
Introduction
This article describes the OAuth2.0 Framework used in the ASP. NET Web API for authorization.
This framework is for checking the authorization and allowing the user limited access to the resource. It is works as security for the resources that are accessed by the user. We use the OAuth2.0 for protecting our ASP. NET Web API.
It provides various methods for accessing the resource on the behalf of the Resource Owner. It gives the services of the end-user that provide the permission of a third party to access the resources without knowing the credentials.
Advantages of OAuth2.0
- Allows the user limited access to the resource
- Allows the user access to any resource for a limited duration
- It is a standards-based framework
- Under the OAuth authorization the client cannot see the credentials
Disadvantages of OAuth2.0
- There is sn unspecified format for the token.
- There is more complexity for writing an authorization server.
Some rules for defining the OAuth2.0
- Resource Owner: Grants the permission for accessing the resource.
- Client: Accesses the request.
- Resource server: Hosts the resource.
- Authorization server: Provides the authentication to the owner that issues the tokens for accessing the client.
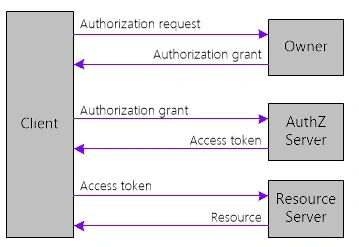
- First the client sends the request to the owner and receives permission for accessing the resources but this permission is for limited scope and limited duration.
- After getting the permission the client access the token from the Authorization server.
- Now the client accesses the resource.
We defined in above the flow of OAuth2.0, but how OAuth works is not exactly like that because it depends on the client type.
- By using the OAuth we protect our Web API.
- It provides Authentication to the client for accessing the protected resources.
- It depends on the client type for using the OAuth authorization
Join the conversation! Your thoughts help the community grow.