
StageFright- A word of fear for Android devices?
Figure 1- Stage
Introduction
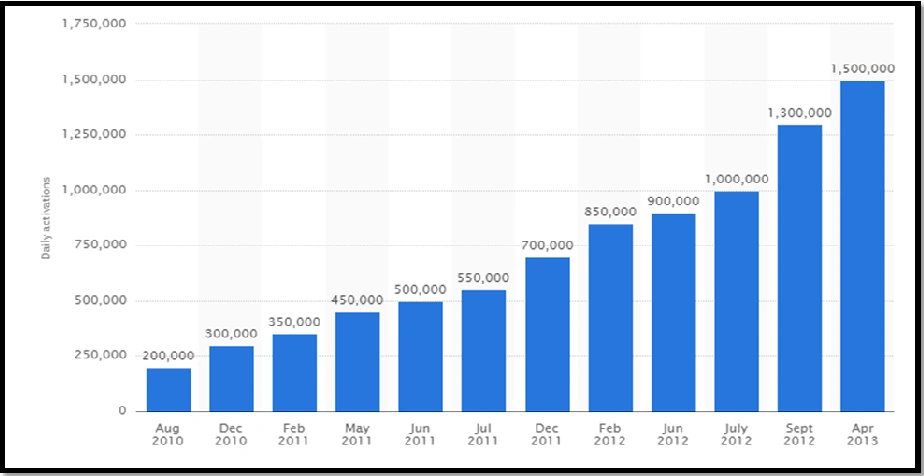
Figure 2- Rising
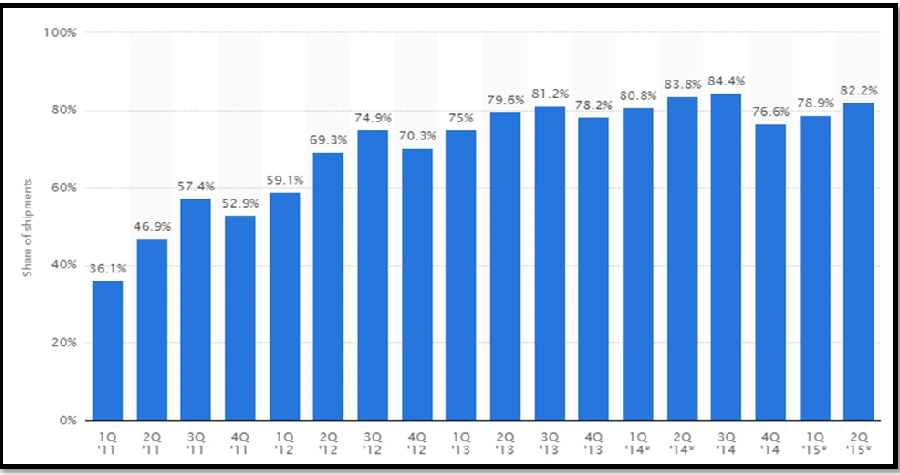
Figure 3- Showing global
What is StageFright?
“Stagefright is the collective name for a group of software bugs that affect versions2.2 ("Froyo") and newer of the Android operating system, allowing an attacker to perform arbitrary operations on the victim device through remote code execution and privilege."
A top Android researcher Joshua Drake (@jduck), who is working in Zimperium’s zLabs team, discovered the most vulnerable bug in Android OS escalation and was publicly announced for the first time on July 27, 2015. Zimperium’s team is also calling it ‘Mother of all Android Vulnerabilities’, as it impacts 95% or 950 million of all Android devices and does not require any interaction with the victim.
It is most vulnerable because a hacker can get into your android device without interacting with the victim and can operate remotely or silently and you can never guess that you are the victim if you are not a techie and smart enough. Here below is a StageFright demo video released from Zimperium’s zlabs by Joshua Drake. In this video, Joshua Drake is showing how a hacker can get into your device and what type of privileges he/she can escalate.
See StageFright Demo Video
Two versions are their which exploits an Android device:
Who discovered StageFright?
Why StageFright is the most vulnerable bug?
StageFright Versions
- StageFright 1.0
- StageFright 2.0
StageFright 1.0
You can get an idea about StrageFright 1.0 from the following link:
Avast blog for StageFright 1.0
According to Zimperium, a pair of recently discovered vulnerabilities make it possible for an hacker or attacker to get into Android device with an MP3 or MP4 like file, so when the metadata for that file is previewed by the OS that file could execute malicious code via the website or a human being. In the middle of an attack it is built specifically for delivering these malformed files, this code could be executed without the user interaction.
“Zimperium claims to have confirmed remote execution and brought this to Google's attention on August 15. In response, Google assigned CVE-2015-3876 and CVE-2015-6602 to the pair of reported issues and started working on a fix.”
Is your Android device vulnerable for StageFright 2.0
According to Zimperium “In one way or another, yes. CVE-2015-6602 refers to a vulnerability in libutils, and as Zimperium points out in their post announcing the discovery of this vulnerability it impacts every Android phone and tablet going back as far as Android 1.0. CVE-2015-3876 affects every Android 5.0 and higher phone or tablet, and could theoretically be delivered via a website or man in the middle attack.”
I am talking about CVE but what actually CVE is?
CVE stands for Common Vulnerabilities and Exposures (CVE) system provides a reference-method for publicly known information-security vulnerabilities and exposures.
CVE-ID Syntax
There was an old version of CVE syntax also which is a little bit different from the below-defined syntax.
CVE prefix + Year + Arbitrary Digits [ New syntax implemented from Jan 1st, 2014 ]
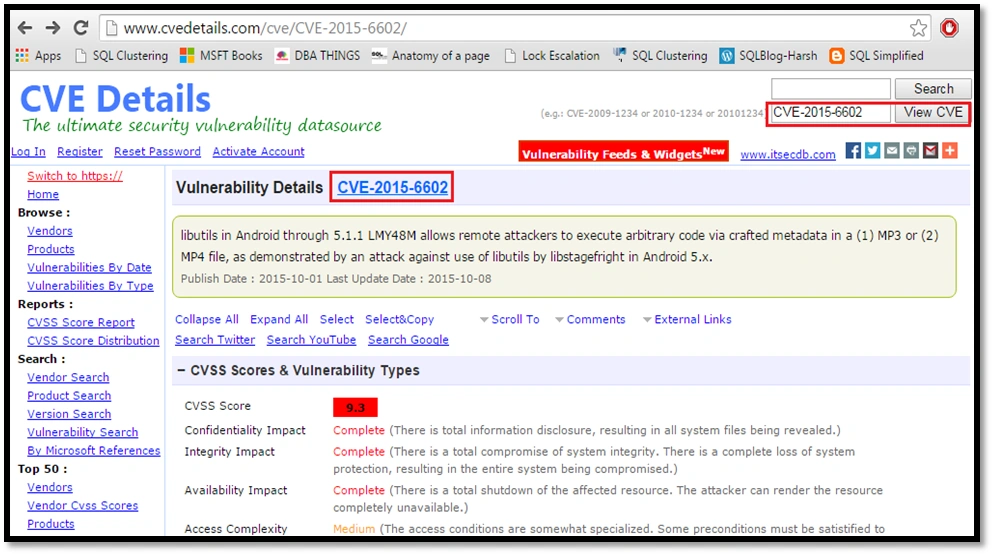
So if someone says what is CVE-2015-6602, then we can easily describe it, that it is a threat ( Common Vulnerability Exposure ) which came in the year 2015 having CVE-ID 6602. By putting CVE-2015-6602 on the website: www.cvedetails.com you can get more information, resources and links for the particular CVE. I hope that now CVE-YYYY-NNNN is not a new thing for you. You are aware and you can answer if someone asks.
 The following figure is clearly showing the difference between old CVE syntax and new CVE syntax.
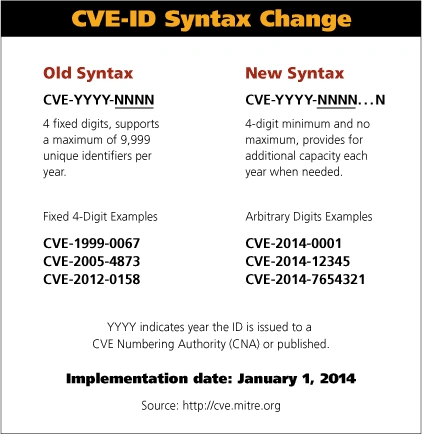 Image Source- mitre.org
StageFright 2.0
What CVE is?
Figure 4- Fetching
Figure 5- Showing
How to know my Android device is affected by StageFright 2.0 vulnerability?
How to fight with StageFright 2.0 until the patch arrives?
- Try to not download mp3 or mp4 from your web-browsers.
- Avoid public networks.
- Secure your wi-fi connection with strong passwords.
- Pay attention that where and what you are browsing
Santhakumar MunuswamyPosted Oct 18, 2015, 2:21 AM
Good one
Priyaranjan K SPosted Oct 17, 2015, 1:21 PM
Thanks for the share ...
Rajeesh MenothPosted Oct 17, 2015, 6:08 AM
Thanks for sharing!
Mukesh KumarPosted Oct 17, 2015, 12:50 AM
Great job
Nilesh JadavPosted Oct 17, 2015, 12:11 AM
Good one sir !!
Harshad PansuriyaPosted Oct 17, 2015, 12:08 AM
Nice one