
The Issue
My organization was using AD connect to sync users to Azure AD. The below settings were in use:
- Password Hash Sync
- Password Write Back
- ms-DS-ConsistencyGuid
In a ransomware attack, all domain controllers AD sync server and backups are compromised. We rebuilt the domain controllers with same forest and domain names, but the SID has changed. We have recreated the users with same display name and UPN, as on the previous domain controller.
We are utilizing M365 for Teams, emails, etc.
Objective
Restore the syncing of AD users to Azure AD from the newly created domain.
Note
On-prem requirements are not covered here.
Solution
The solution will be executed in four steps:
- Converting Ad Synced users into Cloud Users.
- Hard match for the users that we need to resync
- Running Pilot Sync Batch
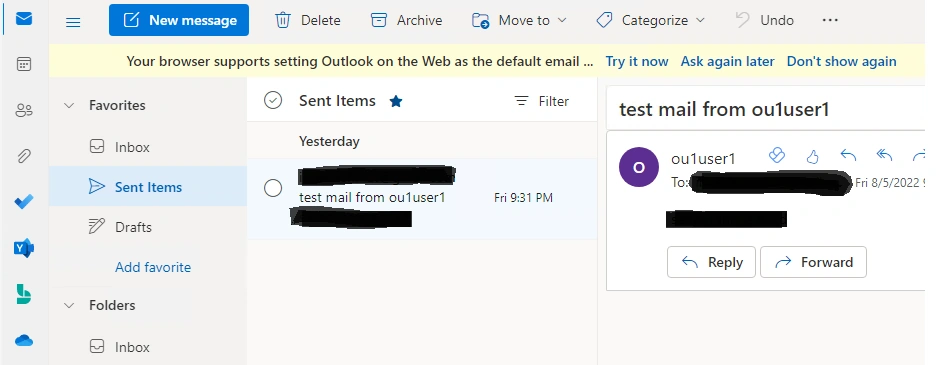
- Examining restored M365 services
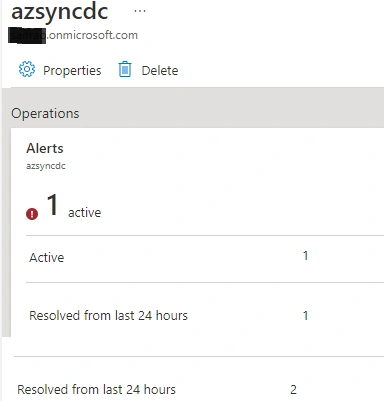
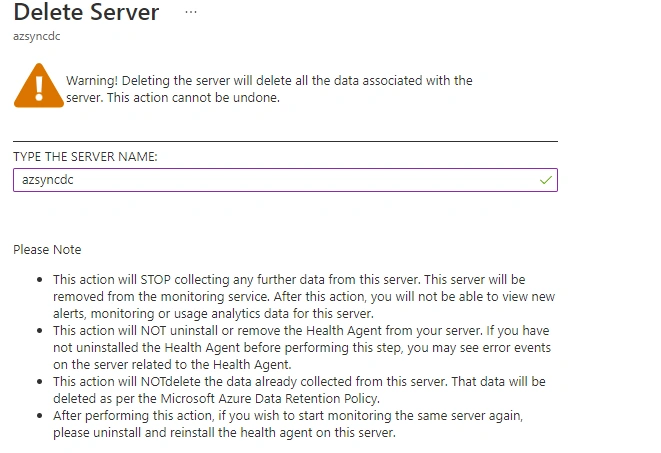
- Cleanup of old AD Connect Servers
Before starting the resolution steps, it's important to check and verify the existing state of the Azure AD Tenant.
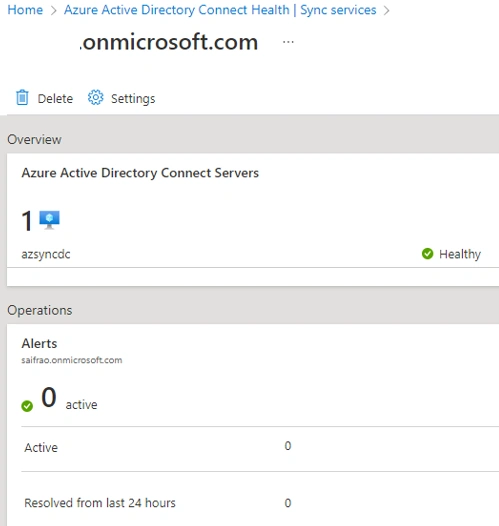
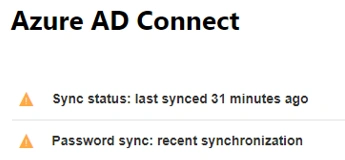

Converting Ad Synced users into Cloud Users
In this step, we will disable the AD sync service via PowerShell. This can take up to 72 hours, depending on the numbers of users. In the lab setup for five users, this was done in under 10 minutes.
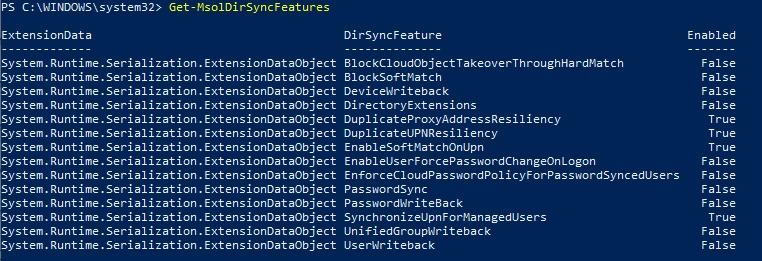
Set-MsolDirSyncEnabled –EnableDirSync $false
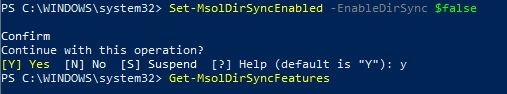
After some, depending on the numbers of users ad synced, accounts will be converted to cloud only accounts, and they will keep the same password as the ones of on-prem when they were last synced.

Hard match for the users that we need to be resynced
Install the new AD connect server with required setting and then proceed for Hard Match. Hard match can also be done prior to the new AD connect Installation.
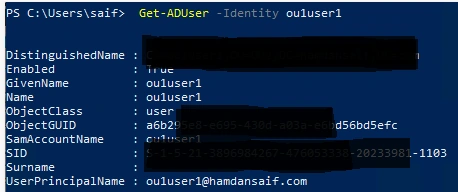
On the Domain Controller, open a PowerShell window and run the command Import-Module Active Directory.
Run the command Get-ADUser -Identity “Enter Local AD logon ID in these quotes." Once you run the above command, you should see an output like this:



Join the conversation! Your thoughts help the community grow.