
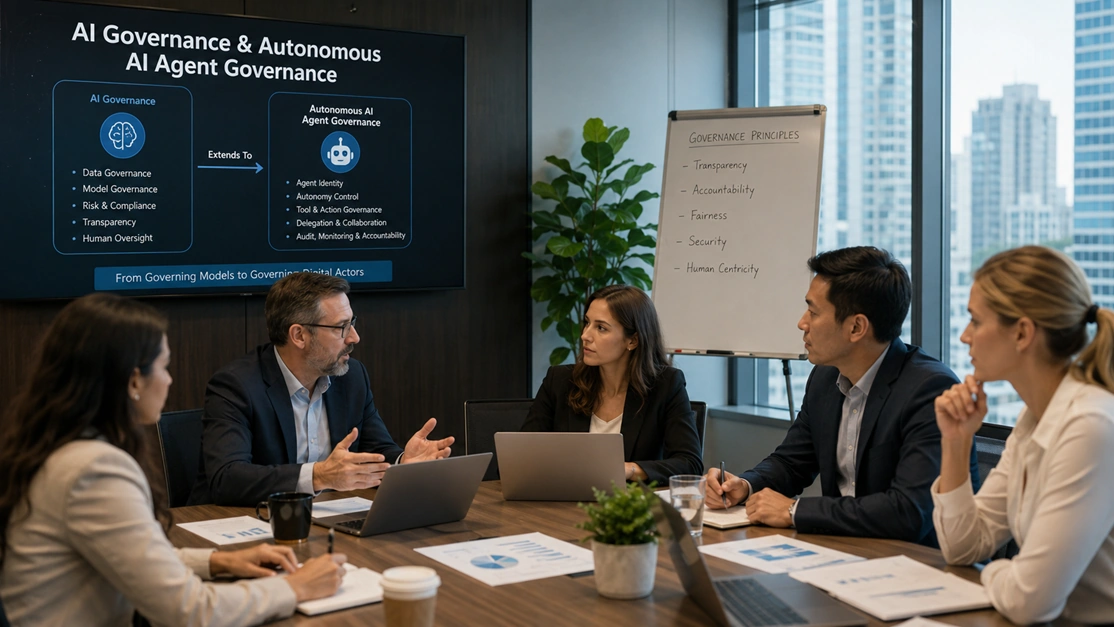
Artificial intelligence governance has traditionally focused on controlling how AI systems are designed, trained, deployed, and monitored. The central questions have been familiar: Is the model fair? Is the data protected? Can the output be explained? Is the system compliant with policy and regulation?
Autonomous AI agents introduce a fundamentally different governance problem.
A conventional AI system primarily generates an output. An autonomous agent can interpret an objective, create a plan, choose tools, access enterprise systems, delegate work, execute transactions, modify data, communicate with people, and continue operating over time.
That difference changes governance from model oversight into operational control.
AI governance asks whether an intelligent system is trustworthy. Autonomous AI agent governance must also determine what the system is authorized to do, how far it may proceed, who remains accountable, and how its actions can be stopped, reconstructed, challenged, or reversed.
The relationship between the two is therefore not competitive. Agent governance is an extension of AI governance—but one that requires a much stronger execution, identity, and accountability layer. Here is from Gate2Asi AI's AgentFactory (Formerly AlpineGate AI's) point of view:
1. What Traditional AI Governance Covers
AI governance is the organizational framework used to ensure that AI systems are developed and used responsibly, securely, lawfully, and in alignment with business objectives.
Its core concerns typically include:
Data quality, privacy, and provenance
Model accuracy, robustness, and reliability
Bias, fairness, and discrimination
Explainability and transparency
Security and misuse prevention
Regulatory and policy compliance
Human oversight
Lifecycle monitoring
Vendor and third-party risk
Ownership and accountability
This framework is essential. Without it, enterprises risk deploying systems that are opaque, inconsistent, insecure, or misaligned with organizational values.
However, traditional AI governance often assumes a relatively contained interaction:
Input → Model → Output → Human decision
The human is expected to evaluate the result and decide what happens next.
Autonomous agents change that sequence.
2. How Autonomous Agents Change the Operating Model
An autonomous AI agent does not merely answer a question. It may act as a persistent digital worker.
The execution pattern becomes:
Objective → Interpretation → Planning → Tool selection → Action → Observation → Adaptation → Further action
An agent may:
Read emails and documents
Query production databases
Generate and execute code
Update enterprise records
Initiate workflows
Create financial analyses
Contact customers or employees
Coordinate with other agents
Escalate exceptions
Request approval
Continue until an outcome is reached
The agent is no longer only a source of information. It becomes an active participant in enterprise operations.
This creates a new governance unit: not just the model, but the agentic execution loop.
The governance system must therefore control the complete chain of behavior, including the objective, plan, tools, permissions, actions, dependencies, handoffs, evidence, and final outcome.
3. The Fundamental Difference: Intelligence Versus Agency
The clearest distinction is between intelligence and agency.
AI governance governs intelligence.
It focuses on whether a system can produce reliable, responsible, and compliant judgments or outputs.
Autonomous AI agent governance governs agency.
It focuses on whether a system may act, what it may act upon, under which conditions, and with what degree of autonomy.
A language model may suggest that a supplier payment should be suspended. An autonomous financial agent may actually place the payment on hold.
A model may recommend changing a customer account. An agent may update the CRM, notify the customer, open a service ticket, and trigger an approval workflow.
The risk is no longer limited to an incorrect answer. It includes an incorrect or unauthorized action.
This is why agent governance must treat autonomy as a controlled privilege rather than a default capability.
4. AI Governance and Agent Governance Are Layered
Autonomous agent governance should not replace traditional AI governance. It should sit on top of it.
A useful layered model is:
Layer 1: Model Governance
This governs the underlying AI capabilities.
It addresses:
Model selection
Accuracy and robustness
Bias testing
Prompt-injection resistance
Output filtering
Training-data concerns
Model versioning
Provider risk
Evaluation and benchmarking
Layer 2: Agent Governance
This governs the digital actor created around the model.
It addresses:
Agent identity
Assigned role
Scope of responsibility
Permitted tools
Data access
Delegation rights
Memory boundaries
Runtime policies
Approval requirements
Escalation rules
Layer 3: Work Governance
This governs the specific assignment being executed.
It addresses:
Business objective
Acceptance criteria
Budget
deadline
Risk classification
Required evidence
Human checkpoints
Segregation of duties
Completion conditions
Layer 4: Operational Governance
This governs what happens during execution.
It addresses:
Runtime monitoring
Tool-call authorization
Transaction controls
Rate limits
exception handling
rollback
suspension
audit logging
incident response
Layer 5: Outcome Governance
This governs the final business result.
It addresses:
Verification
independent review
approval
evidence retention
impact assessment
accountability
post-execution monitoring
This layered structure is necessary because a well-governed model can still be embedded in a poorly governed agent, and a properly configured agent can still be given an unsafe assignment.
5. Identity Becomes a Governance Requirement
Traditional applications typically operate through user accounts, service identities, or application credentials. Autonomous agents need the same rigor.
Every enterprise agent should have a persistent and verifiable identity.
That identity should define:
Who created the agent
Who owns it
Which organizational unit it represents
What role it performs
Which systems it may access
Which data classifications it may handle
Which actions it may execute
Which other agents it may instruct
Who is accountable for its behavior
An anonymous agent with broad credentials is not a governed digital worker. It is an uncontrolled automation risk.
Agent identity should therefore function much like an enterprise employee identity, but with stronger machine-enforced restrictions.
The organization should be able to answer:
Which agent performed this action, under whose authority, for which objective, using which tools, based on which evidence?
If this cannot be answered, the system is not operationally governable.
6. Autonomy Must Be Granted by Level
Autonomy should not be treated as binary.
A practical governance framework defines levels of permitted independence.
Level 0: Advisory
The agent produces recommendations only. A human performs every action.
Level 1: Assisted Execution
The agent prepares actions, but each material step requires human approval.
Level 2: Bounded Autonomy
The agent may execute low-risk actions within predefined limits.
Level 3: Conditional Autonomy
The agent may complete end-to-end workflows when policy conditions are satisfied, but must escalate exceptions.
Level 4: High Autonomy
The agent may plan, delegate, and execute complex work across systems with continuous monitoring and enforceable controls.
Level 5: Enterprise Autonomous Operation
Multiple agents coordinate persistent business functions with dynamic planning, governance, evidence capture, and human intervention available at strategic control points.
The higher the autonomy level, the stronger the governance requirements must become.
Increasing autonomy without increasing observability, authorization, and accountability produces unmanaged operational risk.
7. Human-in-the-Loop Is Not Enough
Many organizations assume that adding a human approval step automatically creates safe AI governance.
It does not.
Human approval can become superficial when:
Too many requests are generated
Reviewers lack context
Explanations are incomplete
Decisions must be made too quickly
The agent has already completed irreversible steps
Approval interfaces encourage automatic confirmation
Responsibility is unclear
Effective agent governance requires more precise human control models.
These may include:
Human-in-the-loop: A human must approve a defined action.
Human-on-the-loop: The agent may operate, but a human continuously supervises and can intervene.
Human-over-the-loop: Humans define policies, limits, and escalation rules governing many autonomous executions.
Human-at-the-boundary: Human approval is required only when an action crosses a risk, financial, legal, or operational threshold.
The objective is not to insert humans into every step. It is to place human judgment at the points where it provides real control.
8. The Governance Object Must Be the Entire Decision Chain
Autonomous behavior is often distributed across multiple components:
A user instruction
A system prompt
A planning model
A retrieval system
Enterprise data
External tools
Agent memory
Policy engines
Other agents
Human approvals
A failure may not originate in the model itself. It may result from a combination of incomplete instructions, stale data, excessive permissions, weak tool validation, or incorrect inter-agent delegation.
Governance must therefore capture the full decision chain.
A governed agent action should preserve evidence of:
The original objective
The interpreted requirements
The plan
The data consulted
The policies applied
The tools invoked
The approvals obtained
The intermediate decisions
The final action
The observed result
Any deviations or exceptions
Join the conversation! Your thoughts help the community grow.