
Introduction
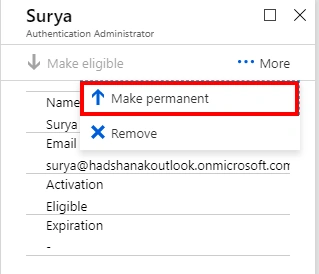
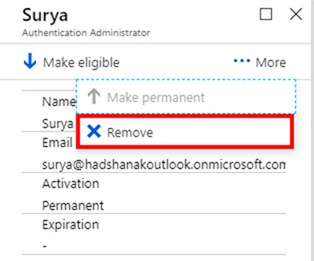
The Azure AD Privileged Identity Management (PIM) administration likewise permits Privileged Role Administrators to make permanent administrator role assignments. Also, Privileged Role Administrators can make clients eligible for Azure AD administrator roles. An eligible admin can activate the role when they need it, and after that their permissions expire once they're finished.
With Azure Active Directory (Azure AD), a global administrator can make permanent Azure AD administrator job assignments. These role assignments can be made utilizing the Azure portal or utilizing PowerShell commands.
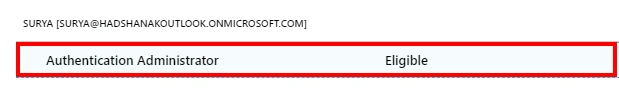
User eligible for a role
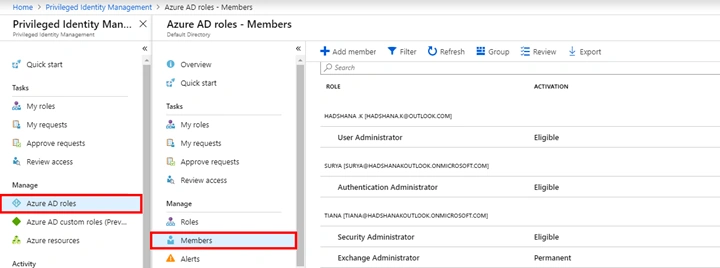
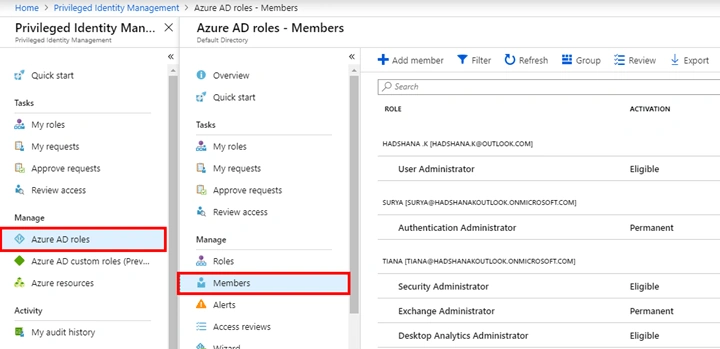
Sign in to the Azure portal. Open Azure AD Privileged Identity Management.
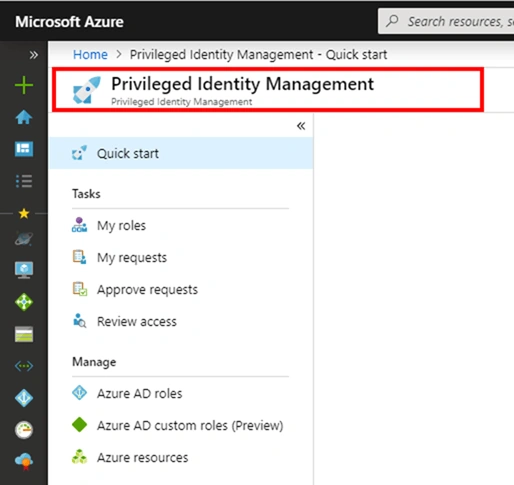
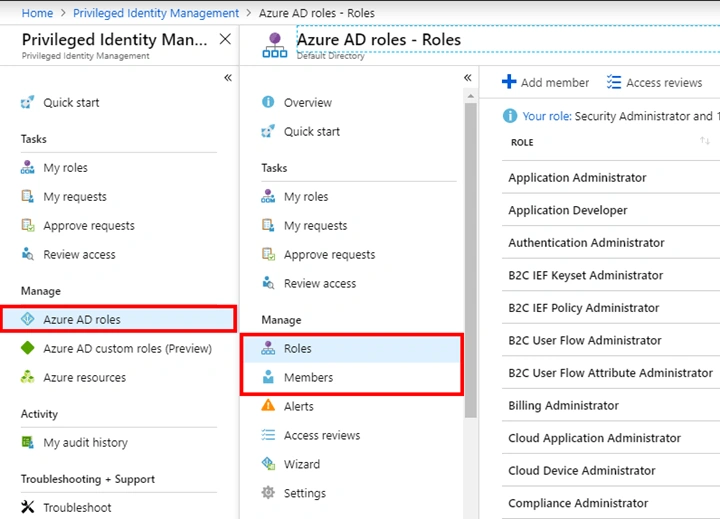
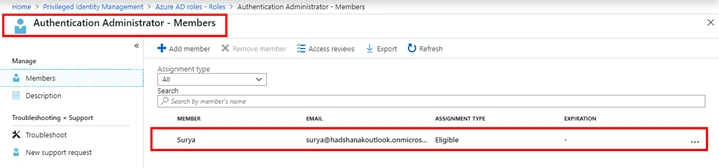
After that, click Azure AD Roles and then, click Roles or Members.
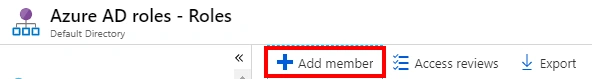
Then, click "Add member" to add managed members.
After that, click "Select a role". Click a role you want to manage, and then click "Select".
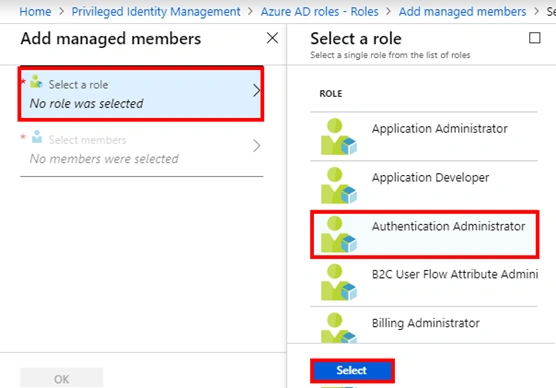
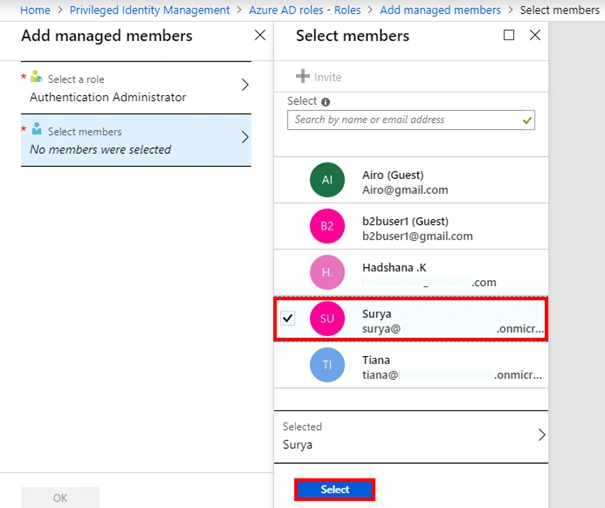
And the second option is to click "Select members" and select which users you want to assign to the role and then click "Select".
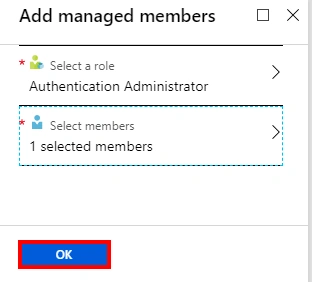
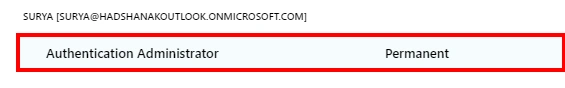
Finally, in "Add managed members" section, click OK to add the user to the role.
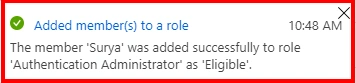
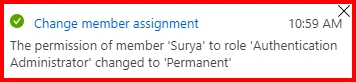
See the notification of "Successfully added".
Sana KamalPosted Sep 15, 2019, 3:10 AM
Good Explanation
Chittaranjan SwainPosted Aug 24, 2019, 4:27 AM
Nice article.
Arvind KatariaPosted Aug 23, 2019, 12:23 AM
Nice ...!!!
Rushi MehtaPosted Aug 22, 2019, 11:26 PM
Keep sharing information on Azure DevOps
Viknaraj ManogararajahPosted Aug 22, 2019, 10:00 AM
Another Nice article about Azure AD...keep sharing more...