
Introduction
Managed Identities provide a secure way for Azure resources to authenticate to Microsoft Entra ID without storing credentials. However, when a Managed Identity needs to call Microsoft Graph APIs, it must be granted the appropriate Microsoft Graph application permissions.
Recently, I was working on an Azure Function that needed to retrieve users and groups from Microsoft Entra ID using Microsoft Graph and, at the same time, assign Microsoft Graph permissions, such as User.Read.All and Group.Read.All to the Managed Identity, I encountered an Authorization_RequestDenied error despite having Application Administrator privileges.
In this article, I'll walk through:
How to retrieve Microsoft Graph App Role IDs
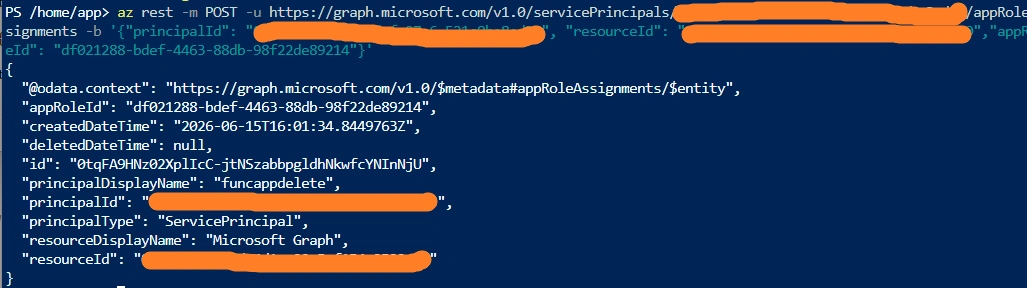
How to assign Microsoft Graph application permissions to a Managed Identity
What Microsoft Entra role is required to perform the assignment
Understanding Microsoft Graph App Roles
When assigning Microsoft Graph application permissions programmatically, you cannot use the permission name directly.
Instead, Microsoft Graph expects the corresponding App Role ID.
The App Role ID can vary and should always be retrieved directly from the Microsoft Graph Service Principal.
Retrieve the Microsoft Graph Service Principal Object ID
Microsoft Graph uses the following Application ID:
00000003-0000-0000-c000-000000000000
The assignment operation requires the Object ID of the Microsoft Graph Service Principal in your tenant.
az rest `
    --method GET `
    --uri "https://graph.microsoft.com/v1.0/servicePrincipals?`$count=true&`$filter=appId eq '00000003-0000-0000-c000-000000000000'" `
    --headers "ConsistencyLevel=eventual" "Content-Type=application/json" `
    --query "value[0].id" `
    --output tsv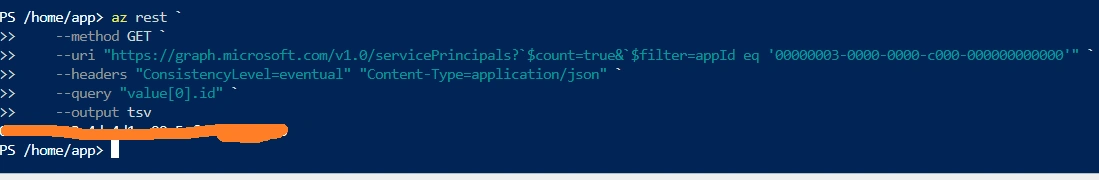
Note the value of the id property.
Get the App Role ID for User.Read.All and Group.Read.All
The following command filters the response and returns only the User.Read.All permissions:
$response = az rest -m GET -u "https://graph.microsoft.com/v1.0/servicePrincipals(appId='00000003-0000-0000-c000-000000000000')?`$select=appRoles" | ConvertFrom-Json
$response.appRoles |Where-Object { $_.value -eq "User.Read.All" } |Select-Object id, value, displayName
$response.appRoles |Where-Object { $_.value -eq "Group.Read.All" } |Select-Object id, value, displayName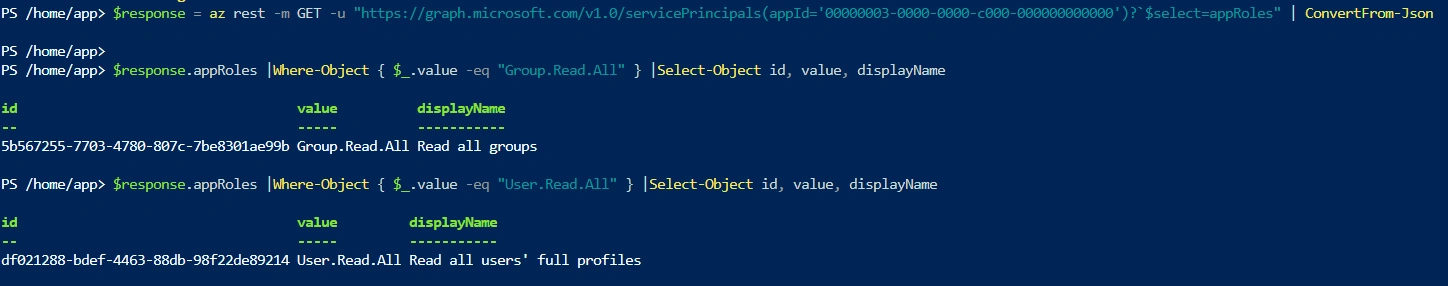
Join the conversation! Your thoughts help the community grow.