
Introduction
By default, when somebody creates an Azure SQL Server, an Administrator with SQL Authentication is made as a matter of course. In any case, for authoritative purposes, it is a best practice to utilize Azure Active Directory.
Azure Active Directory is a cloud directory and identity management administration service having various qualifications for every application.
That is the reason using Azure AD for Azure SQL Database or other Azure applications is necessary. You can bring together the verification management. It also provides more high security to your Azure SQL Databases.
Learn how to
- How to create an Azure Active Directory user
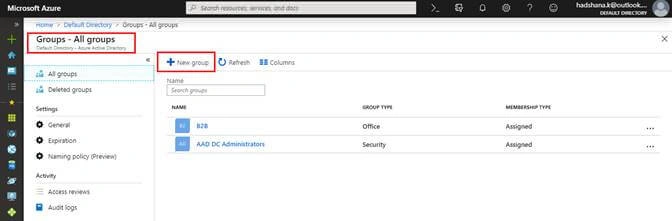
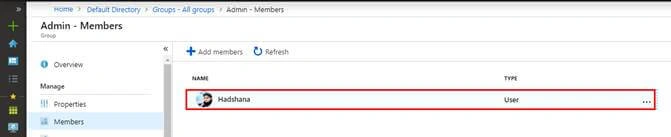
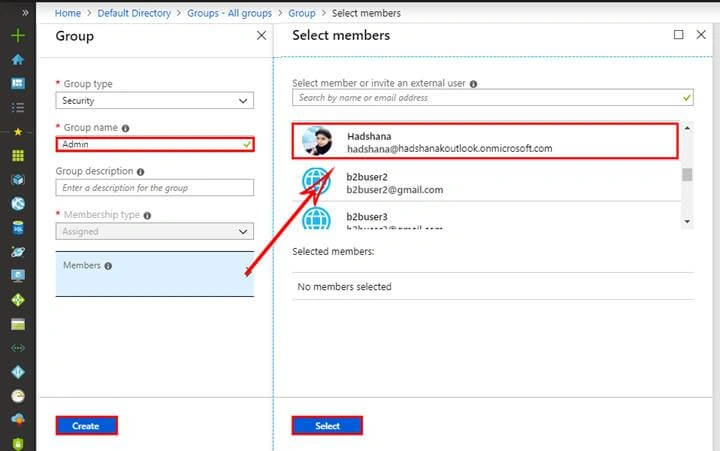
- How to create an Azure Active Directory group and assign the user group
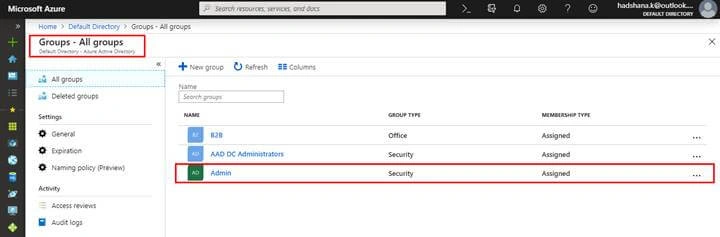
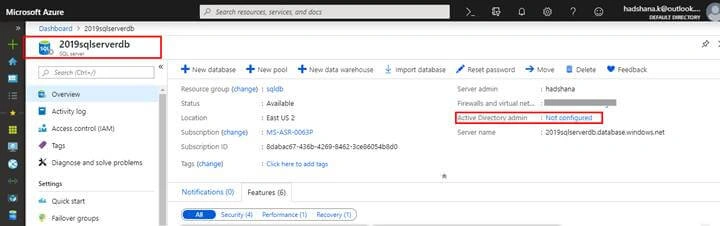
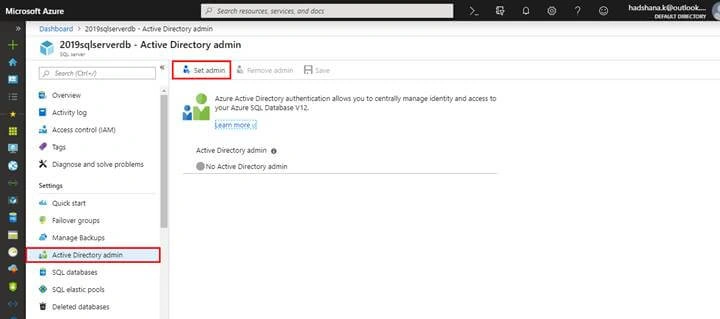
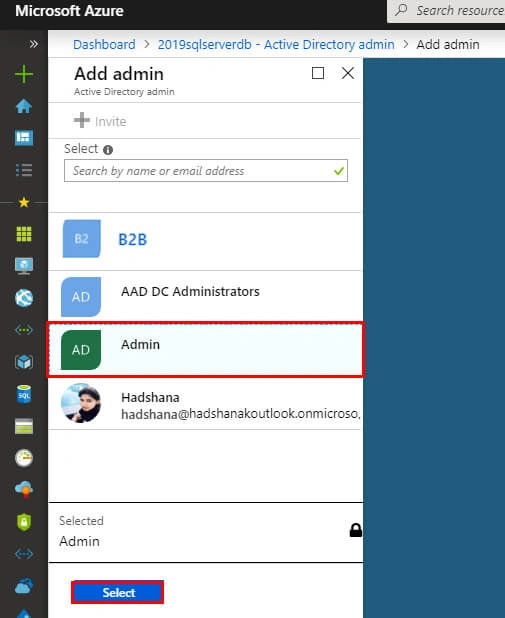
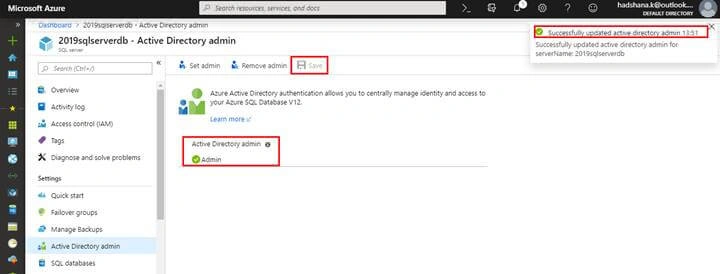
- How to add an Azure Active Directory user/group as an Azure SQL Administrator
- How to add Azure Active Directory users to Azure SQL Database
Requirements
- A subscription to Azure
- An Azure SQL Server and database created (if you do not have that, you can create a new one)
Getting started
By default, an Azure AD directory is already created. We will first create the user and then add it to a group. Finally, we will add it to the Azure SQL Database.
Step 1 - Create an Azure Active Directory User
In the Azure Portal, click on the account and select your directory.
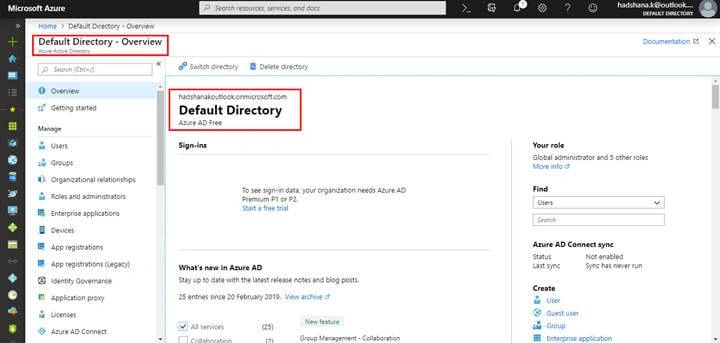
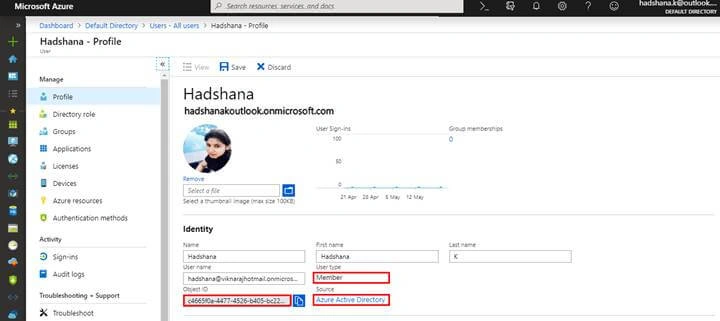
The directory information like users and groups in Azure will show. In this example, the directory is hadshanakoutlook.onmicrosoft.com.
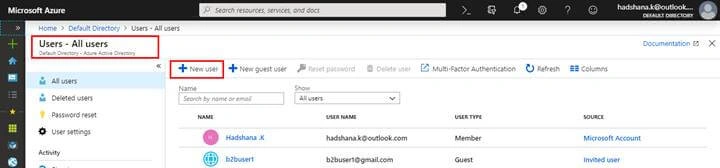
To create a user, in the Azure Active directory, press the > and look for Users and Groups. Go to All users and click the “New user”.
After that, add/fill-in the information about the user like the name, user name, first name, last name, work information, etc.
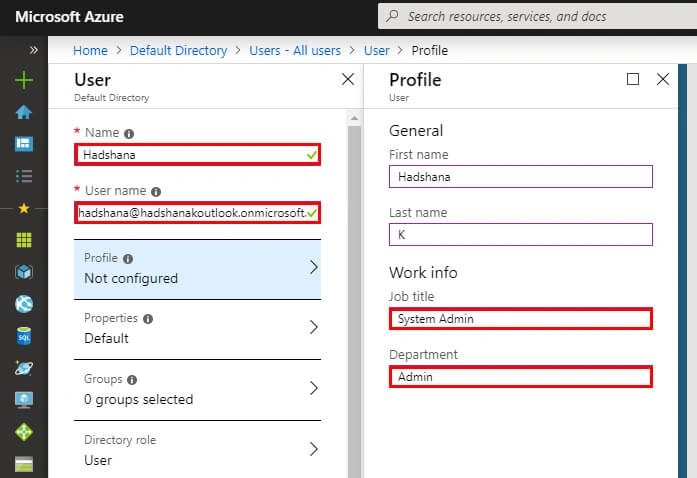
Assign roles like the User, Global, and Limited administrator role. Once you select the options, click "Create".
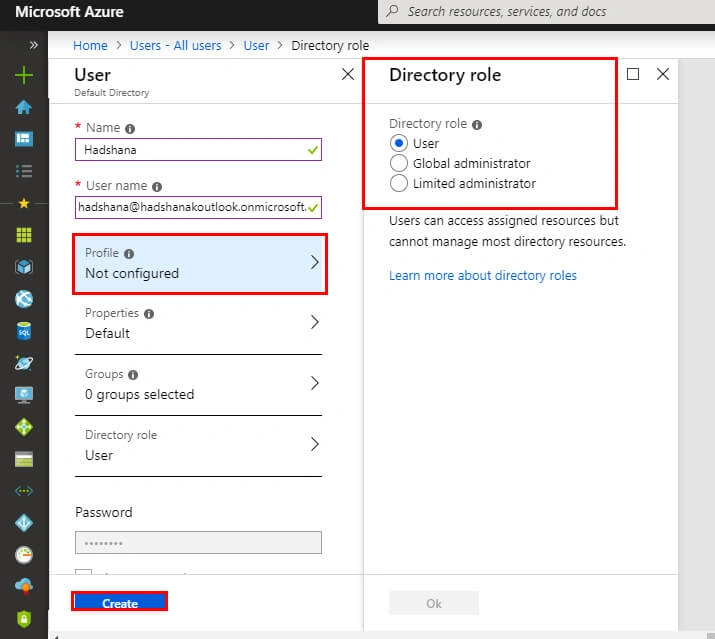
Roles
- A user can access the resources but cannot manage the directory resources.
- A global administrator can do anything except changing the password of another administrator.
- The limited administrator is limited to the role assigned. It can be a password administrator, service administrator, SharePoint administrator, security administrator, etc.
The new user is created successfully.
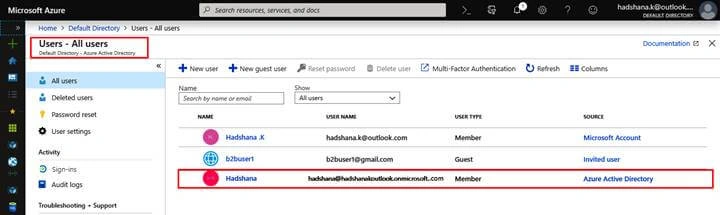
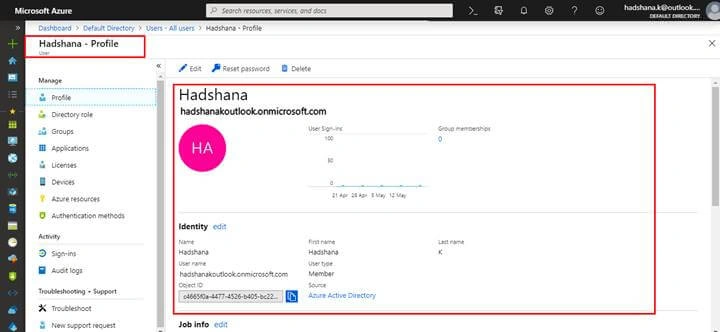
After this, if you click on the new users, you will see the options to reset the password or to delete it. By default, the user is created with a temporary password that you are forced to change after the first login to the portal.
Ankur VishwakarmaPosted May 14, 2020, 8:45 AM
I want to add a Azure Security Group to a specific Azure SQL database in a SQL instance where there are several DBs are hosted. Is it possible? How, if yes.
Viknaraj ManogararajahPosted Jun 22, 2019, 12:17 AM
Nice Article, thank you for sharing!!!
Sana KamalPosted Jun 21, 2019, 10:10 PM
Nice Article.