
Introduction
Most ASP.NET Web applications have file upload functionality where users can upload files and those files are saved on a server or blob storage. But without performing anti-virus scanning or other content checking against the uploaded file, attackers could target other users of the application by uploading malware to the server.
The application should perform filtering and content checking on any files that are uploaded to the server. Files should be thoroughly scanned and validated against an antivirus scanner with up-to-date virus signatures before being made available to other users. Any files flagged as malicious should be discarded or deleted immediately.
To achieve this, we will use an open-source antivirus engine called ClamAV via nClam NuGet package, a pure .NET client to ClamAV.
This article demonstrates how we can perform secure and effective file scanning using ClamAV antivirus.
Prerequisites
The ClamAV server should be up and running on a specific port. In case, you want to run the ClamAV server in localhost, you can follow the subsequent steps below.
Running ClamAV on localhost using Docker Image
This step is optional if you already have the ClamAV server. Here I used the docker image as the simplest and easiest way to run it.
ClamAV demon is a Dockerized open-source antivirus image. Let’s follow below simple steps below to install and run on localhost via default TCP port 3310. I am assuming you have Docker Desktop's latest version installed and running on your PC.
Execute the below commands from the command prompt.
docker run -d -p 3310:3310 mkodockx/docker-clamav:alpine
docker run -d -p 3310:3310 mk0x/docker-clamav
docker ps
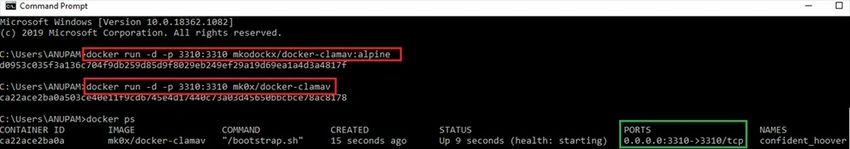
The ClamAV Server is now set up!
For more details, you can check here.
Implementing ClamAV antivirus scan on uploaded files in .NET application
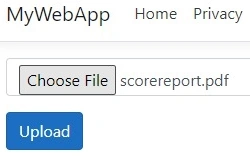
Now we are ready to run on-demand scans and anything from code using nClam. To demonstrate an example, here I created a simple file upload UI in ASP.NET Core MVC Web application (you can have a similar ASP.NET website in WebForms or MVC with file upload input) where we will browse and upload different types of files like PDF, IMAGE, ZIP, DCOX, etc.
The Approach
- Install the nClam NuGet package.
- Add ClamAV server and port to the config file.
- Read file from File upload and convert to byte array.
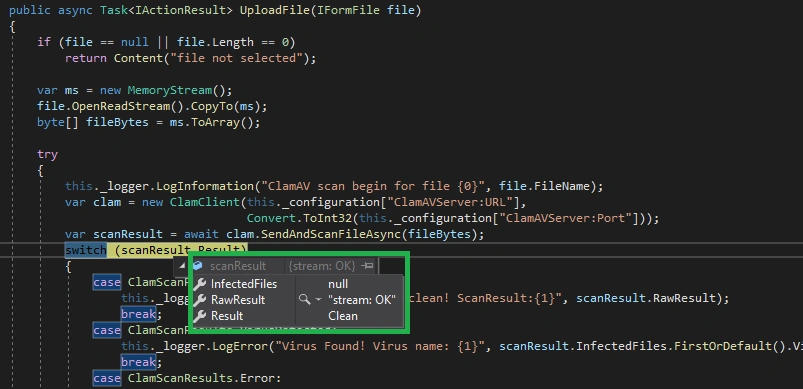
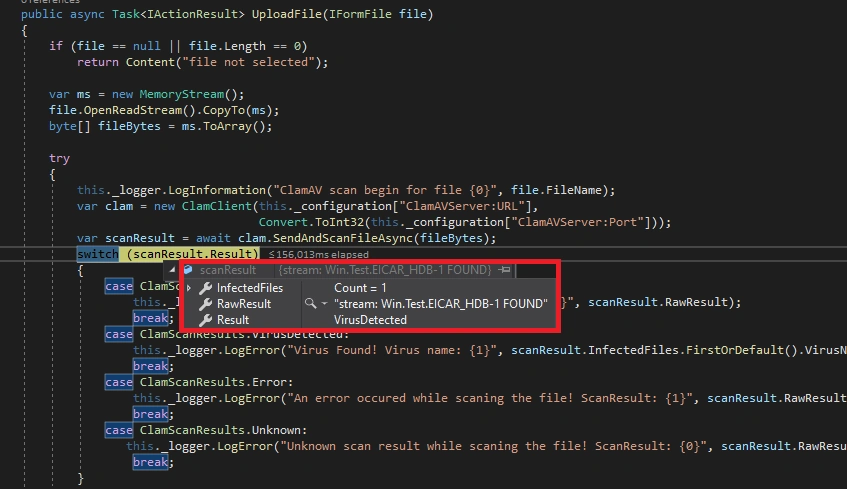
- Scan file byte array against ClamClient and validate ClamScanResult object.
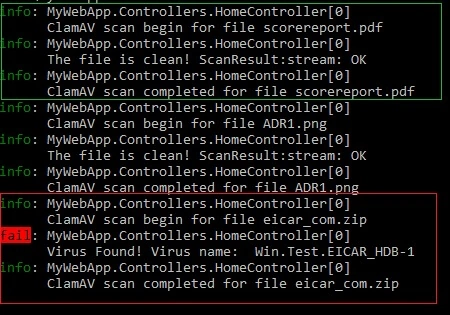
- Test ClamAV scan against a valid file
- Test ClamAV scan against an Anti Malware test file
Step 1. Install nClam NuGet package
Install below NuGet package from the NuGet package manager into your project.
<PackageReference Include="nClam" Version="4.0.1" />
Step 2. Add ClamAV server and port to appsettings.json.
{
  "ClamAVServer": {
    "URL": "localhost",
    "Port": "3310"
  }
}
David MillerPosted May 22, 2024, 2:31 PM
Use to use ClamAV, but it's just sooooo slow... plus detection rates are awful compared with commercial engines :( Since then I've used commercial AV APIs, Verisys (https://www.ionxsolutions.com/products/verisys-virus-api) more recently, but also Trend Micro Cloud One for enterprise projects.
Luke PerrinPosted Apr 9, 2021, 3:52 PM
Why are you running two AV images? I get an error saying the port is already in use if i do that.
Agostino ArcasensaPosted Apr 3, 2021, 7:51 PM
We're using nClam nugget on our netcore 5 app, running via pm2 on Debian 10.We've installed docker engine and created a ClamAV container on port 3310, but when we try to scan a file via our netcore app an error occours: Message: Unable to write data to the transport connection: Broken pipe. Stack: at nClam.ClamClient.SendStreamFileChunksAsync(Stream sourceStream, Stream clamStream, CancellationToken cancellationToken) It seems the ClamAV container is crashing for some reason every time the app tries to communicate with it (after the error the container is no more in the container list showed via docker ps). What are we missing?