
Introduction
This article covers the comparison between TDEA algorithm and Rijndael also known as Advance Encryption Standard(AES)
TDEA Algorithm
- Description of TDEA algorithm
- Considerations for the use of TDEA algorithm
- Security of TDEA algorithm
- Recommendations for Reducing the risk
Rijndael Algorithm
- Origin of Rijndael Algorithm
- Why AES replaced TDEA algorithm
- High-level Description Rijndael Algorithm
- Decryption Process
- Stability under attack
TDEA Algorithm
Description of TDEA Algorithm
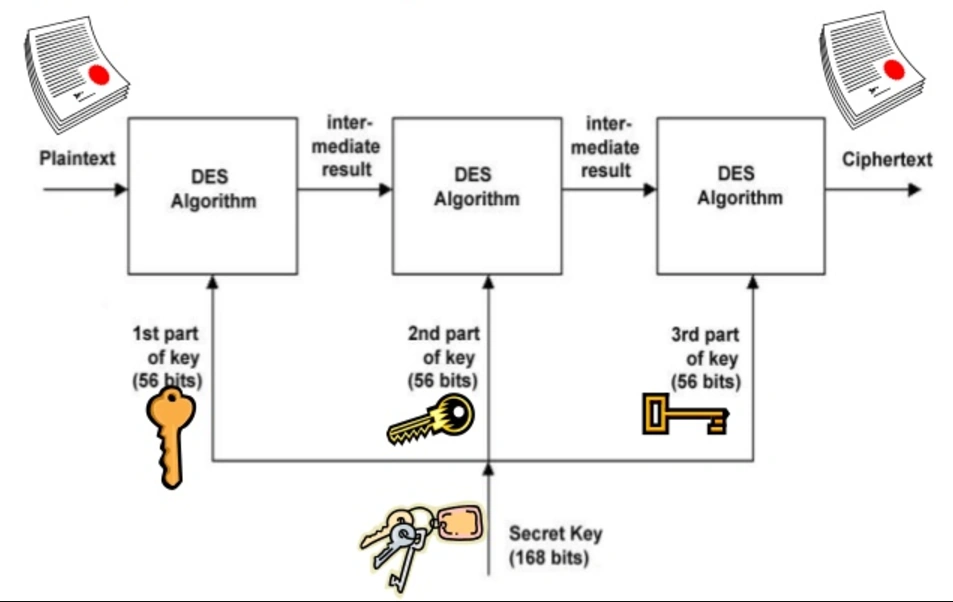
Triple Data Encryption Algorithm became designed to cope with the failings that were found in DES set of rules without creating a completely new cryptosystem. Data Encryption Standard (DES) set of rules makes use of a 56-bit key and it is not efficient enough to encrypt touchy information. In order to overcome this flaw, Triple DEA Algorithm was introduced that extends the DES set of rules with the aid of applying the set of rules three times in succession. The blended key length is consequently 56*3 =168 bit key length. Despite creating the algorithm secured by way of the usage of three instances greater secured key but this also slows down the algorithm as it takes 3 instances more time compared to DES set of rules.
Considerations for use of TDEA Algorithm
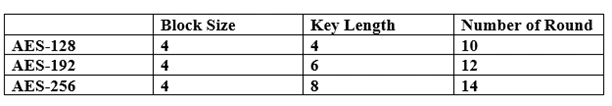
This set of rules is used by older running systems and older protocols. Up to this point systems are now the usage of AES (Advanced Encryption Standard) also named Rijndael Algorithm as it's miles lots efficient as compared to TDEA algorithm in phrases of block size, key length, a wide variety of rounds and key scheduling.
“Sweet 32” take advantage of is ranked as a medium chance by using the Common Vulnerability Scoring System(CVSS), so in this example, the presence of TDEA algorithm could be suggested “failure”
In addition to that, the idea of “robust cryptography” is based totally on the attractiveness of NIST authoritative bodies. Once it's miles disallowed with the aid of the authoritative bodies, it will not be considered as sturdy cryptography.
Security of TDEA Algorithm
As TDEA algorithm having 3 unbiased keys carries 168 bits key length but because of an attack named “meet-in-the-middle-attack”, the safety that it ensures is only 112 bits. The meet-in-the-middle-attack(MITM) is a popular cryptographic attack in opposition to encryption techniques that depends on performing multiple encryption operations in a sequence. That is the primary purpose why TDEA set of rules can be compromised and brute-forced through an attacker with 256 space and 2112 operations.
The short block size of 64 bytes makes the TDEA algorithm makes it vulnerable if it makes use of the equal keys to encrypt massive amounts of data.
The number of blocks with one key bundle has an effect on the safety of TDEA set of rules. To observe cryptographic protection one key bundle shall now not be used.
Recommendations for reducing the risk
The recommendation for reducing the chance is to disallow the usage of TDEA algorithm as it's miles now not an up to date cipher suite that will be backdoor for exploitation. So it's far suggested the use of AES set of rules having a block size of at least 128 bits and key duration of 128 bits that makes it a secured and up to date cipher suite. I Will talk in the latter part of this paper. Some measures that taken will reduce the threat of the current TDEA set of rules: 1. Using a more potent cipher suite, encrypt records at software layer. 2. Regularly converting the TDEA key
Rijndael Algorithm
Origin of Rijndael Algorithm
The algorithm changed into created by way of the cryptologists, Joan Daemen and Vincent Rijmen. The word Rijndael was derived from their surnames. Rijndael has its origins in Square, an encryption algorithm previously designed by the collaboration of both cryptologists, but became intended to enhance upon that in advance try in accordance with three principles that guided the process,
- Defense to all recognized attacks
- Efficiency and speed of the supplied code on a number of computing systems
- Design’s Simplicity
Introduction
Rijndael Algorithm also called Advance Encryption Standard(AES). Rijndael is a family of Ciphers having distinctive keys and block sizes. This set of rules has become chosen to update the DES Algorithm through the National Institute of Standards and Technology(NIST).It is a symmetric key algorithm that means similar key might be used for each both encryption as well as decryption processes. It is based on a layout principle. Unlike its predecessor DES,it doesn’t use Feistel Network.
2.1 Why AES replaced the TDEA algorithm
One of the major requirements by NIST( National Institute of Standards and Technology(NIST) for the replacement of the TDEA algorithm was that It had to be efficient enough to be implemented in both implementations that are hardware as well as software.
Join the conversation! Your thoughts help the community grow.