
In this article, we are going to learn how can we implement VNet Peering across different Azure Active Directory Tenants. VNet Peering allows you to connect two virtual networks created by using different deployment models.
Normally we are using a VPN gateway for connecting different subscriptions from Virtual Network to Virtual Network. At the same time, we can use VNet Peering to connect virtual networks in the same Azure subscription or different subscriptions, as long as they share the same Azure AD tenant.
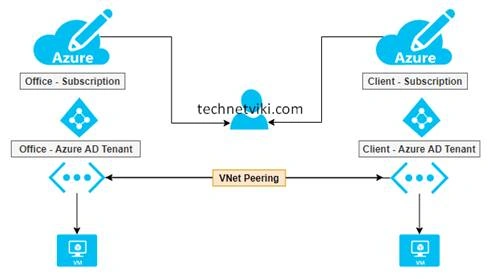
Before configuring the VNet peering we need to add the Client AD Tenant user to our Azure AD, so invite them using the Azure AD.
Step 1
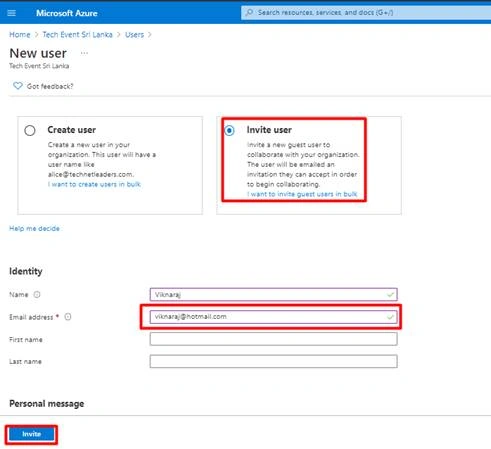
In the Azure Active Directory, select the Users under the management, in the Users page Click + New user, then select Invite user finally enter the user email address and click the Invite button.
Step 2
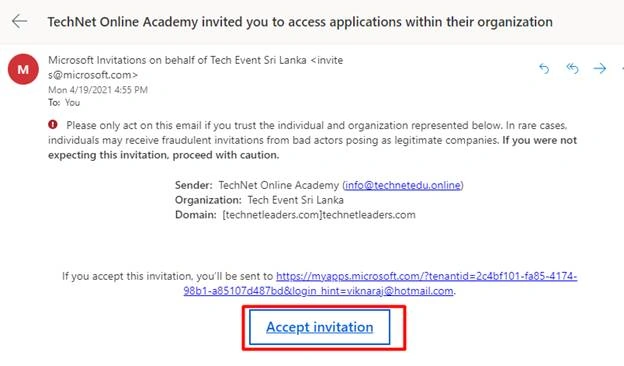
In the client email, we can find that the Azure AD initiation, so click Accept Invitation.
Step 3
After accepting the Invitation, Sign out of the Azure portal and Sign in Again, we can now find the new directory added to our Azure portal.
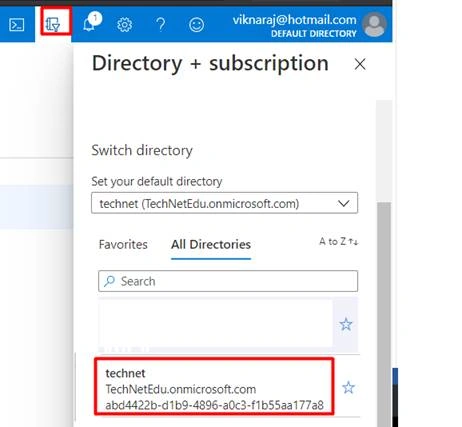
Step 4
Repeat the same process (Step 1 to Step 3) for another Azure AD Tenant.
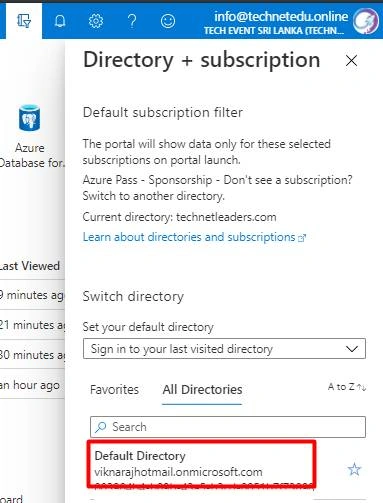
Step 5
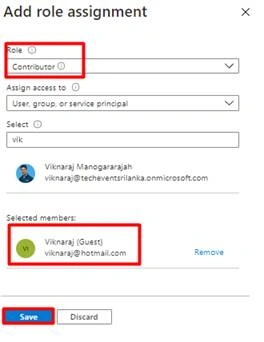
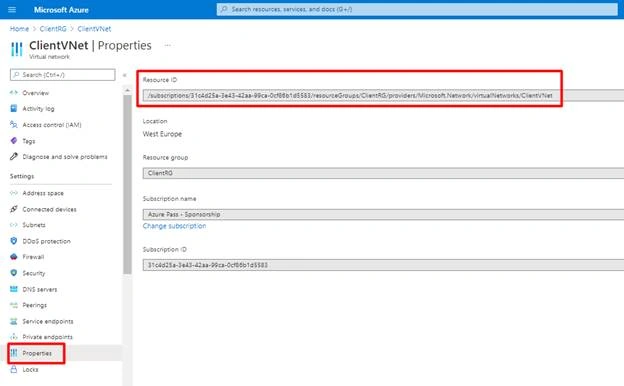
Now we have to assign permission to the Invited users. In the Azure Resource Group create the Role assignment using the Access Control (IAM), select the role like Contributor or Network Contributor, and then select the user and click Save.
Siva JPosted Aug 11, 2022, 1:54 AM
Is it possible to access resource groups across different tenants (directories) to create private endpoint for servers using VPN GW from different tenant - Thanks in advance
Neeraj AilPosted Feb 20, 2022, 5:19 PM
Thanks for the article Viknaraj. What is the purpose or scenario of creating a vpn gateway then?
Hadshana KamalanathanPosted Sep 28, 2021, 4:24 AM
Excellent Article;