
In this article, I will explain how we can create an Azure Key vault; add secrets to an Azure Key Vault, and how we can add a web app service principal into the vault access policy using simple ARM templates.
Before beginning to create an ARM template, the assumption here is that you should have a basic understanding of the structure of ARM templates and you already have a resource group.
The Context
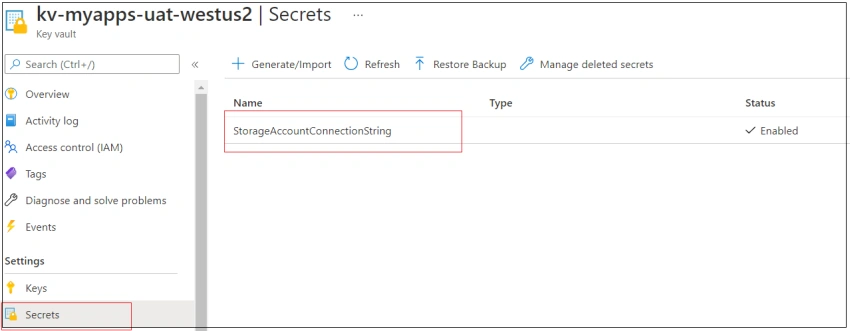
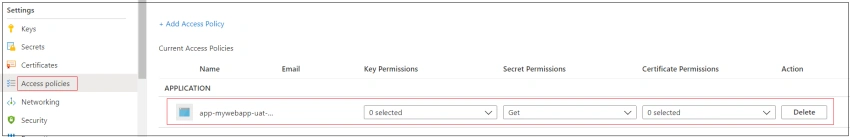
For demonstration purposes, we will create a web app with a system-assigned identity and we will add web app service principal id to the key vault access policy. Similarly, we will create a storage account to demonstrate how we can easily add storage account connection string into key vault secret.
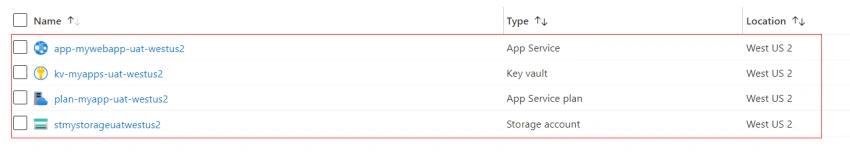
We will create the below resources in this article for better understanding purposes.
| Resource Name | Type reference |
| Key Vault | Microsoft.KeyVault/vaults |
| Key Vault - Secret | Microsoft.KeyVault/vaults/secrets |
| Storage Account | Microsoft.Storage/storageAccounts |
| Web App | Microsoft.Web/sites |
| App Service Plan | Microsoft.Web/serverfarms |
The below image represents the resources dependency of our ARM templates which we will build in subsequent steps.
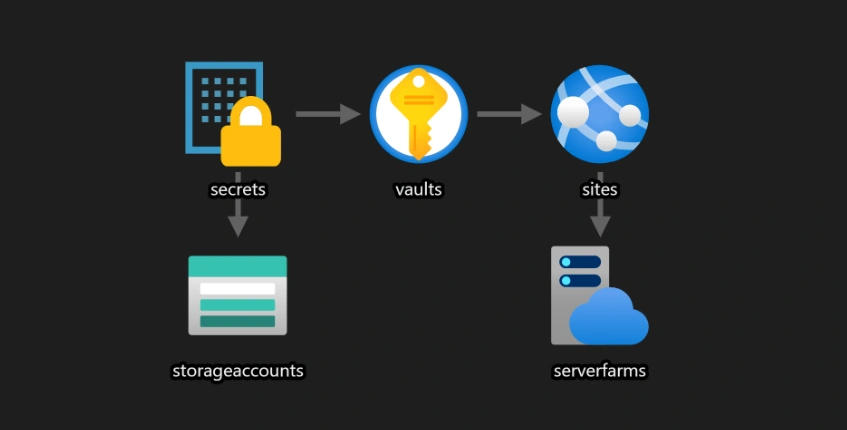
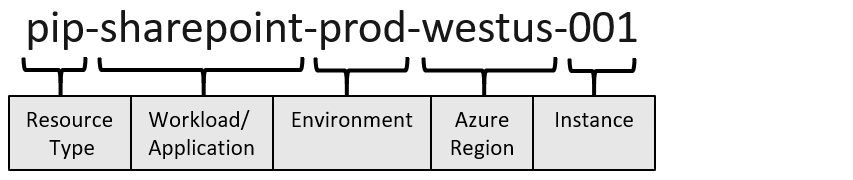
And we will follow the below-maiming convention while creating resources using ARM. Image has been referred from Microsoft documentation.
Let’s build our template step by step for each resource.
Parameters & Variables
We are taking environment name as Input and in the variable, we will concatenate environment name with resources we are creating.
"parameters": {
    "envName": {
        "defaultValue": "uat",
        "type": "String"
    }
}, "variables": {
    "tenantId": "[subscription().tenantId]",
    "appServicePlanName": "[concat('plan-myapp-',parameters('envName'),'-',resourceGroup().location)]",
    "webAppName": "[concat('app-mywebapp-',parameters('envName'),'-',resourceGroup().location)]",
    "storageAccountName": "[concat('stmystorage',parameters('envName'),resourceGroup().location)]",
    "keyVaultName": "[concat('kv-myapps-',parameters('envName'),'-',resourceGroup().location)]"
},
Creating Key Vault with Vault Access Policy
To create a Key Vault with an access policy, we add the following resource to the ARM template.
First, we will create a web app with an app service plan.
{
    "type": "Microsoft.Web/serverfarms",
    "apiVersion": "2018-02-01",
    "name": "[variables('appServicePlanName')]",
    "location": "[resourceGroup().location]",
    "sku": {
        "name": "S1",
        "tier": "Standard",
        "size": "S1",
        "family": "S",
        "capacity": 1
    },
    "kind": "app"
}, {
    "type": "Microsoft.Web/sites",
    "apiVersion": "2018-11-01",
    "name": "[variables('webAppName')]",
    "location": "[resourceGroup().location]",
    "dependsOn": ["[resourceId('Microsoft.Web/serverfarms', variables('appServicePlanName'))]"],
    "kind": "app",
    "identity": {
        "type": "SystemAssigned"
    },
    "properties": {
        "name": "[variables('webAppName')]",
        "httpsOnly": true,
        "serverFarmId": "[resourceId('Microsoft.Web/serverfarms', variables('appServicePlanName'))]"
    }
},
Join the conversation! Your thoughts help the community grow.