
Part-I of this article covered cryptography in the context of encryption. This part continues from where part-I left. It assumes that the reader understands the purpose of encryption, knows about the two types of encryption namely asymmetric encryption and symmetric encryption and the fundamental differences between them. It also assumes that the reader understands encryption-decryption classes in System.Security.Cryptography namespace and the stream based encryption model in. NET framework class library (FCL).
This part discusses developing secured applications using cryptographic solutions like digital envelops, digital signature and digital certificates, with .NET. It uses nine sample visual studio projects (DigitalEnvelopCode.zip) to explain the cryptographic concepts and their support in .NET. It also includes a full-fledged sample for securing .NET remoting application using .NET FCLs cryptographic classes. Part-I of this article is available at
Cryptography in Microsoft.NET Part I: Encryption
Cryptography
In a distributed environment, for a server to trust the data it received from its peer-server there are three issues that must be addressed, namely
- Authenticity: There should be a way for the receiving server to ascertain that the message came from its peer-server only.
- Data Integrity: There should be a way for the receiving server to verify that the message was not altered in the way after it was sent by its peer-server.
- Non-repudiation: There should be a way for the receiving server to protect it from the sender falsely denying the knowledge of the message sender sent.
For a server to send any data confidently to its peer-server there is one more issue that must be addressed in addition to the above, namely
- Privacy: There should be a way for the sending server to ensure that the message will be secure during transit, and except for the intended receiving server no one would be able to read it.
Cryptography, with its encryption and hashing algorithms, solves all these issues.
Hashing Algorithm
Hashing is the focal point of almost all the cryptographic solutions for real world security problems. It is a method of reducing a message (string) of any length to a message (string) of fixed length, called message digest, in such a way that it is computationally infeasible to
- Find two different messages producing same digest (collision)
- Find a message from the given message digest (retracing)
Even when one bit is changed in the input message about half of the bits in the message digest gets changed.
In cryptographys terminology, the mathematical functions that do this are called One-Way Hash Functions or Hash Algorithms. They are also called compression functions, message-digests, and fingerprints. The variable-length message that the hash algorithms take is called pre-image and the fixed-length output string that they produce is called hash value.
Hash algorithms are characterized by the size of the hash value that they produce. Following are some of the popular hash algorithms and the size of the hash value that they produce.
- MD2, MD4 and MD5 128 bits
- SHA and SHA-1 160 bits
MD2, MD4 and MD5 are Message Digest algorithms developed by Ron Rivest of RSA Labs (http://www.rsasecurity.com/) for use in digital signature applications. Of these MD2 is used in 8 bits systems. MD4 and MD5 are used in 32 bit systems. MD5 is slower than MD4, but it is more secure
Secure Hash Algorithm (SHA/SHA-1) was developed by National Institute for Standards and Technology (NIST) (http://www.nist.gov/). SHA-1 is more secure than SHA. Until now no cryptanalysts could find a single collision for SHA-1.
SHA256/384/512
On October 12, 2000, NIST proposed three new secure hash algorithms to succeed SHA-1. These algorithms, SHA-256, SHA-384 and SHA-512, are intended to meet the three security levels of the recently proposed Advanced Encryption Standard, which comes with three key sizes: 128 bits, 192 bits and 256 bits.
Advanced Encryption Standard is implemented in RijndaelManaged class. SHA algorithms are implemented in SHA256Managed, SHA384Managed and SHA512Managed classes in System.Security.Cryptography namespace.
Keyed Hash Algorithm
A keyed hash algorithm is a secret-key dependent one-way hash function. It is very similar to the normal hash algorithms (called free functions) except that, in this the hash value is a function of the pre-image and a secret-key. Only someone who knows the secret-key can verify the hash. Hence it is used to do message integrity checks for messages exchanged between two parties that share a secret-key. It can also be used to authenticate files shared between users or even a single user can use it to verify that viruses did not alter the files.
Since the hash generated by keyed hash algorithm is used as a secured checksum, it is known as message authentication code (MAC), or data authentication code (DAC).
MAC can be created out of a hash algorithm or a block symmetric encryption algorithm. Following are some of the commonly used MACs
- MACs using block encryption algorithm:
MAC with RC5, MAC with CAST-128, MAC with TripleDES and MAC with CBC (AES).
- MACs using hash algorithm:
Keyed-hash MAC (HMAC) with MD5, HMAC with SHA-1, HMAC with RIPEMD-128 and HMAC with RIPEMD-160.
Cryptographic Applications
Although asymmetric encryption, symmetric encryption and hash functions are powerful by themselves, any real world application of them in enterprise is possible only by their combination.
To epitomize their strengths,
- Asymmetric Encryption: Encrypting data with a key (public-key or private-key) of a key-pair makes it computationally infeasible to decrypt without using the complement key in the same key-pair.
- Symmetric Encryption: Encrypting data with a key (secret-key) makes it computationally infeasible to decrypt without using the same key. Also symmetric encryption is faster than asymmetric encryption.
- Hashing: Produces a unique message digest of known fixed size and it is computationally infeasible to get the original data from Message Digest.
Following applications of cryptography uses some or all of the above algorithms.
- Digital Envelope
- Digital Signature
- Digital Certificate
For discussing these applications, assume three users (or servers) named Alice, Bob and Eve. Alice is the sender of the message, Bob is the receiver of the message and Eve is the malicious eavesdropper. Alice has an asymmetric key-pair with a public-key called PBa and a private-key called PRa. Bob also has an asymmetric key pair with public-key called PBb and private-key called PRb. Since PBa and PBb are public-keys every one, Alice, Bob and Eve, knows them.
Digital Envelope
Digital enveloping is an application in which the sender seals the message in such a way that no one other than the intended recipient can open the sealed message. It uses both content-encryption algorithm (symmetric encryption) and key-encryption algorithm (asymmetric encryption).
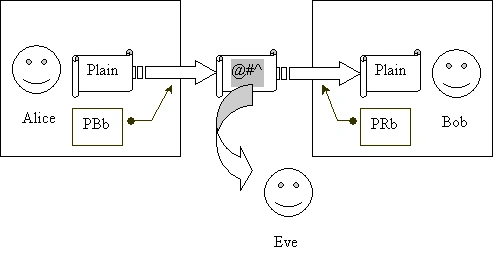
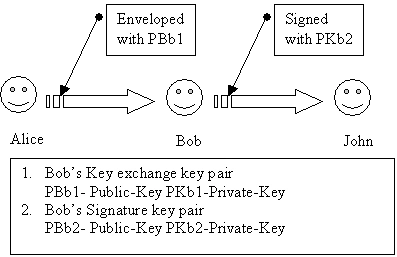
Alice encrypts the message (Plain) with Bobs public-key (PBb) using some asymmetric algorithm and sends the message to Bob. Since the message is encrypted with a public-key, it can be decrypted with complement key in the same key- pair, which is Bobs private-key (PKb) and only Bob knows it. Even though Eve can eavesdrop the ciphertext he wont know what is the actual message that is being sent.
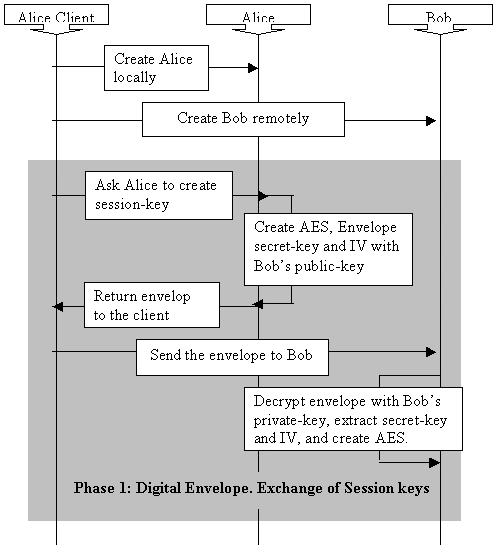
Since asymmetric encryption is slower to do (asymmetric encryption is about 1000 times slower than symmetric encryption), Alice will create a new secret-key in the beginning, encrypt it with Bobs public-key and send it to Bob. For the exchange of actual messages, Alice will use this secret-key to encrypt the message using symmetric encryption.
Digital Signing
Digital Signing is an application in which the sender signs the message in such a way that anyone can verify that the message is from the sender only and no one modified the message after sender signed it. It uses message-digest functions (hash algorithms) and message-digest encryption algorithm (asymmetric encryption).
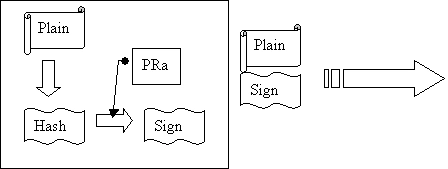
Alice creates the message-digest (hash) for the message (Plain) and encrypts it with her private-key (PRa) to create a digital signature (Sign) of the message. She sends the message along with the signature to the receiver, Bob.
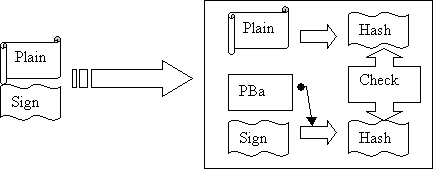
When Bob receives the message-signature pair from Alice, he hashes the message (Plain), with the same hash algorithm that Alice used, to generate a hash, and decrypts the Sign with Alices public-key (PBa) to generate another hash. If both the hashes are same then the message came from Alice only and no one did alter the message in the transit.
If Eve attempts to forge Alice, he would capture the message-signature pair send by Alice and send a different message-signature pair to Bob. Eve can either send a modified message with the same signature that Alice sent, or he can modify the message and create a new signature with his private-key. Bob can identify both, as the hash that he creates from the message wont match the hash that he gets by decrypting the signature using Alices public-key (PAa).
Digital Certificates
The above applications have three loopholes, which are plugged by using digital certificates. Following are those loopholes
- How does Bob know Alices public-key and how can he be sure of it?
- How does Bob know which hash algorithms to use (MD5 or SHA) and what are its parameters?
- How does Box know which encryption algorithms to use (DES or RC2, RSA or DSA) and what are the its parameters?
Digital certification is an application in which a certification authority signs a special message m, containing the name of user and the users public-key in such a way that any one can verify that the message was signed by no one other than the centralized authority. The certificate also has the algorithms used and their parameters.
The typical implementation of digital certification involves signature algorithm that both hashes the message and signs the hash with the private-key, rather than using a message-digest function followed by message-digest encryption algorithm.
This whole solution hinges on Bob trusting the certification authority.
For more details on certification please refer
http://www.verisign.com/resources/gd/buildEcommerce/index.html
Cryptography in Microsoft .NET
Microsoft.NET has classes that extend the cryptographic services provided by Windows CryptoAPI.
System.Security.Cryptography namespace of .NET Framework Class Library (FCL) provides classes for
- Symmetric Encryption
- Asymmetric Encryption
- Hashing
- Digital Signatures
- Digital Certificates
- XML Signatures
Part-I of this article discussed symmetric and asymmetric encryption. This part discuss hashing and signature. Subsequent parts will discuss digital certificates and XML signatures.
Hash Algorithms
Similar to encryption algorithms, hashing algorithms are also implemented using three level inheritance patterns. The root class HashAlgorithm is abstract and it has an overloaded method to compute hash (message-digest) for any message passed either as a byte array or as a stream.
- Computes the hash value for the specified byte array.
byte[] ComputeHash(byte[]);
- Computes the hash value for the specified Stream.
byte[] ComputeHash(Stream);
- Computes the hash value for the specified region of the specified
byte array. byte[] ComputeHash(byte[], int, int);
Only MD5 and SHA1 are available in Windows CryptoAPI. Hence there only two unmanaged hashing classes in FCL, MD5CryptoServiceProvider and SHA1CryptoServiceProvider. All the other hash functions are implemented in the managed class having the standard Managed suffix as in SHA256Managed. However there are two keyed-hash functions implemented in managed class but without the Managed suffix, HMACSHA1 and MACTripleDES. FCL has a managed class implementation also for SHA1.
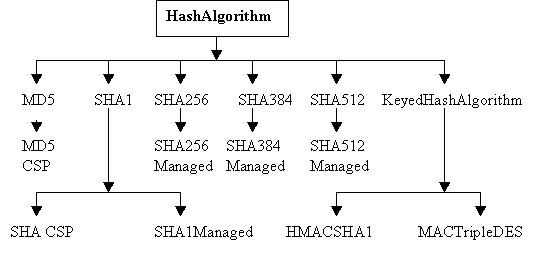
Similar to encryption classes, hash algorithms also can be created either using static create method of the root class or using constructors.
Following snippet creates using the static method
HashAlgorithm hash = HashAlgorithm.Create();
Console.Out.WriteLine("Algorithm : {0}",hash.ToString());
Console.Out.WriteLine("Hash Size : {0} bits",hash.HashSize);
SHA1CryptoServiceProvider is the default algorithm for hashing. Hence the output generated is:
Algorithm: System.Security.Cryptography.SHA1CryptoServiceProvider
Hash Size: 160 bits
Following snippet creates using the constructor
SHA512Managed hash = new SHA512Managed();
Console.Out.WriteLine("Algorithm : {0}",hash.ToString());
Console.Out.WriteLine("Hash Size : {0} bits",hash.HashSize);
The output generated is:
Algorithm: System.Security.Cryptography.SHA512Managed
Hash Size: 512 bits
Following snippet shows how to generate a simple hash for a file. For full source code please refer File Hash project in the attached source code.
//Open the Source file
FileStream fsSource = File.OpenRead(_SourceFilepath);
//Create the default hash algorithm
HashAlgorithm hash = HashAlgorithm.Create();
//Compute the hash
hashbyte = hash.ComputeHash(fsSource);
//close the streams
fsSource.Close();
Keyed Hash Algorithm
FCL has managed implementations for two keyed hash algorithms
- MAC using symmetric encryption algorithm (block): MAC with TripleDES in System.Security.Cryptography.MACTripleDES
- MAC using hashing algorithm: HMAC with SHA1 in System.Security.Cryptography.HMACSHA1
Both the classes take the secret-key in the constructor and as a property.
Following snippet shows creating KeyedHashAlgorithm object using static create
KostadineditedPosted Feb 24, 2012, 8:25 AMEdited Feb 24, 2012, 8:26 AM
Hello I couldn't understand the meaning of this: "The typical implementation of digital certification involves signature algorithm that both hashes the message and signs the hash with the private-key, rather than using a message-digest function followed by message-digest encryption algorithm." Aren't 'signing the hash' and 'message-digest encryption' one and the same thing?!
dhanalakshmi narayanasamyPosted Apr 24, 2009, 3:13 AM
sdsd sds