
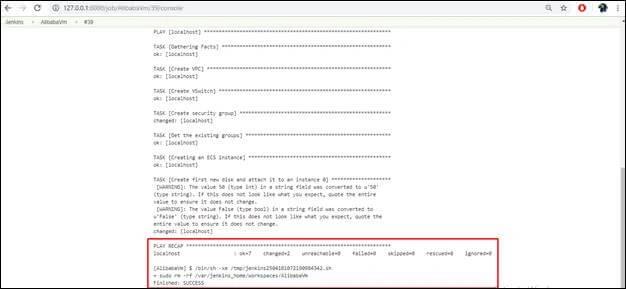
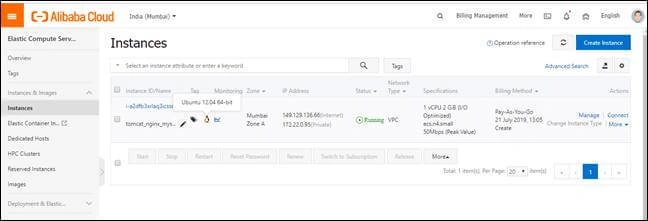
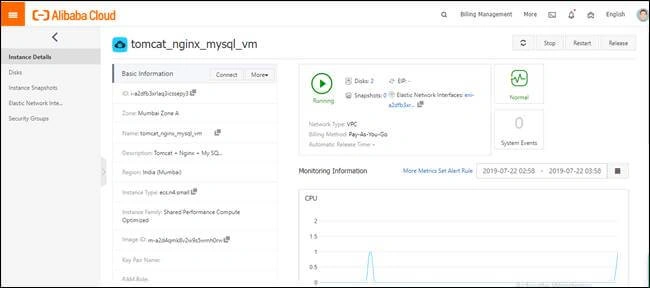
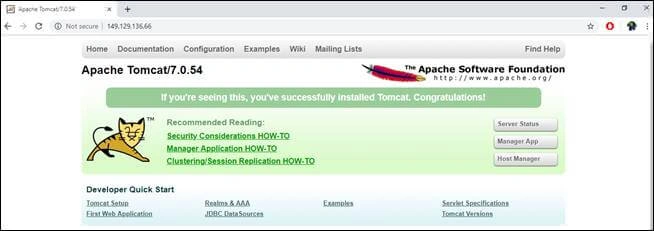
The image consists of Tomcat, Java, MySQL which will be running on an Alibaba Elastic Compute Instance (ECS). Here, Infrastructure as Code (IaC) tool, “Ansible” and an open-source Continuous Integration and Continuous Delivery (CICD) tool, “Jenkins” are being used for provisioning.
Jenkins
It’s an open-source automation server which enables you to reliably build, test, and deploy software as well the infrastructure for an application. Jenkins is a continuous integration build tool which builds and releases application code after any change is made to the code and, pushed to the codebase. It saves development time by running automated testing against the code at every change pushed to the repos.
Firstly, we require a few prerequisite setups to be established to achieve the environment.
Prerequisite
- Jenkins Server (Master only or Master/Slave setup) Link
Once Jenkins server master/slave (agent) environment is established, make sure the agents are up and running fine by checking the status. In my setup, I’m using a master node as Jenkins server and an agent machine for Ansible. If required, you can have only one machine by installing Ansible on the master itself.
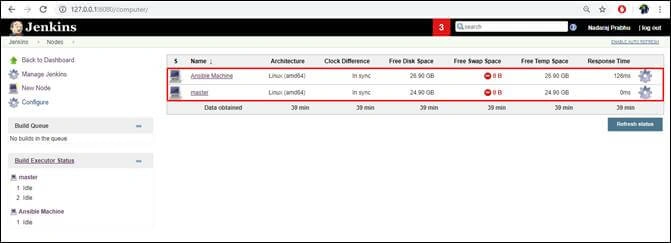
Next, install Ansible Tool in the master and agent machines.
Ansible
Ansible is a powerful tool for IT automation and can be used in a CI/CD process to provision the target environment and to then deploy the application on it. Ansible is cumbersome to maintain and reuse scripts in the long run.
It helps you perform the same set of tasks across different servers/environment from the centralized server where Ansible is installed. Ansible is completely agentless, which is an advantage over other IaC tools like chef, Puppet, etc. It implies no agent needs to be installed on client systems where the automation needs to be taken through provided SSH communication between client and server. All the automation will be easier when there are hundreds of instances in the specified region. Ansible playbooks are written are YAML/YML language.
Ansible’s few important notes
Control node
Machine where Ansible is installed and responsible for servers you are managing.
Inventory
An Ansible inventory file defines the hosts and groups of hosts upon which commands, modules, and tasks in a playbook operate. The file can be in one of many formats depending on your Ansible environment and plugins. It’s used to create project-specific inventory files in alternate locations.
Playbook
Playbooks are Ansible’s configuration, deployment, and orchestration language. They can describe a policy you want your remote systems to enforce or a set of steps.
Install “Ansible” and “Ansible Alicloud Module”
Install Ansible plugin on Jenkins
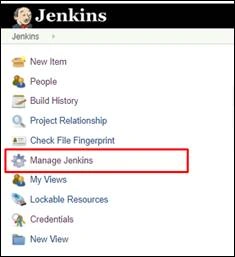
- Click on “Manage Jenkins” in the dashboard.
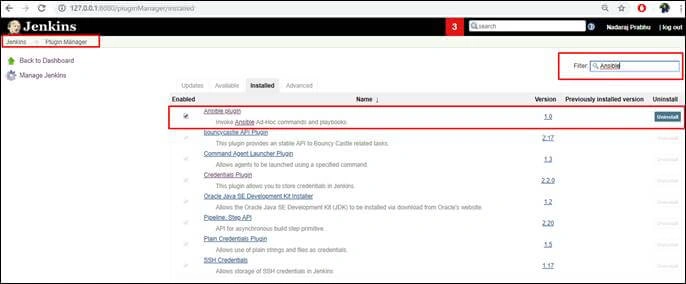
- Click on “Manage Plugins” and look for “Ansible” plugin on the search bar which is on the top right of the page.
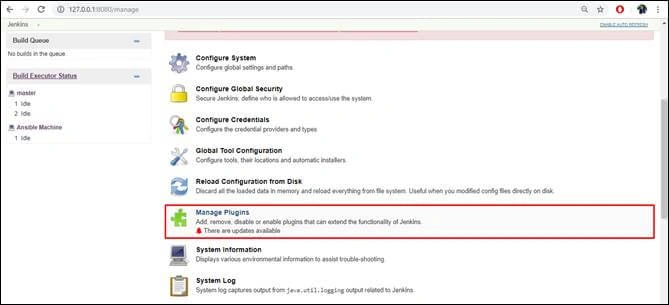
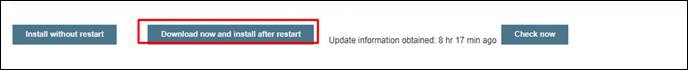
- Select Ansible and click on “Download now and install after restart”.
Note
Don’t install Ansible Tower, which is not required for the current setup.
Don’t install Ansible Tower, which is not required for the current setup.
After a successful install of Ansible plugin in Jenkins, install Ansible in Client/Agent machine.
Install Ansible in Client/Agent machine
Alibaba Ansible Modules are frequently updated hence refer to the GitHub link.
Open a terminal window in the agent machine and execute below commands.
sudo yum check-update; sudo yum install -y gcc libffi-devel python-devel openssl-devel epel-release
sudo yum install -y python-pip python-wheel
For Ubuntu 16.04 LTS
sudo apt-get update && sudo apt-get install -y libssl-dev libffi-dev python-dev python-pip
Enter the following command to install the required packages Ansible for Alibaba
sudo pip install ansible
sudo pip install ansible_alicloud
sudo pip install ansible_alicloud_module_utils
Variable in Ansible Playbook.
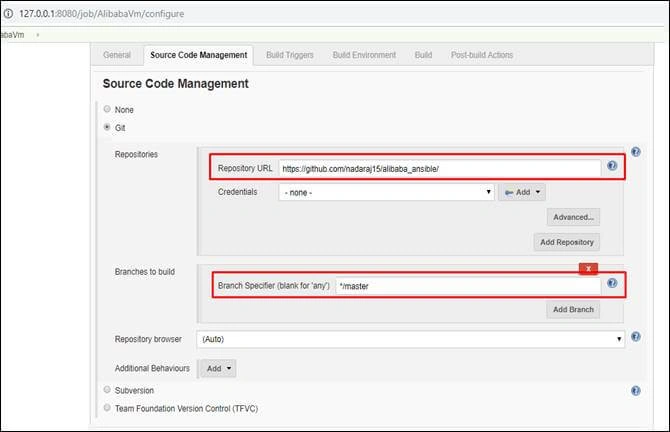
I have created an Ansible playbook script to provision an Alibaba ECS Link. you can fork the source code and modify the parameter values as per your environment.
alicloud_access_key: <Alibaba Access Key>
alicloud_secret_key: <Alibaba Secret Key>
alicloud_region: <Alibaba Region for your resource> e.g. - ap-south-1
alicloud_zone: <Alibaba Zone for your resource> e.g. ap-south-1a
password: <New VM Password>
image: "m-a2d4qmk8v2w9s5wmh0rw"
Note
I’m importing an image from Alibaba Application Stacks provided by Zhuyun. It consists of Linux, Nginx, MySQL and Jdk-Tomcat (Nginx1.6-jdk1.7-tomcat7-mysql5.5-vsFTPd2.2.2)> Link
I’m importing an image from Alibaba Application Stacks provided by Zhuyun. It consists of Linux, Nginx, MySQL and Jdk-Tomcat (Nginx1.6-jdk1.7-tomcat7-mysql5.5-vsFTPd2.2.2)> Link
Generate Access Key and Secret
Step 1
To get access_key and secret_key, go to Alibaba console Link and select “Resource Access Management (RAM)” in “Product” menu.
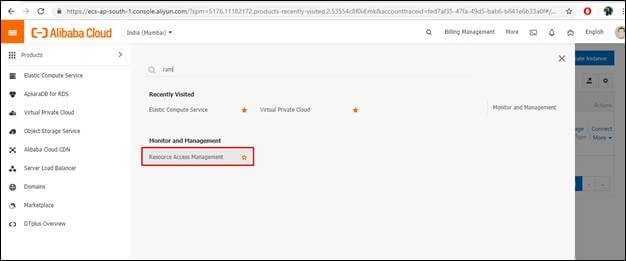
Step 2
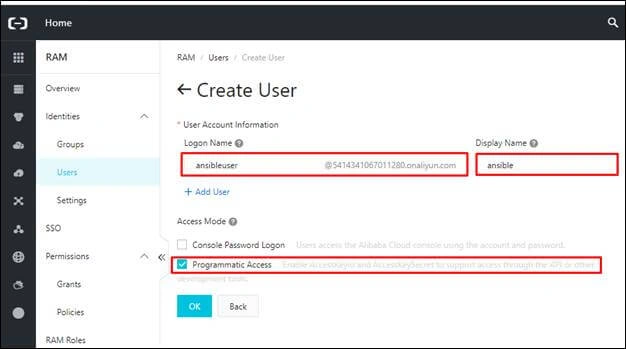
Click on the “Users” option on the left blade and select “Create User”.
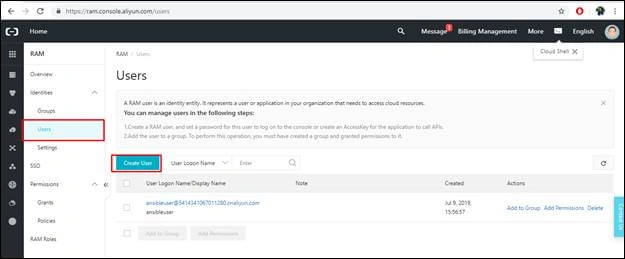
Step 3
Create a new user by providing a login name and display name. Under “Access Mode” check on “Programmatic Access”. It's not required to provide “Console Password Logon” access.
Note
No user will be able to login to Alibaba console using this user, which provides an extra level of security.
No user will be able to login to Alibaba console using this user, which provides an extra level of security.
Step 4
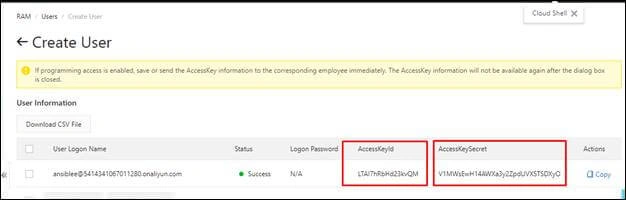
Copy “AccessKeyId” and “AccessKeySecret”, which will be your “alicloud_access_key” and “alicloud_secret_key” value in the playbook.
Note
The AccessKey information will not be available again after the dialog box is closed. Hence copy and save it before you close the dialog box.
The AccessKey information will not be available again after the dialog box is closed. Hence copy and save it before you close the dialog box.
Step 5
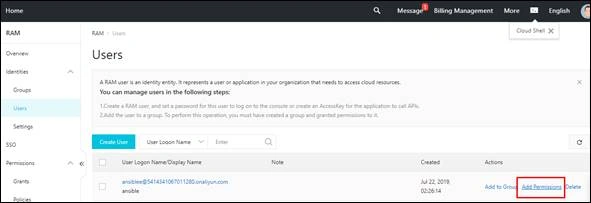
Provide appropriate permission to provide the resources like VPC, V-Switch, Security group, and ECS instance I have provided.
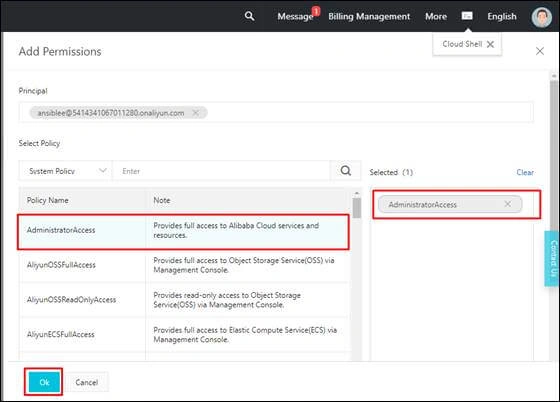
AdministratorAccess
Provides full access to Alibaba Cloud services and resources.
Below are the regions and zone available on Alibaba Cloud.
|
Region
|
"cn-qingdao"
|
"cn-beijing"
|
"cn-zhangjiakou"
|
"cn-huhehaote"
|
"cn-huhehaote"
|
|
Zone
|
"cn-qingdao-b"
"cn-qingdao-c"
|
"cn-beijing-a"
"cn-beijing-b"
"cn-beijing-c"
"cn-beijing-d"
"cn-beijing-e"
"cn-beijing-f"
"cn-beijing-g"
|
"cn-zhangjiakou-a"
"cn-zhangjiakou-b"
|
"cn-huhehaote"
|
"cn-huhehaote-a"
"cn-huhehaote-b"
|
|
Region
|
"cn-hangzhou"
|
"cn-shanghai"
|
"cn-shenzhen"
|
"cn-hongkong"
|
"ap-northeast-1"
|
|
Zone
|
"cn-hangzhou-b"
"cn-hangzhou-c"
"cn-hangzhou-d"
"cn-hangzhou-e"
"cn-hangzhou-f"
"cn-hangzhou-g"
"cn-hangzhou-h"
|
"cn-shanghai-a"
"cn-shanghai-b"
"cn-shanghai-c"
"cn-shanghai-d"
"cn-shanghai-e"
"cn-shanghai-f"
|
"cn-shenzhen-a"
"cn-shenzhen-b"
"cn-shenzhen-c"
"cn-shenzhen-d"
|
"cn-hongkong-a"
"cn-hongkong-b"
"cn-hongkong-c"
|
"ap-northeast-1a"
|
Join the conversation! Your thoughts help the community grow.