
In a previous article, we learned how to set up Azure AD and create users and groups, so we will continue to use that user and group for this article.
So, what is multi-factor authentication?
In today’s world just having a userid and password which contains letters, symbols, numbers etc. is not secure enough, no matter how complex it is. Once your password is lost it's easy for other users to break into your system and steal important information.
So multi-factor authentication refers to more ways to authenticate than just your password.
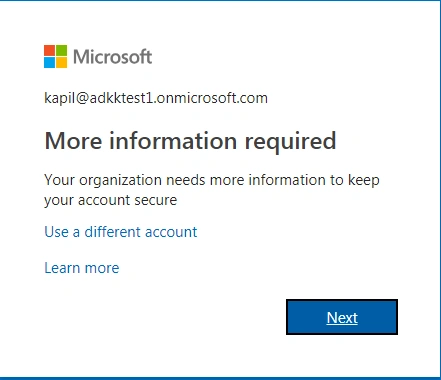
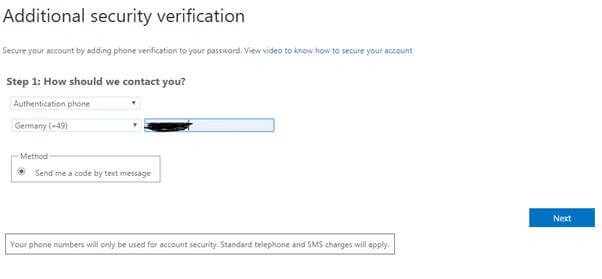
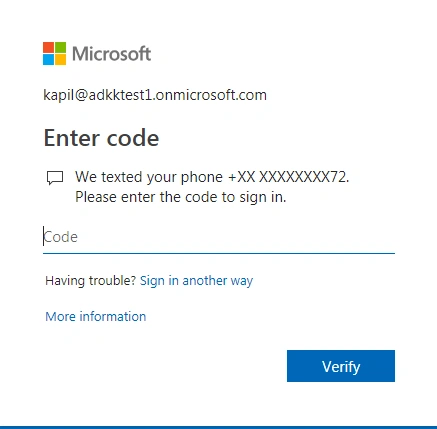
Users can add another layer of authentication either via phone, email, authentication app, security tokens etc. If a user is authenticating via phone then a text message will come to a registered mobile number which is needed during the login process to complete the authorization, or if user chooses the email option then user receives an email with some random numbers which is required other than your password. This way another layer of security can be added.
Microsoft Azure AD supports multi-factor authentication and it's available as add on service and a billing model will be associated with it.
If you are using a premium AD service, then it's included in that.
So, let’s see the demo of how we can enable MFA.
- Login to Azure Active Directory
- Click on Users tab. All user list will appear
- Click on Multi-factor authentication at the top. After you click it will take you to another website in new tab or window.
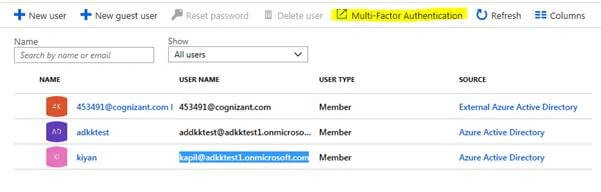
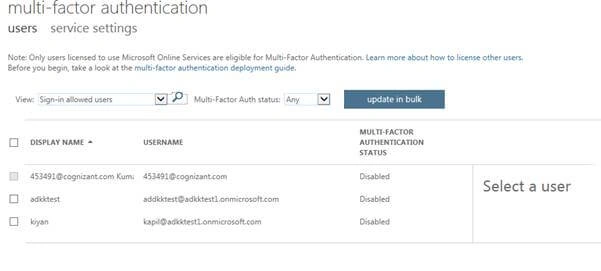
- A new window will open for multi-factor authentication.
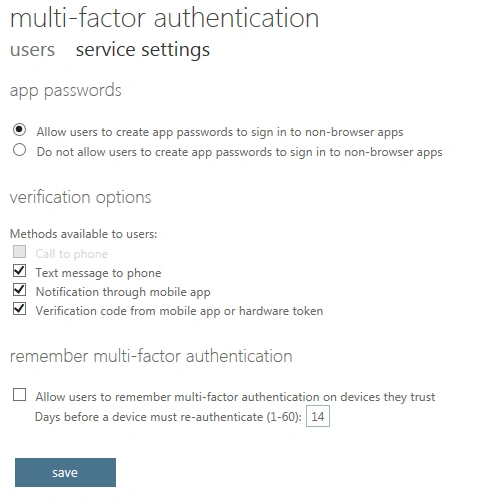
- At top, there are two section ‘Users’ and ‘Service Settings’. By default, User section will open.
- Click on ‘Service Settings’. Here you can see the available option for verification and modify the options as per your choice and need.
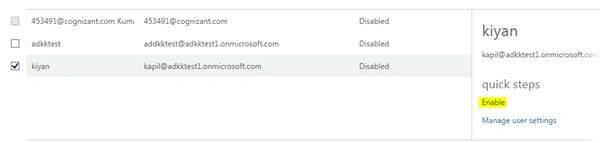
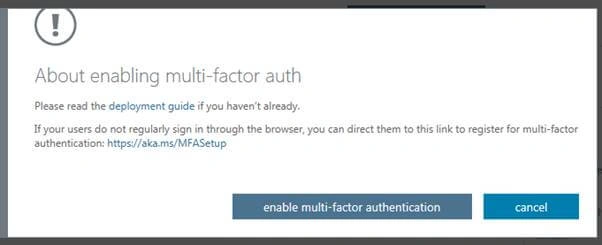
- Now, select the user from User tab for which you need to enable MFA and click ‘Enable’,
Join the conversation! Your thoughts help the community grow.