
In my previous article, we learned how to enable multi-factor authentication for an individual user. We can perform the same steps for all users to enable MFA.
If we don’t have MFA enabled for all users, then also we can enable multi-factor authentication for users based on a condition which is basically a policy that we can define.
Let’s say, we can enable MFA for users who try to login to the system outside of my trusted locations. In that case, whenever a user tries to log in to the system from within a trusted location, the user can login with username and password but when a user tries to login from outside of the trusted location, then they need to go through additional security check, i.e., via MFA.
We can use conditional access to turn ON multi-factor authentication under specific circumstances so rather than depending on the user, it is dependent on the combination of both.
One of the prerequisites to enable conditional access is that the user should have an Azure AD Premium P2 subscription.
Let’s see how we can apply this conditional access.
- Log in to the Azure portal.
- Go to your Azure Active Directory.
- Go to the Security settings and select option ‘Conditional Access’.
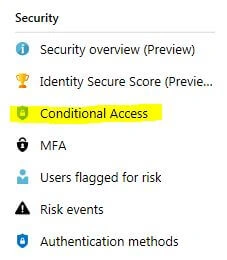
- Click on ‘New Policy’.
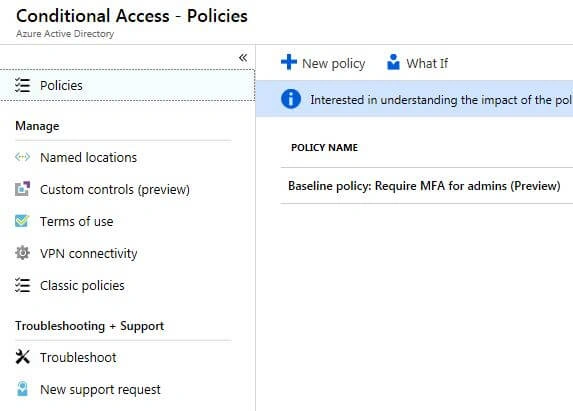
- Enter a name for this policy. For this demo, I entered the name as ‘Trusted Location’.
- Click on ‘Users and Group’ section and select option ‘All users’ as we will enable this policy for all users.
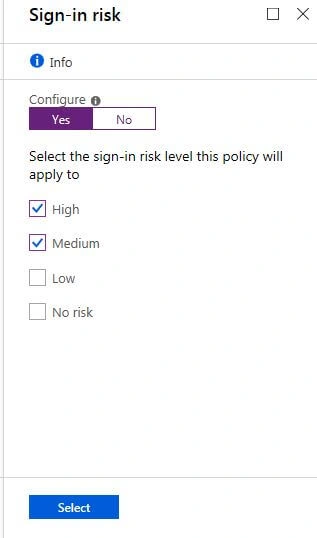
- Click on ‘Conditions’ and Select the ‘Sign-in risk’. This is used to apply the sign-in risk level for the policy.
- Let’s choose the option as ‘High’ and ‘Medium’ in our case as we see it as high risk if any user tries to access the system outside a trusted location.


Join the conversation! Your thoughts help the community grow.