
Introduction
Azure Private Links works with Site-to-Site VPN, Point-to-Site VPN, and the Express Route to provide private and secure access to Azure PaaS services over Azure Private Endpoints. The Azure PAAS Services include a read-only network interface service called Azure Private Endpoint. It allows you to add deployed sites to your virtual network and restrict network access to them.
Key Benefits
- Blocking access to the internet in general.
- Accessible from within the company's on-premises network
- From outside the business network, access is possible through an authorized VPN client.
Step 1
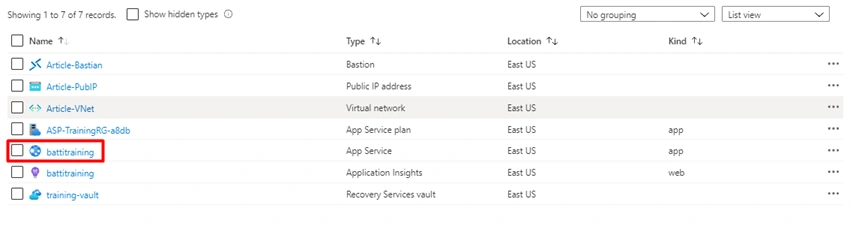
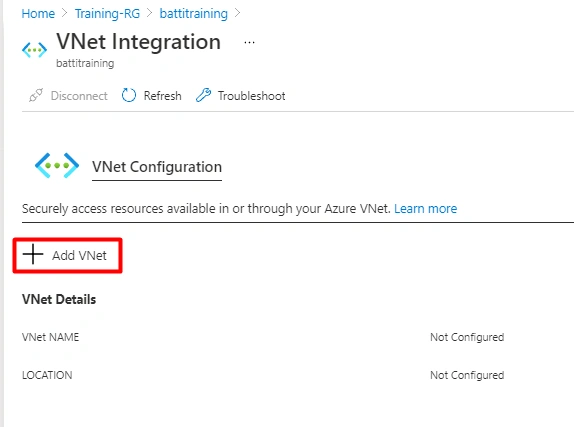
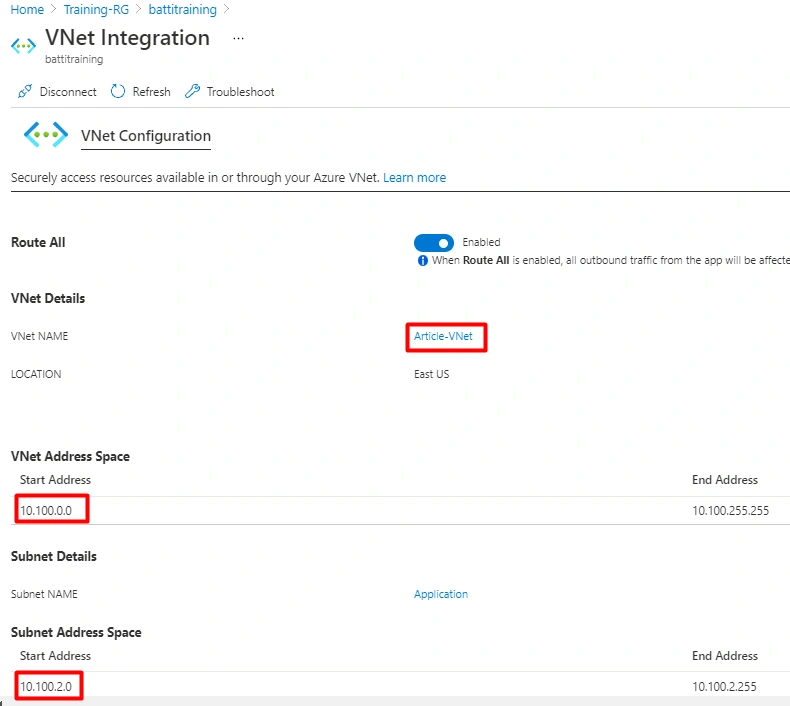
We've already set up Azure Web App service (battitraining) and Virtual Network (Article-VNet) in the Azure portal.
Step 2
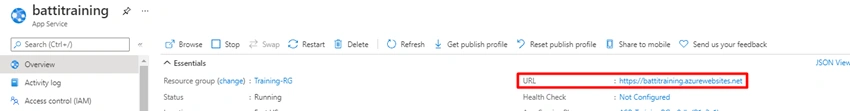
Go to the Web App and copy the URL of the application from the Overview page.
Step 3
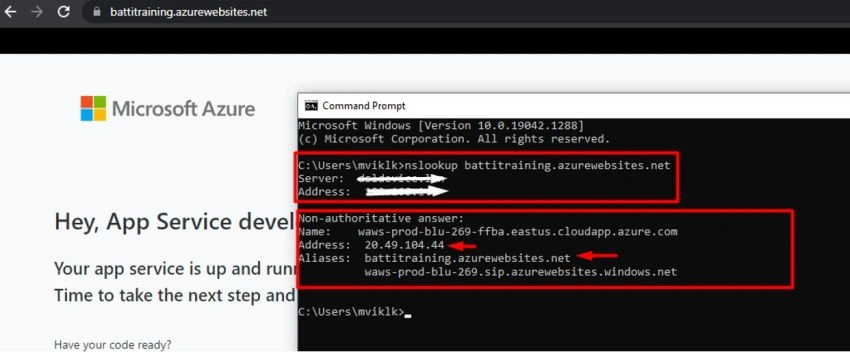
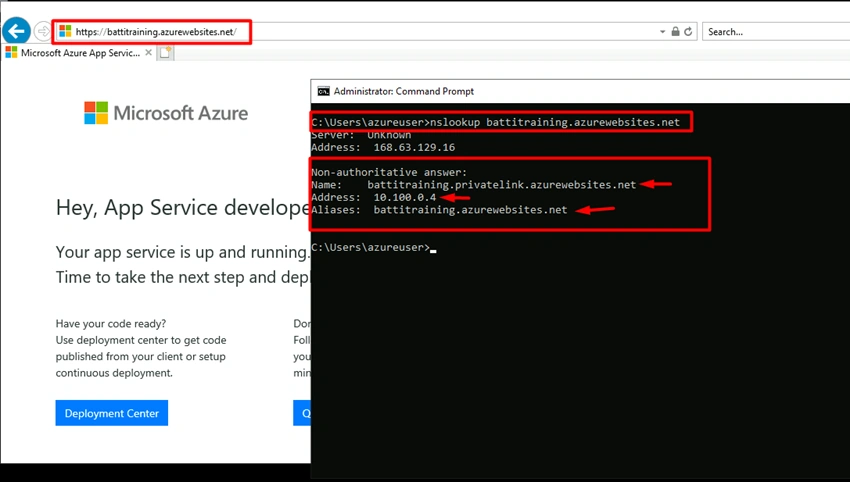
Open a browser, paste the URL, and hit enter, we will receive the landing page, so can observe that the URL is working publicly in the browser. Now we can see what the resolving IP is, so open the Command prompt and execute the "nslookup" command to see the resolved IP and make sure it's the Public IP address.
Step 4
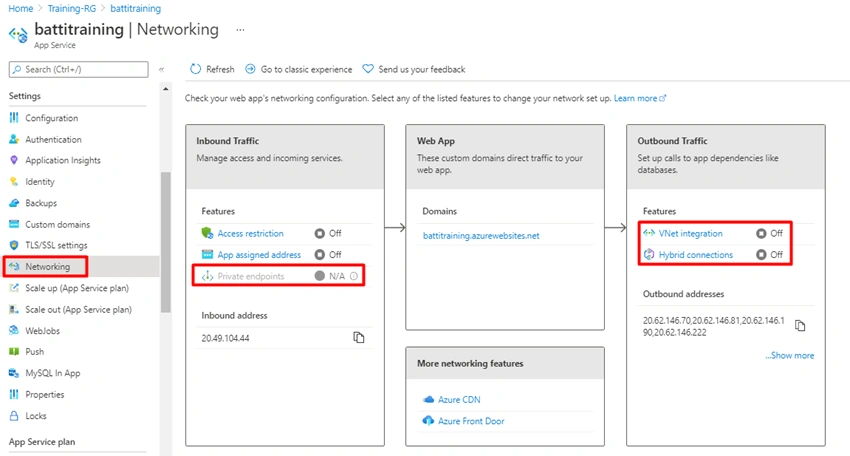
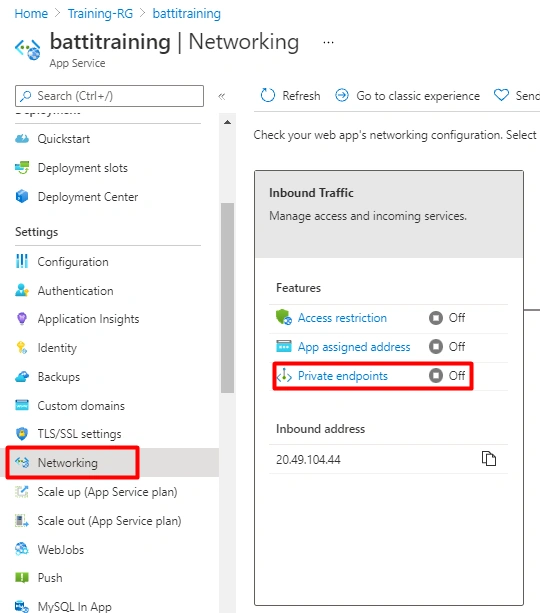
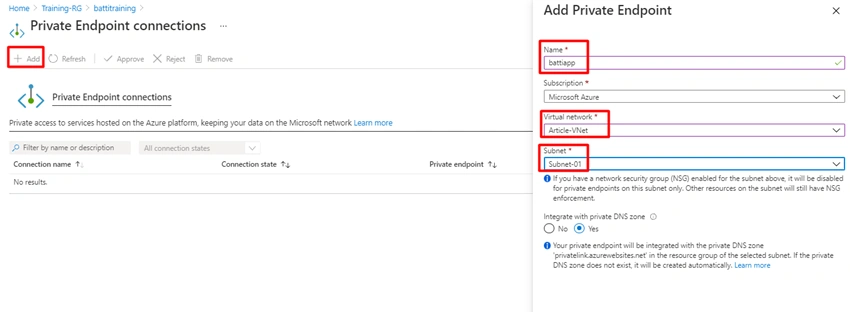
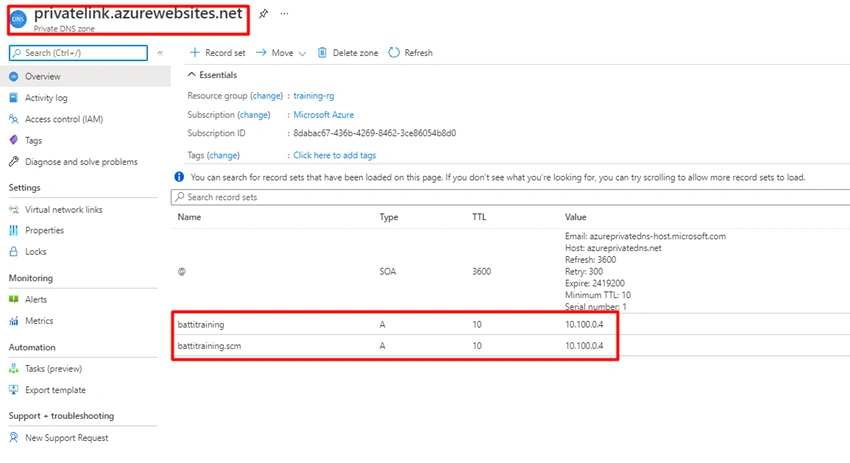
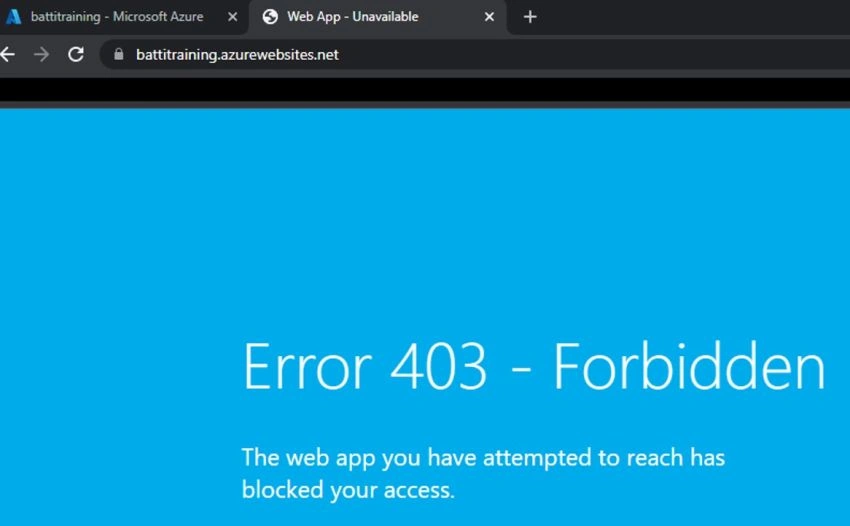
Now go to your Azure portal and access the App service; within the App service, check whether the Private endpoint is available by selecting Networking from the Settings menu. Now that we've discovered that the Private endpoint isn't working, we'll need to upgrade our app service.
Step 5
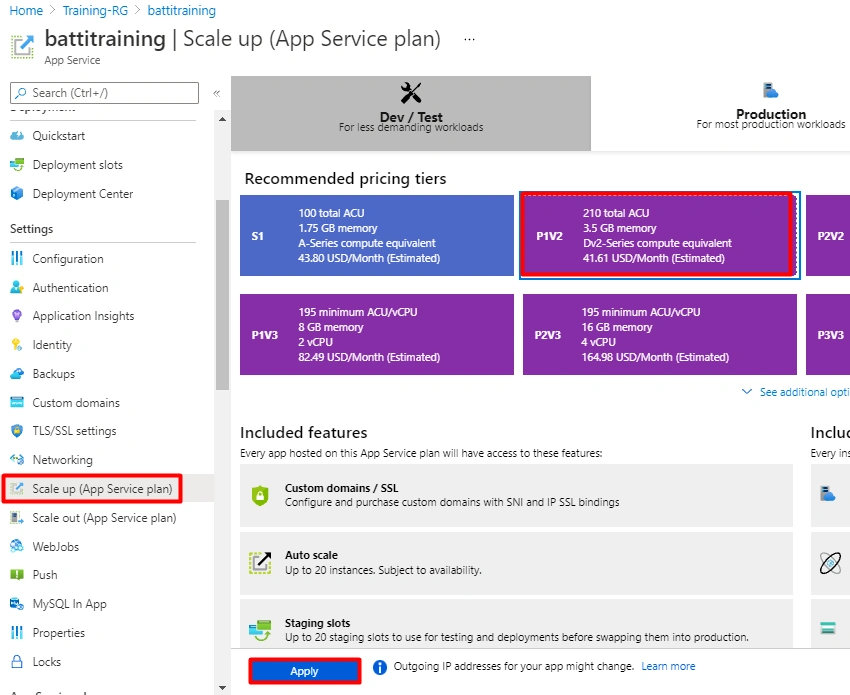
In the App Service select Scale-up (App Service plan) under the Settings, and then Select Premium Plan (in this demo, we will choose P1V2), and then click Apply.
Step 6
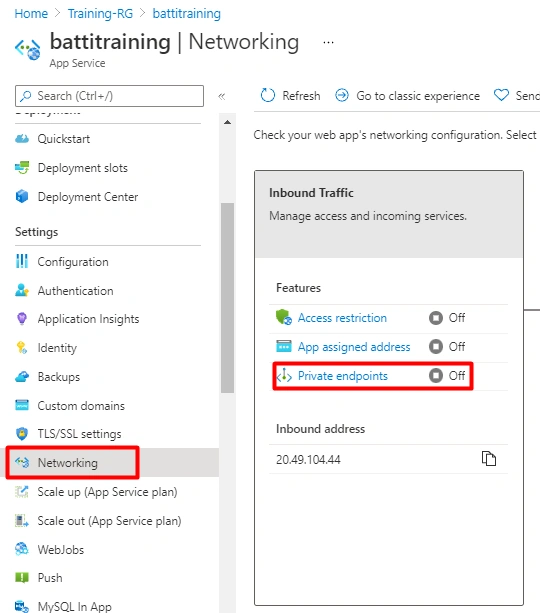
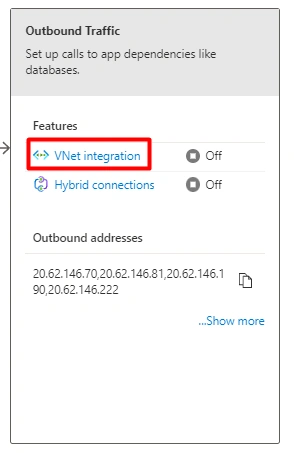
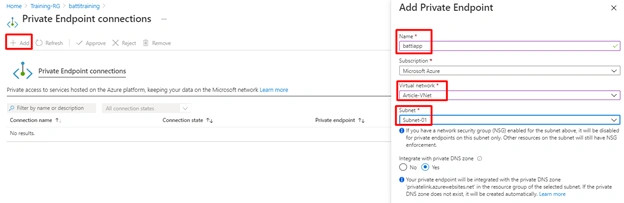
Now we can verify that the Private endpoint service is available for this App service. Now it’s available.
Abdul BasithPosted Jan 12, 2022, 11:15 AM
Superb Article
Hadshana KamalanathanPosted Nov 25, 2021, 6:54 AM
Nice Article!