
Introduction
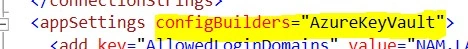
This article gives a walkthrough on how to take an existing ASP.NET application running in Azure App Service, and without touching the C# code, configure it in a way that it will retrieve its sensitive configuration values from a Key Vault instead of its Web.config or App.Config file.
The way how the application reads the configuration, e.g. ConfigurationManager.AppSettings["MyDatabaseConnectionString"] today, that value would come directly from a secret in Key Vault, all without modifying anything in the actual source code of your app.
This is also without storing the Key Vault connection string or credentials in your application configuration file and makes it very easily redeployable across environments.
Framework and Configuration Builder
This guideline is for an ASP.NET project targeting .NET Framework 4.7.1 or later and Configuration Builders which are only available in recent versions of the framework.
Configuration builders in ASP.NET provide a way to modify and/or override the values coming from your configuration files (
Web.config in the case of ASP.NET) by using different sources (environment variables, Key Vault, etc.). This means that you can store your config values in other places than those files without modifying the parts of your application that are dependent on those values.Implementation Steps
- Add secrets to the Key Vault: Add the secrets to the Key Vault and It’s important that the secrets must have the same name as the app settings you would like to replace with them. So, for example, if you have an app setting with the key MyDatabaseConnectionString in your
Web.configfile, you must create a secret with the same name and the relevant value in Key Vault.
Steps to create Key Vault
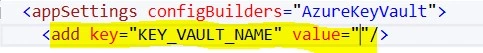
- Give access to your Web App to the secrets stored in Key Vault. The recommended approach is to use Web App’s managed identity feature. This feature will provide a Web App with its own identity in Azure Active Directory and the application will be able to authenticate with Key Vault using that identity. The benefit of this is that the only information that is needed to pass to the application is the name of the Key Vault instance to connect to.
a. Enable System Managed Identity on the Web App:
b. Grant access to the web app on the Key Vault with relevant permissions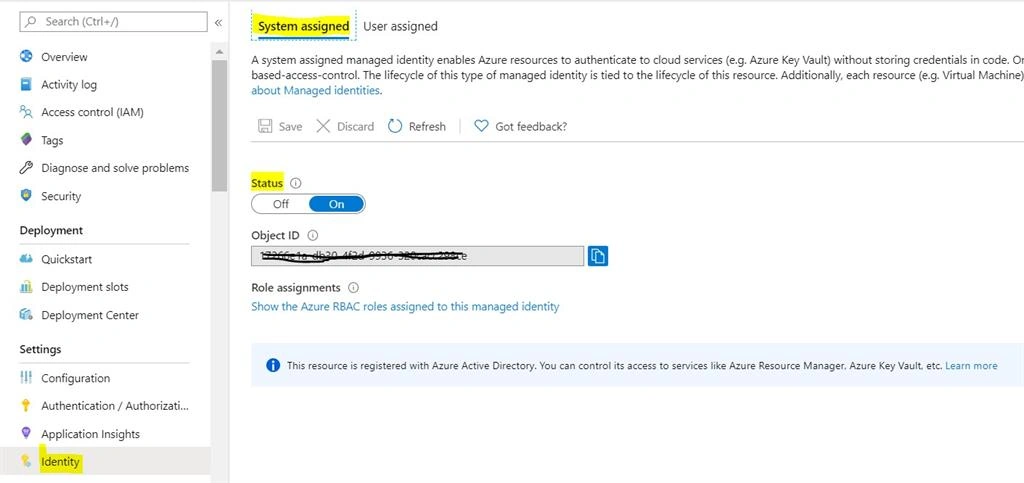


kalyan pssPosted Sep 27, 2021, 3:25 PM
Hi Nithin, were you able to successfully build the application in Azure Devops after this implementation? Because i am getting the following exception "Type is not resolved for member 'Azure.Identity.Credential Unavailable Exception,Azure.Identity"