
In the previous article, we successfully generated a JWT and returned it to the client after login. At this point, the client has an access token that represents the authenticated user.
But there's one important question:
How does the API know whether the received token is genuine or fake?
Simply receiving a JWT does not mean the API should trust it. Anyone can copy a token, modify it, or even create a fake one. Before executing a protected endpoint, ASP.NET Core must validate the token and ensure it was issued by a trusted source.
In this article, you'll learn how JWT validation works internally and how to configure JWT Bearer Authentication in an ASP.NET Core Web API.
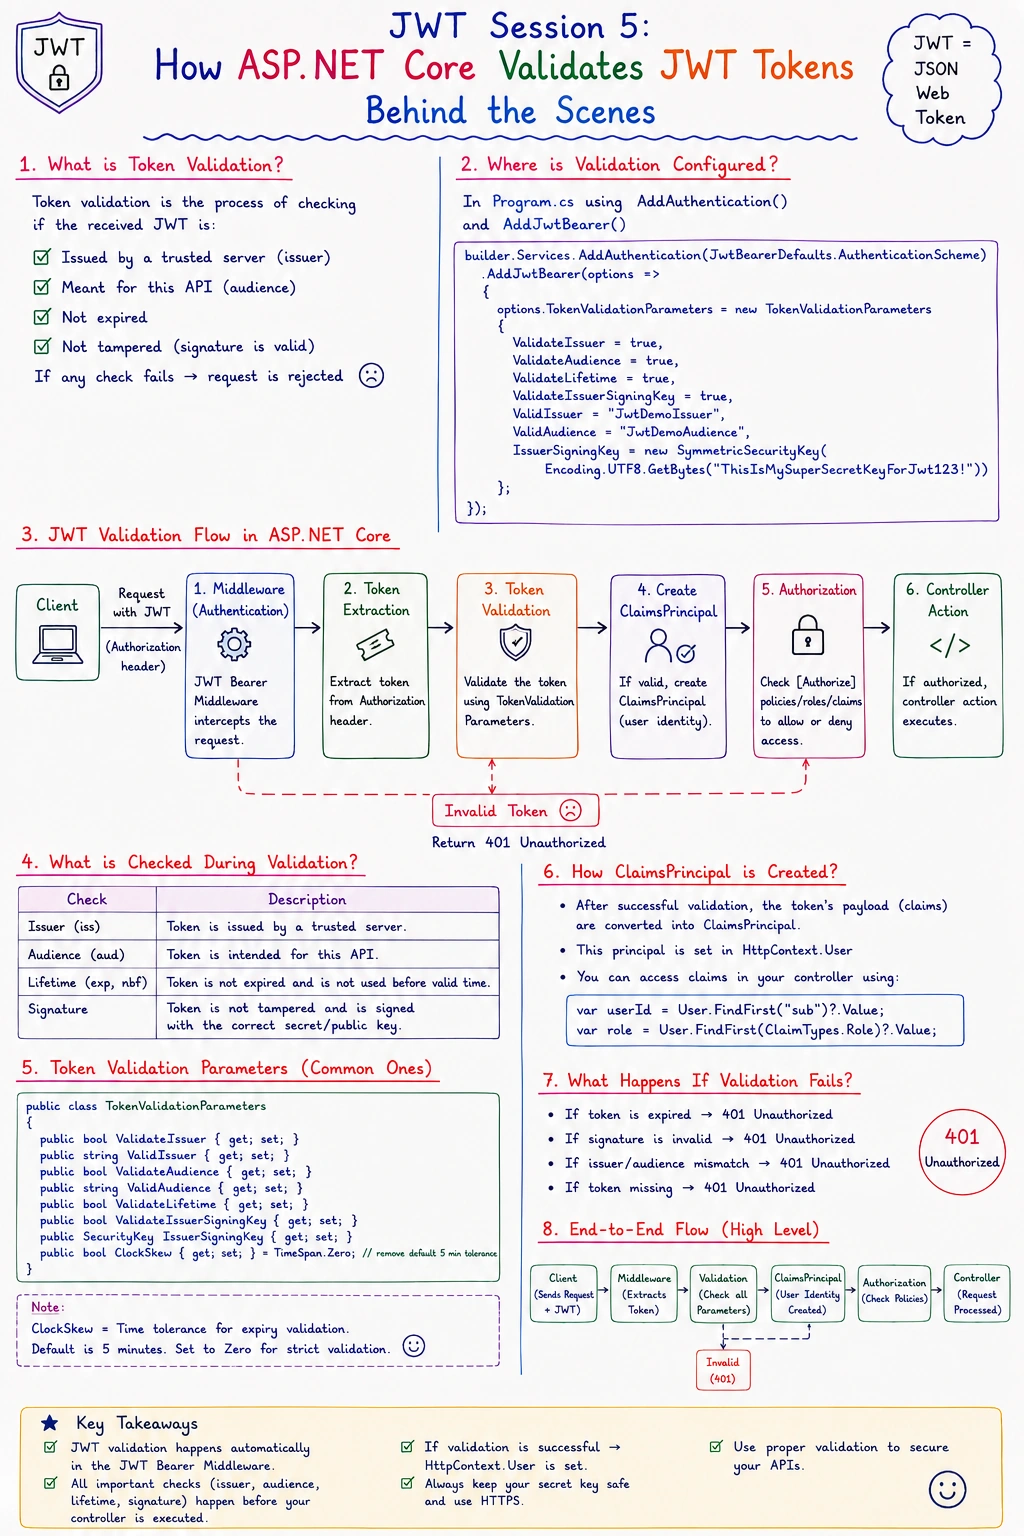
What Is JWT Validation?
JWT validation is the process of verifying whether an incoming token is authentic, valid, and trustworthy before allowing access to a protected API.
Think of a movie ticket.
When you enter a cinema, the security staff doesn't just check whether you're holding a ticket. They verify:
Is the ticket genuine?
Has it expired?
Is it for this theatre?
Has it been tampered with?
Only after these checks are completed are you allowed to enter.
JWT validation follows exactly the same idea.
Why Is Token Validation Necessary?
Suppose someone sends the following request:
GET /api/orders
Authorization: Bearer eyJhbGciOiJIUzI1NiIs...
The API cannot simply trust this token because:
The token may have expired.
Someone may have modified its contents.
It may have been issued by another application.
It may have been created using an invalid signing key.
Without validation, anyone could gain unauthorized access to your APIs.
How JWT Validation Works
Whenever a protected endpoint receives a request, ASP.NET Core automatically performs several validation steps.
HTTP Request
      │
      ▼
Read Authorization Header
      │
      ▼
Extract JWT
      │
      ▼
Validate Token
      │
      ├── Signature
      ├── Expiration
      ├── Issuer
      ├── Audience
      │
      ▼
Create User Identity
      │
      ▼
Execute Controller
If any validation fails, the request stops immediately.
The controller action is never executed.
Step 1: Install JWT Bearer Authentication
If you haven't already installed the package, run:
dotnet add package Microsoft.AspNetCore.Authentication.JwtBearerThis package provides the middleware responsible for reading and validating JWT tokens.
Step 2: Register JWT Authentication
Open Program.cs.
Add the required namespaces.
using Microsoft.AspNetCore.Authentication.JwtBearer;
using Microsoft.IdentityModel.Tokens;
using System.Text;
Now register JWT authentication.
builder.Services
    .AddAuthentication(JwtBearerDefaults.AuthenticationScheme)
    .AddJwtBearer(options =>
    {
        options.TokenValidationParameters =
            new TokenValidationParameters
            {
                ValidateIssuer = true,
                ValidateAudience = true,
                ValidateLifetime = true,
                ValidateIssuerSigningKey = true,

                ValidIssuer = builder.Configuration["Jwt:Issuer"],
                ValidAudience = builder.Configuration["Jwt:Audience"],

                IssuerSigningKey =
                    new SymmetricSecurityKey(
                        Encoding.UTF8.GetBytes(
                            builder.Configuration["Jwt:Key"]!))
            };
    });
This tells ASP.NET Core how every incoming JWT should be validated.
Understanding TokenValidationParameters
This class contains all the validation rules.
Let's understand each property.
ValidateIssuer
ValidateIssuer = trueThis verifies that the token was generated by the expected application.
If another application creates a token, ASP.NET Core rejects it.
Join the conversation! Your thoughts help the community grow.