
Introduction
In this article, I am going to talk about orchestrating containers developed in (.NET Core technology) using Azure Kubernetes service. The service can be consumed by any front-end application like HTML, etc., I will be demonstrating in a step-by-step manner how to create Kubernetes cluster and deploy the ASP.NET Core application image into Azure registry and then how Kubernetes cluster maintains those internal container instances automatically.
Please refer to my article how to deploy local docker image into azure regsitry, this will be useful to deploy your local docker image into Azure container registry. We will focus only on Kubernetes services in this article.
Pre-requisite
Orchestrating containers using Kubernetes
Step 1
Go to Azure Portal and open cloud shell on right top corner(>_) to create secrets and to deploy images from container registry to Kubernetes.
Step 2
Create Image pull secret to secure image using the same credential of container registry.
- kubectl create secret docker-registry trainings --docker-server= trainingservice1.azurecr.io --docker-username= trainingservice1 --docker-password= lddH+ejcVXQf81nNWP3C9bTOA
'trainings' is the name of secrets and docker-server is the login server name from container registry and docker-username and password is container registry username and password.
Step 3
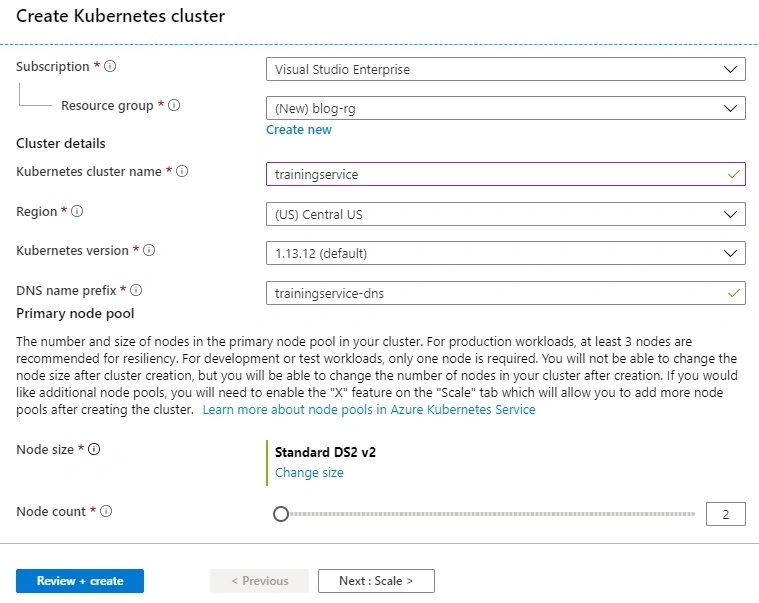
Create new Resource -> Containers -> Kubernetes Service (AKS cluster), with Node count two, this node will be used to load balance in case of more requests which are taken care of by Kubernetes services. You can keep all other parameter values as default.
DeepikaPosted Dec 16, 2019, 11:04 AM
Nice article