
ABSTRACT
Blockchain technology has transformed the way digital transactions are performed by providing decentralization, transparency, immutability, and trust without relying on centralized authorities. Modern blockchain platforms primarily depend on classical cryptographic algorithms such as RSA, Elliptic Curve Cryptography (ECC), and ECDSA for key generation, digital signatures, authentication, and transaction verification. While these cryptographic techniques are considered secure against classical computing attacks, the rapid advancement of quantum computing presents a significant challenge to their long-term reliability.
Quantum algorithms, particularly Shor's Algorithm and Grover's Algorithm, have demonstrated the theoretical capability to compromise widely used public-key cryptographic systems. Once large-scale fault-tolerant quantum computers become available, attackers could potentially recover private keys from public keys, forge digital signatures, and manipulate blockchain transactions. Such capabilities would undermine the fundamental security principles upon which blockchain networks are built.
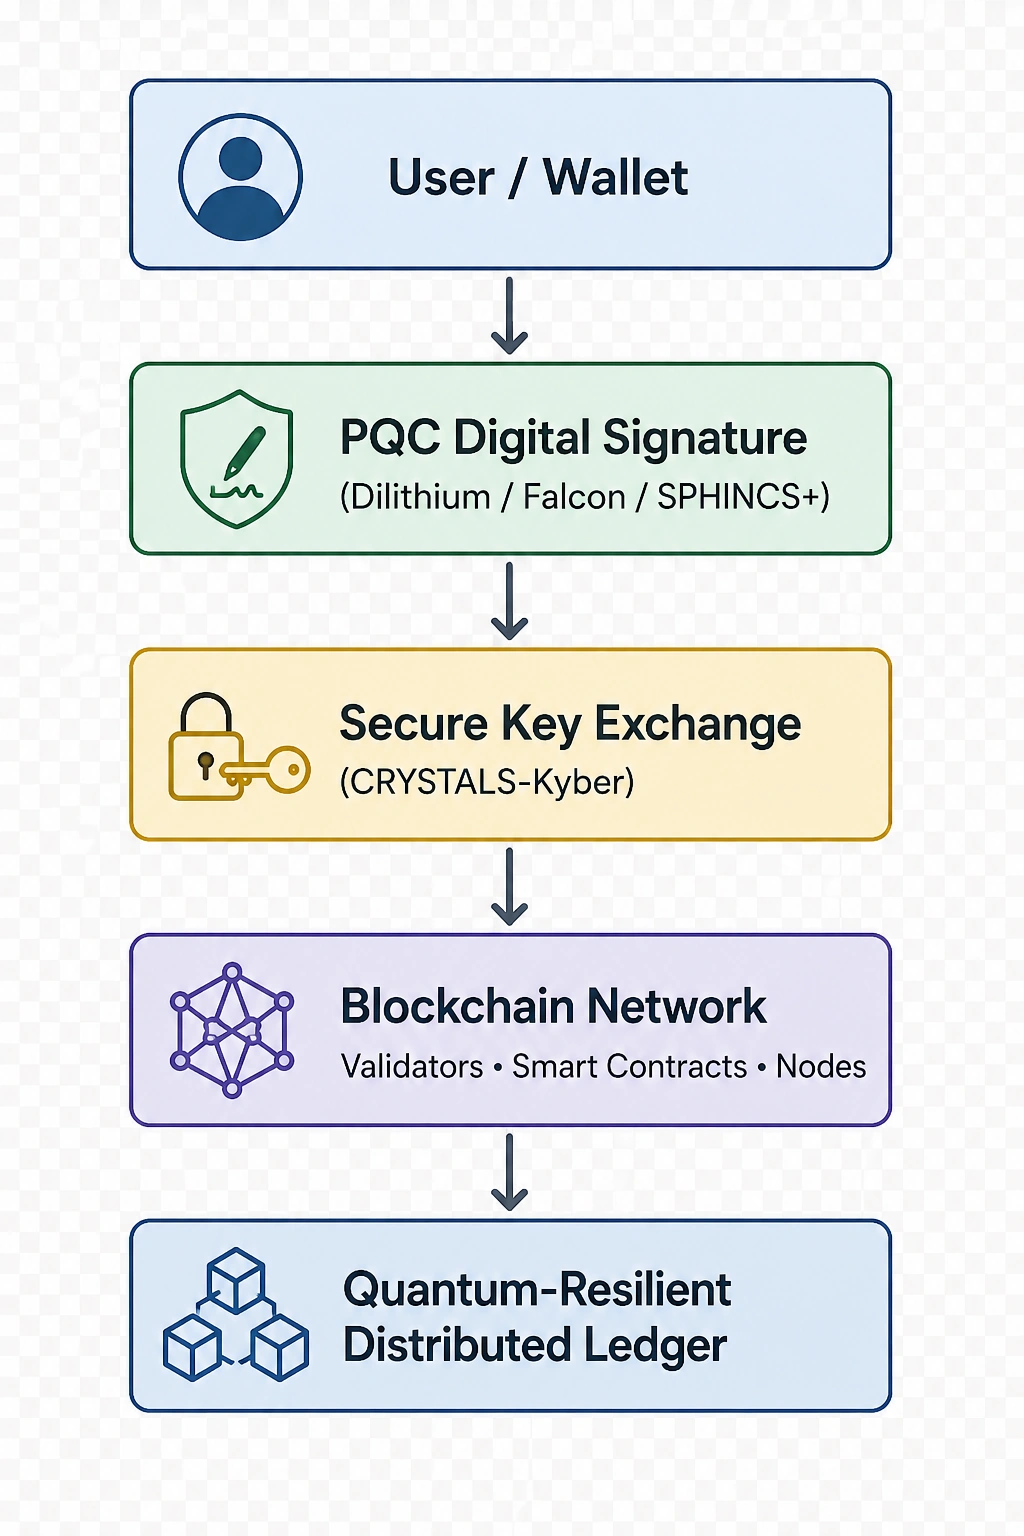
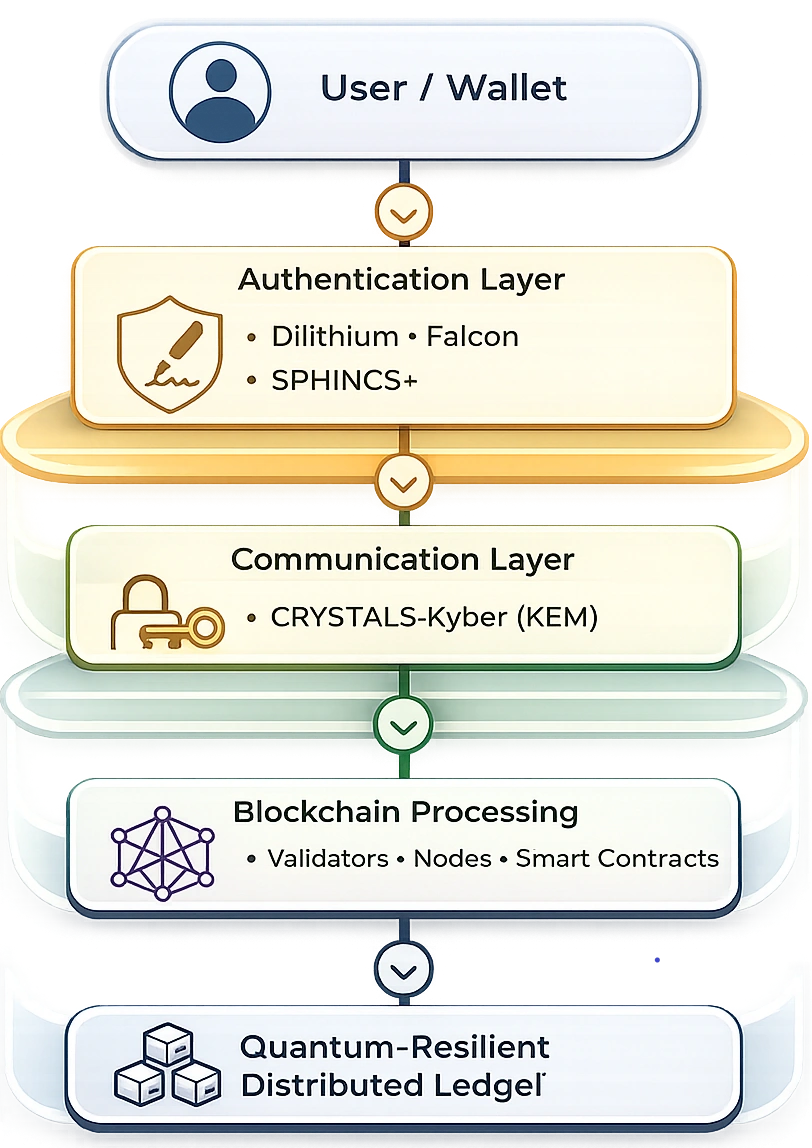
To address these emerging threats, the cybersecurity community has shifted its attention toward Post-Quantum Cryptography (PQC), a new generation of cryptographic algorithms specifically designed to remain secure against both classical and quantum attacks. In recent years, the National Institute of Standards and Technology (NIST) has standardized several quantum-resistant algorithms, including CRYSTALS-Kyber for secure key encapsulation and CRYSTALS-Dilithium, Falcon, and SPHINCS+ for digital signatures. These algorithms are expected to become the foundation of secure digital communication in the quantum era.
This article explores the growing importance of Post-Quantum Cryptography in blockchain technology. It discusses the limitations of existing cryptographic mechanisms, explains the working principles of NIST-standardized PQC algorithms, compares their characteristics, and examines how they can be integrated into blockchain ecosystems. Finally, the article highlights future research directions and the challenges associated with migrating existing blockchain infrastructures toward quantum-resilient decentralized systems.
1. Introduction
Over the past decade, blockchain technology has evolved from powering cryptocurrencies to becoming a fundamental component of modern digital infrastructure. Today, blockchain is widely adopted in sectors such as finance, healthcare, supply chain management, digital identity, cloud computing, electronic voting, and smart cities. Its decentralized architecture ensures transparency, integrity, and trust while eliminating the need for centralized intermediaries.
The security of every blockchain network depends heavily on cryptographic algorithms. Digital signatures authenticate users, cryptographic hash functions maintain data integrity, and asymmetric encryption protects sensitive communications between participants. Algorithms such as RSA and Elliptic Curve Digital Signature Algorithm (ECDSA) have served as the backbone of blockchain security since the inception of Bitcoin and Ethereum.
For decades, these cryptographic systems have successfully protected billions of digital transactions. However, their security assumptions rely on the computational limitations of classical computers. As long as factoring large integers or solving discrete logarithm problems remains computationally infeasible, these algorithms continue to provide strong protection.
The emergence of quantum computing challenges this assumption. Unlike classical computers that process information using binary bits, quantum computers operate using qubits, which exploit quantum mechanical properties such as superposition and entanglement. These properties allow quantum systems to solve specific computational problems exponentially faster than conventional computers.
One of the most significant breakthroughs in quantum computing was the introduction of Shor's Algorithm, which demonstrated that sufficiently powerful quantum computers could efficiently solve integer factorization and discrete logarithm problems. Since RSA and ECC rely directly on these mathematical problems, they would become vulnerable in the presence of large-scale quantum computers.
For blockchain networks, this creates serious security implications. An adversary equipped with a quantum computer could theoretically derive private keys from publicly available blockchain addresses, forge digital signatures, impersonate legitimate users, and authorize fraudulent transactions. Such attacks could compromise digital assets, smart contracts, decentralized applications, and the overall trustworthiness of blockchain ecosystems.
Another quantum algorithm, Grover's Algorithm, reduces the complexity of brute-force attacks against symmetric cryptographic primitives and hash functions. Although hash algorithms such as SHA-256 remain comparatively more resistant than public-key systems, Grover's Algorithm effectively halves their security strength, encouraging the adoption of stronger hash functions and longer key lengths.
These developments have accelerated global efforts to identify cryptographic techniques capable of resisting quantum attacks. Instead of relying on integer factorization or elliptic curve mathematics, researchers have developed entirely new families of cryptographic algorithms based on mathematical problems believed to remain difficult even for quantum computers.
This new generation of security mechanisms is collectively known as Post-Quantum Cryptography (PQC).
Recognizing the urgency of this transition, the National Institute of Standards and Technology (NIST) initiated a multi-year global standardization program to evaluate quantum-resistant cryptographic algorithms. After extensive analysis involving researchers worldwide, NIST selected several algorithms for future cryptographic standards. Among these, CRYSTALS-Kyber was standardized for secure key establishment, while CRYSTALS-Dilithium, Falcon, and SPHINCS+ were selected for digital signature applications.
These algorithms represent a major milestone in the evolution of cybersecurity. Unlike Quantum Key Distribution (QKD), which requires specialized quantum communication infrastructure, Post-Quantum Cryptography can be deployed using existing hardware and communication networks, making it significantly more practical for real-world blockchain adoption.
As governments, financial institutions, cloud service providers, and blockchain platforms prepare for the quantum era, integrating Post-Quantum Cryptography into decentralized systems is no longer a theoretical consideration, it has become a strategic necessity.
This article examines how Post-Quantum Cryptography strengthens blockchain security, explores the characteristics of the leading NIST-standardized algorithms, compares their capabilities, and discusses how they can be incorporated into next-generation blockchain architectures capable of withstanding future quantum-enabled cyber threats.
2. Why Current Blockchain Cryptography Is at Risk?
Blockchain is often regarded as one of the most secure technologies ever developed. Its decentralized architecture, immutable ledger, and cryptographic foundation collectively ensure the confidentiality, integrity, and authenticity of digital transactions. However, the security of blockchain is not solely dependent on decentralization; it fundamentally relies on the strength of the cryptographic algorithms protecting every transaction and user identity.
For nearly two decades, blockchain platforms have successfully employed algorithms such as RSA, Elliptic Curve Digital Signature Algorithm (ECDSA), and SHA-256. These cryptographic primitives have proven resilient against attacks from classical computers. Unfortunately, the emergence of practical quantum computing challenges the mathematical assumptions upon which these algorithms are built.
A sufficiently powerful quantum computer could compromise existing public-key cryptography, making today's blockchain infrastructure vulnerable to attacks that are currently considered computationally impossible. Understanding these vulnerabilities is the first step toward appreciating the importance of Post-Quantum Cryptography.
2.1 Elliptic Curve Digital Signature Algorithm (ECDSA)
ECDSA is one of the most widely adopted digital signature algorithms in blockchain technology. Bitcoin, Ethereum (prior to quantum-resistant upgrades), and many other blockchain platforms rely on ECDSA to authenticate users and verify transactions.
Whenever a user initiates a blockchain transaction, the transaction is digitally signed using the sender's private key. Other participants in the network verify this signature using the corresponding public key before accepting the transaction into the blockchain.
The security of ECDSA depends on the computational difficulty of solving the Elliptic Curve Discrete Logarithm Problem (ECDLP). Classical computers require an impractical amount of time to solve this problem for sufficiently large key sizes, making ECDSA highly secure under current computational capabilities.
However, Shor's Algorithm changes this assumption dramatically. A large-scale quantum computer could solve the elliptic curve discrete logarithm problem in polynomial time, allowing an attacker to derive the private key from a publicly available public key. Once the private key is compromised, fraudulent transactions could be generated and digitally signed as though they originated from the legitimate owner.
This represents one of the most serious security concerns for blockchain ecosystems.
2.2 RSA Cryptography
Although RSA is not commonly used for blockchain transaction signatures, it remains one of the most widely deployed public-key cryptographic algorithms across the Internet. Many blockchain-based applications still depend on RSA for secure communication, certificate management, identity verification, and backend authentication.
RSA derives its security from the computational complexity of factoring extremely large composite integers.
For example,
Public Key → Shared openly
Private Key → Secret
Security → Based on integer factorization
Under classical computing, factoring a 2048-bit RSA modulus would require an infeasible amount of computational resources.
Quantum computing fundamentally changes this landscape.
Shor's Algorithm can efficiently factor large integers, enabling attackers to recover RSA private keys within a realistic timeframe once scalable quantum computers become available. As a result, encrypted communications, authentication systems, and digital certificates protected by RSA would no longer provide adequate security.
2.3 SHA-256 Hash Function
Unlike RSA and ECDSA, SHA-256 is a cryptographic hash function rather than an encryption algorithm.
Blockchain networks extensively utilize SHA-256 for:
Block hashing
Proof-of-Work mining
Transaction integrity
Merkle Tree generation
Blockchain immutability
SHA-256 converts an input of any size into a fixed-length 256-bit hash value. Unlike public-key cryptography, SHA-256 is not directly broken by Shor's Algorithm. However, it is affected by Grover's Algorithm, which provides a quadratic speedup for brute-force search problems.
In practical terms, Grover's Algorithm effectively reduces the security strength of SHA-256 from approximately 256-bit security to 128-bit security. Although SHA-256 remains considerably more resistant than RSA or ECDSA, future blockchain systems may require larger hash sizes, stronger hash functions, or hybrid security mechanisms to maintain long-term protection. Therefore, hash-based security remains relatively robust but is not entirely immune to the impact of quantum computing.
2.4 Shor's Algorithm: The Greatest Threat to Public-Key Cryptography
In 1994, mathematician Peter Shor introduced an algorithm that fundamentally changed the future of cybersecurity.
Shor's Algorithm demonstrated that a quantum computer could efficiently solve mathematical problems that are considered computationally infeasible for classical computers.
Specifically, it can:
Factor large integers
Solve discrete logarithm problems
Break RSA encryption
Compromise Elliptic Curve Cryptography (ECC)
Recover blockchain private keys
The implications for blockchain are profound. If an attacker obtains the public key associated with a blockchain wallet, a sufficiently powerful quantum computer could potentially derive the corresponding private key. This would enable unauthorized transaction signing, digital asset theft, identity impersonation, and compromise of smart contracts.
Although today's quantum computers are not yet powerful enough to perform such attacks at scale, cybersecurity experts increasingly warn about the "Harvest Now, Decrypt Later" strategy, in which attackers collect encrypted or publicly available cryptographic data today with the intention of breaking it once quantum hardware matures.
2.5 Grover's Algorithm: Weakening Symmetric Cryptography
Unlike Shor's Algorithm, which targets public-key cryptography, Grover's Algorithm primarily affects symmetric cryptographic systems and cryptographic hash functions.
Grover's search algorithm reduces brute-force search complexity from:
O(2ⁿ)
to approximately
O(√2ⁿ)
Although this does not completely break algorithms such as SHA-256 or AES, it significantly reduces their effective security level.
For example:
| Classical Security | Effective Quantum Security |
|---|---|
| AES-128 | Approximately 64-bit |
| AES-256 | Approximately 128-bit |
| SHA-256 | Approximately 128-bit |
Fortunately, symmetric cryptography can often be strengthened simply by increasing key sizes. Public-key cryptography, however, cannot be secured merely by using larger keys, making the transition to Post-Quantum Cryptography essential.
Architecture of the Quantum Threat to Blockchain
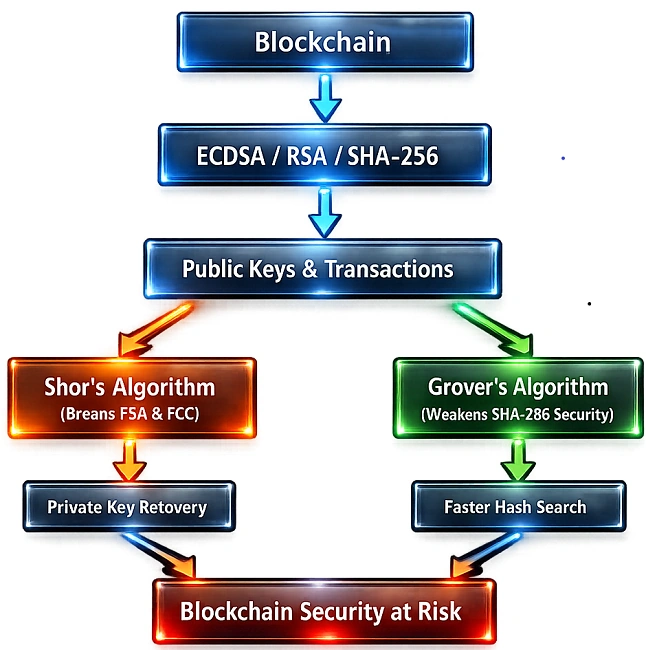
The security of today's blockchain platforms relies heavily on cryptographic algorithms that were designed for the classical computing era. While ECDSA, RSA, and SHA-256 have served as reliable security mechanisms for decades, quantum computing introduces new computational capabilities that challenge their long-term effectiveness. Shor's Algorithm threatens public-key cryptography by enabling efficient private key recovery, whereas Grover's Algorithm weakens the security margin of cryptographic hash functions. These developments make it clear that blockchain systems must evolve beyond traditional cryptographic techniques. The adoption of Post-Quantum Cryptography is therefore not merely an enhancement but a necessary step toward ensuring the continued security, trust, and resilience of decentralized systems in the quantum era.3. What is Post-Quantum Cryptography (PQC)?
The rapid advancement of quantum computing has compelled the cybersecurity community to rethink the foundations of modern cryptography. While today's encryption techniques have successfully protected digital systems for decades, their security relies on mathematical problems that are extremely difficult for classical computers to solve. Quantum computers, however, possess computational capabilities that can solve many of these problems exponentially faster, rendering several widely used cryptographic algorithms ineffective.
To address this emerging challenge, researchers have developed a new class of cryptographic algorithms known as Post-Quantum Cryptography (PQC).
Post-Quantum Cryptography refers to a collection of cryptographic algorithms specifically designed to remain secure against attacks from both classical and quantum computers. Unlike Quantum Cryptography, which depends on quantum communication channels and specialized hardware, PQC algorithms are entirely software-based and can be implemented on existing computers, servers, mobile devices, cloud platforms, and blockchain networks without requiring quantum infrastructure.
Join the conversation! Your thoughts help the community grow.