
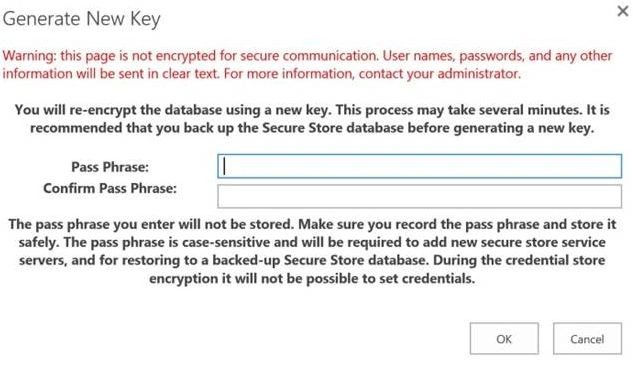
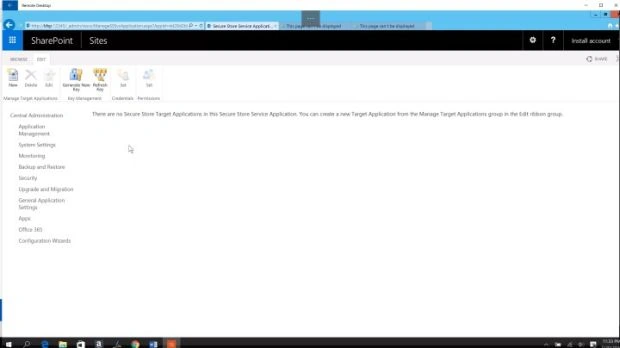
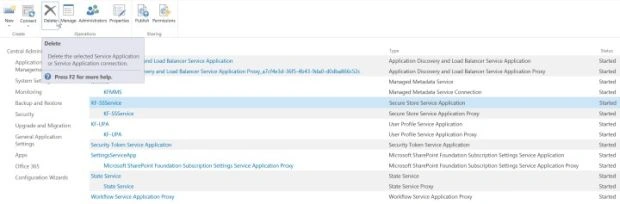
In this article, we will walk through the creation of Secure Store Service, generation of the Key, and deletion of Secure Store Service. We will perform all these operations via Central Admin.
Introduction
The Secure Store Service is an authorization service that runs on an Application Server. The Secure Store Service provides a database that is used to store credentials. These credentials usually consist of a user identity and password, but can also contain other fields that you define. For example, SharePoint Server 2013 can use the Secure Store database to store and retrieve credentials for accessing external data sources. The Secure Store Service provides support for storing multiple sets of credentials for multiple back-end systems.
Before Starting
You should make sure that the following things are ready, before you start. It will help you to create the service application flawlessly.
- Farm Administrator Account to log into Central Admin and for creation of SSS
- URL of the Central Admin
- Service Account (Managed Account) which will run the app pool of Secure Store Service
- Name of the Server where this service application will run
- SQL Server Alias where SSS database will be provisioned
- Name of the Database of SSS
- Name of the application pool of SSS
- Generation Key.
Tips
For a successful configuration of SSS, the following are the industry recommendations.
- Use the dedicated app pool for SSS, and it should not be shared with other application.
- Use the dedicated SQL Server or an SQL Server which should not hold the Content Databases.
- Backup the generation key and SSS database.
- Run the Service on the Application Server.
Create Secure Store Service
In order to create the Secure Store Service, please follow these steps.
- Log onto the Central Admin site with Farm administrator account, with local admin.
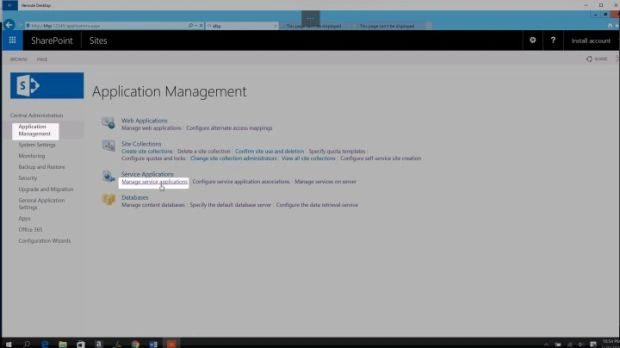
- Click on "Application Management".
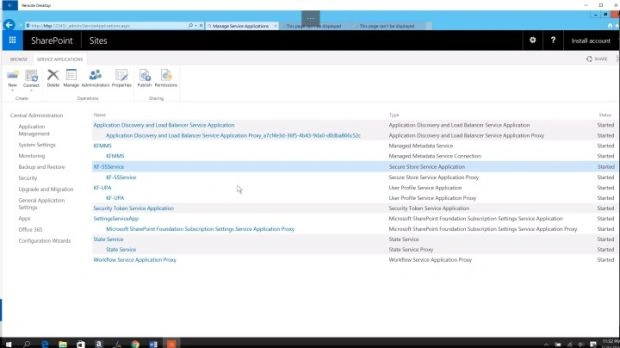
- Click on "Manage service applications" under Service Applications.
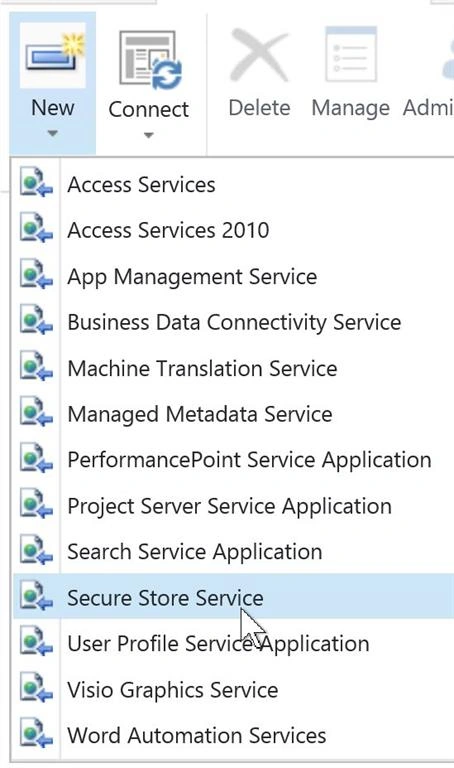
- Click on "New" (top left) and in drop-down, select Secure Store Service.
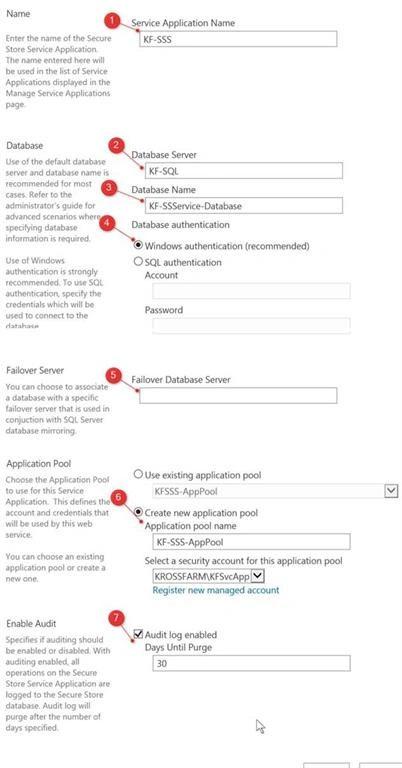
- On this page, please enter the details
- Service Application Name: KS-SSS
- Database Server: KF-SQL
- Database Name: KF-SSService-Database
- Database Authentication: Windows Authentication
- Failed Over Database Server: We are using Always-ON solution, so this will be blank.
- Application Pool
- Application Pool Name: KF-SSS-AppPool
- Select the ID from DropDown: Krossfarm\KFSvcApp
- Enable Audit ( I would recommend to enable it because it will help you to audit every action [who did, what did, success etc]).
- Audit Log Purge: Enable
- Days Until Purge: 30 Days
- Click "OK".
- This shouldn’t take long. Once it is completed, you will see this -
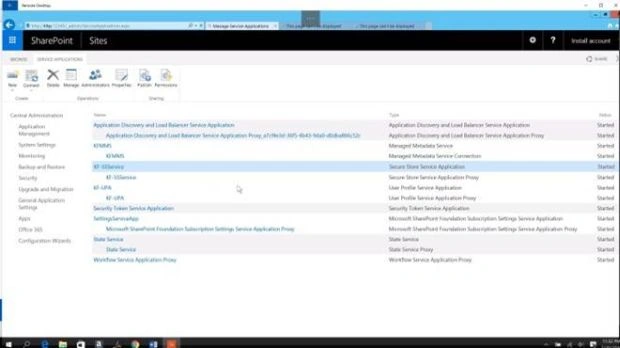
Check
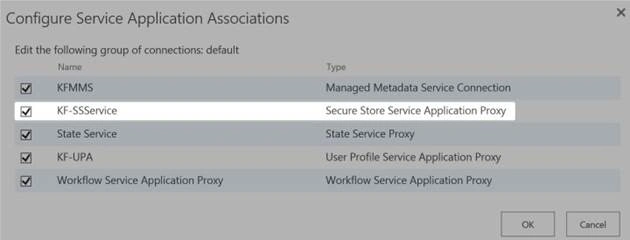
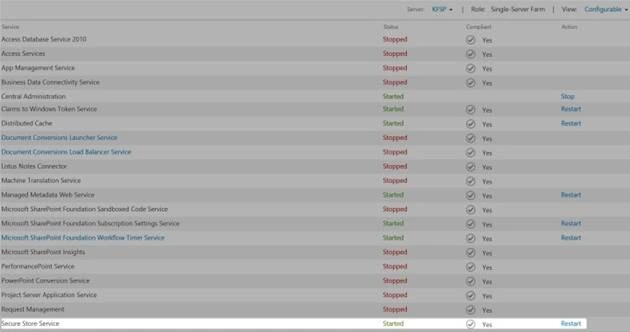
Please check a couple of things to make sure it is successfully created. Make sure that Secure Store Service Application Proxy is part of the Default Proxy group. Also, ensure that Secure Store Service Application Instance is started on the Server.
Check for Default Proxy Group
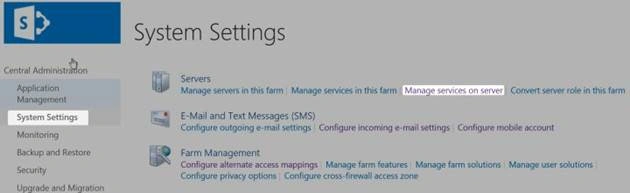
- On Application Management page, click on "Configure service application associations" under "Service Applications".
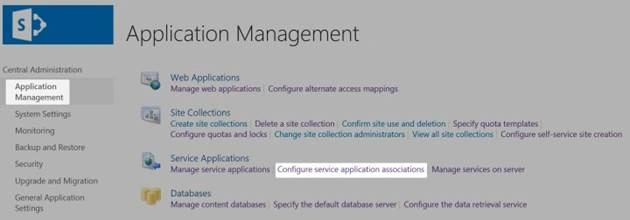
- On this page, click on the Default.
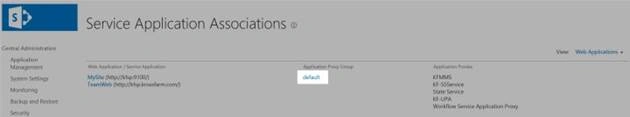
- On this page, please make sure SSS is checked here.

Join the conversation! Your thoughts help the community grow.