
Introduction
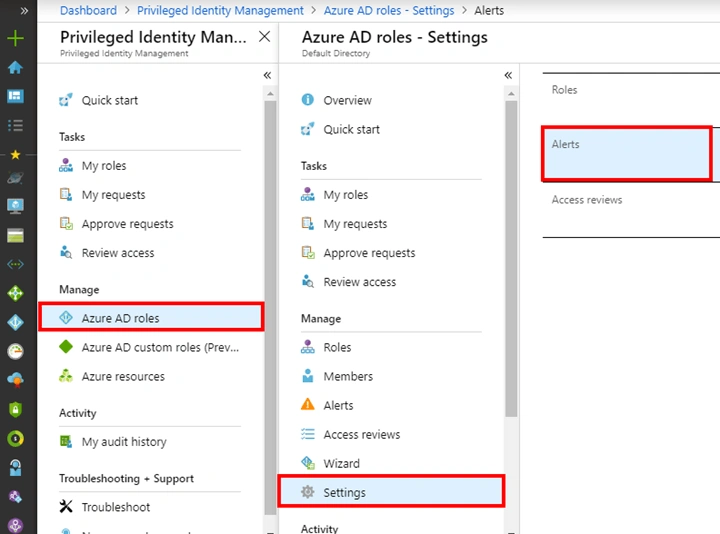
Azure Privileged Identity Management (PIM) creates alerts when there is suspicious or dangerous activity in your organization. At the point when an alert is activated, it appears on the PIM dashboard.
|
Alert
|
Trigger
|
Recommendation
|
|
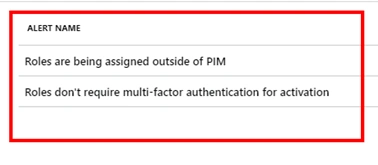
Roles are being assigned outside of PIM
|
An administrator was permanently assigned to a role, outside of the PIM interface.
|
Review the new role task. Since different administrations can just allocate administrators, change it to a qualified task if important.
|
|
Roles are being activated too frequently
|
There were too many re-activations of the same role within the time allowed in the settings.
|
Contact the client to perceive any reason why they have enacted the role so often. Perhaps as far as possible is unreasonably short for them to finish their tasks, or perhaps they're utilizing contents to go around the procedure.
|
|
Roles don't require multi-factor authentication for activation
|
There are roles without MFA enabled in the settings.
|
We require MFA for the most highly-privileged roles, but strongly empower that you empower MFA for activation of all roles.
|
|
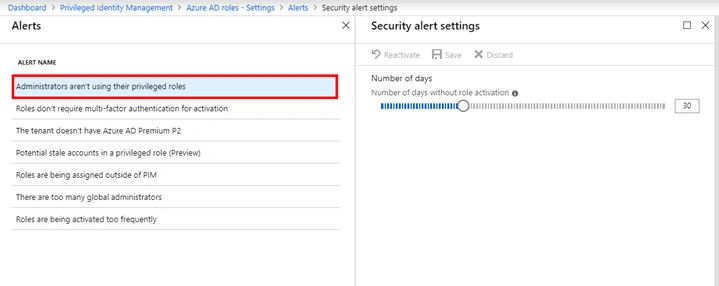
Administrators aren't using their privileged roles
|
There are temporary administrators that haven’t activated their roles recently.
|
Start an access review to decide the clients that needn't bother with access any longer.
|
|
There are too many global administrators
|
There are more global administrators than recommended.
|
On the off chance that you have a high number of worldwide administrators, almost certainly, clients are getting a bigger number of consents than they need. Move clients to less privileged roles or make some of them eligible for the role instead of permanently assigned.
|
Sana KamalPosted Sep 15, 2019, 3:10 AM
Good Explanation