
In this article, I’m going to write a bit about security aspects in ASP.NET Core 2.0.
Whenever you create a new ASP.NET Core application, you will notice that there is an option on the dialog with a button captioned Change Authentication, and once you click on that, you will land upon a dialog having the below 4 options.
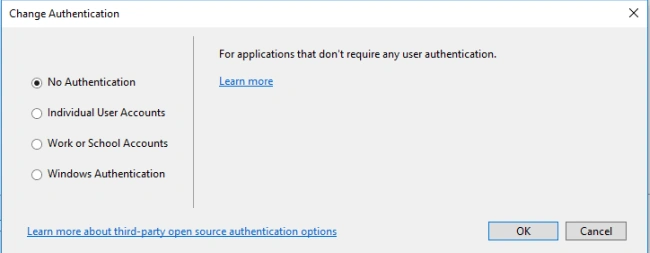
I’ll discuss each of these options in detail but as of now, to get started, let’s take a high-level idea about these.
I’ll discuss each of these options in detail but as of now, to get started, let’s take a high-level idea about these.
- No Authentication – This means the application is completely anonymous and open for everyone to access it.
- Individual User Accounts – It uses a local database for storing the information related to the user.
- Work or School Accounts – It means the application will work with Office365, Active Directory, support for cloud, etc..
- Windows Authentication – For internet applications, it and uses IIS capabilities to know who has logged in.
Once you click OK, you will notice that ASP.NET Core has added the required middleware in ConfigureServices method with a default token provider, as shown below.
- public void ConfigureServices(IServiceCollection services) {
- services.AddDbContext < ApplicationDbContext > (options => options.UseSqlServer(Configuration.GetConnectionString("DefaultConnection")));
- services.AddIdentity < ApplicationUser, IdentityRole > ().AddEntityFrameworkStores < ApplicationDbContext > ().AddDefaultTokenProviders();
- services.AddMvc().AddRazorPagesOptions(options => {
- options.Conventions.AuthorizeFolder("/Account/Manage");
- options.Conventions.AuthorizePage("/Account/Logout");
- });
- services.AddSingleton < IEmailSender, EmailSender > ();
- }
- public void Configure(IApplicationBuilder app, IHostingEnvironment env) {
- if (env.IsDevelopment()) {
- app.UseBrowserLink();
- app.UseDeveloperExceptionPage();
- app.UseDatabaseErrorPage();
- } else {
- app.UseExceptionHandler("/Error");
- }
- app.UseStaticFiles();
- app.UseAuthentication();
- app.UseMvc();
- }
One important thing to notice in the above code snippet is the sequence in which middleware are configured. app.UserAuthentication is called after app.StaticFiles, which means we don’t want any of our static contents to be authenticated before rendering them on to the browser.
Are you thinking, why? Well, let’s understand this with a common example of the Login page.
Login page usually has static contents like css, image, etc. If we shuffle the sequence of both the statements, then the Login page will never ever come until the user is authenticated. Now, if the user is already authenticated, then why do we need Login page? Isn’t it an interesting analogy?
What happens on click of Register?
Now, quickly run the application and click on Register and register yourself, as shown below:
Login page usually has static contents like css, image, etc. If we shuffle the sequence of both the statements, then the Login page will never ever come until the user is authenticated. Now, if the user is already authenticated, then why do we need Login page? Isn’t it an interesting analogy?
What happens on click of Register?
Now, quickly run the application and click on Register and register yourself, as shown below:
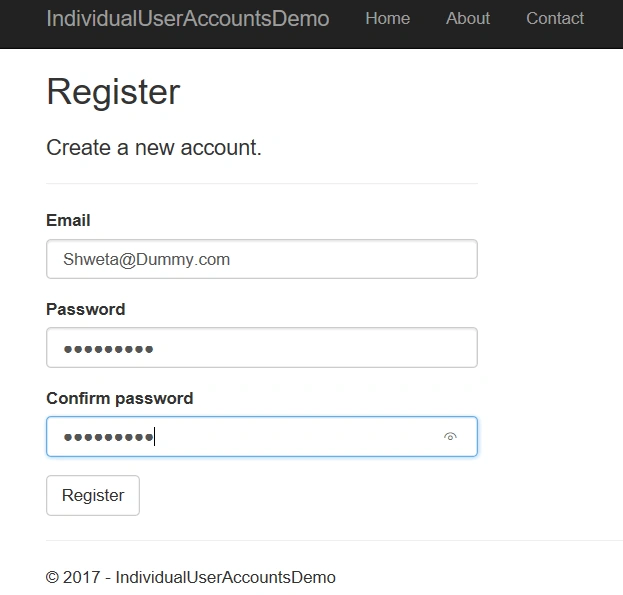
Once you populate the details and click on Register, you will land upon the below page.
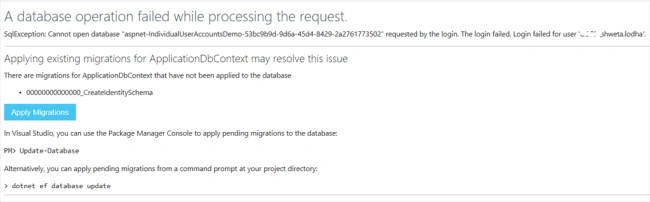
Nothing to worry about.
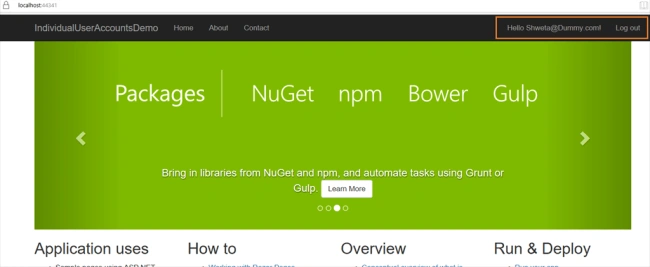
This is the expected behavior because our identity data is not stored anywhere. So, we have to create the required tables and for that, we can use local SQL Express database. This can be done quickly by pressing a button Apply Migrations as shown in the above screenshot. Once the button is pressed, just refresh your page and you would be happy to see the web page with your email id and Log out option in the top right corner, as shown below.
This is the expected behavior because our identity data is not stored anywhere. So, we have to create the required tables and for that, we can use local SQL Express database. This can be done quickly by pressing a button Apply Migrations as shown in the above screenshot. Once the button is pressed, just refresh your page and you would be happy to see the web page with your email id and Log out option in the top right corner, as shown below.
Saravanan GPosted Jul 13, 2018, 4:27 AM
Can you provide option for download this example?
Tridip BhattacharjeePosted Jun 7, 2018, 6:35 AM
Two-Factor Authentication option is there in asp.net mvc 5. why you did not use that....any reason?
Tridip BhattacharjeePosted May 17, 2018, 4:44 AM
Nice article madam. tell me what would be problem if you would use Individual user account option instead of No authentication. thanks