
Introduction
Often, we need to check if the generated Service Principal is using Azure AD App registration. A service principal can be defined as a secured identity that is used against an authorization endpoint, and on success, the authorization endpoint generates an Access Token, which has a limited lifetime, and using this access token, the application can perform required operations against the secured resource in Azure. The idea is to eliminate the usage of passwords to authenticate to the secured resource in Azure and have the application have fine grained and programmatic access to the resource secured by Azure. In this article, we are using the concept of OAuth2.0 Client Credentials Grant flow to obtain the Access Token. More about the OAUTH and service principals can be found in the references section.
Pre-requisites
- An Azure AD the App registered first using the Microsoft Entra App Registration process
- Obtain the Client ID and Client Secret of the Azure AD App.
- Configure the app to have write access to the SharePoint site.
Upload Files to SharePoint Online Library using POSTMAN
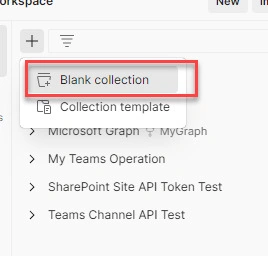
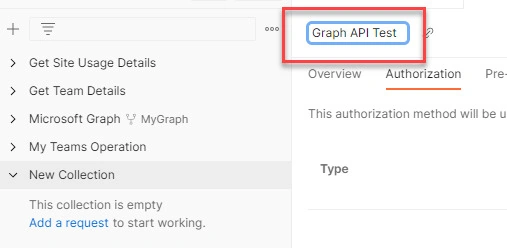
Step 1. Once the Postman tool is opened, on the left-hand side, create a collection by clicking on the + button and name it ‘Graph API Test’. This step is optional, as this will create a collection of requests that we could refer to for future reference.
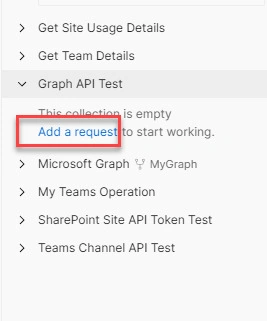
Step 2. Add new request. In the quick launch, click on the link ‘Add a request’.
Step 3. Update the request to ‘Get Site ID’, as this request is to get site ID using the graph API.
https://graph.microsoft.com/v1.0/sites/{TenantName}.sharepoint.com:/sites/{SiteName}
In this case, the URL is
https://graph.microsoft.com/v1.0/sites/gmfinancial.sharepoint.com:/teams/Dept-BusinessIntelligence
Input the URL and make sure the request is of type ‘GET’.
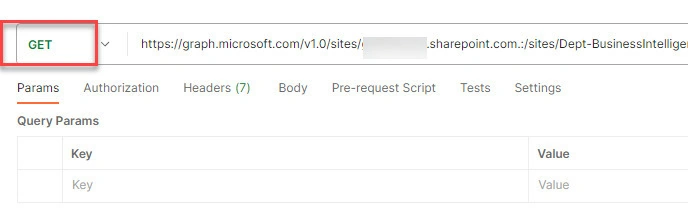
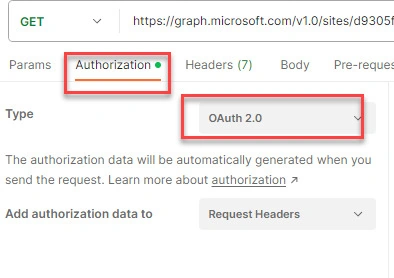
Step 4. Click on the Authorization tab, and Select the type ‘OAuth2.0’.
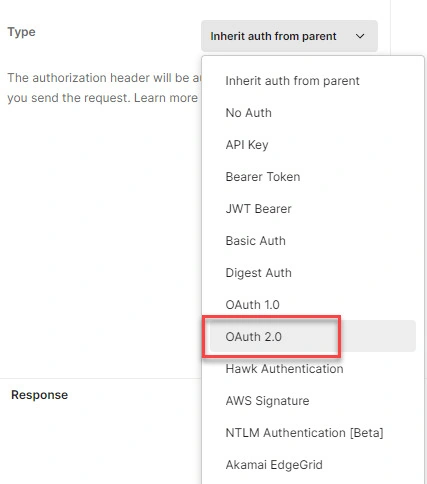
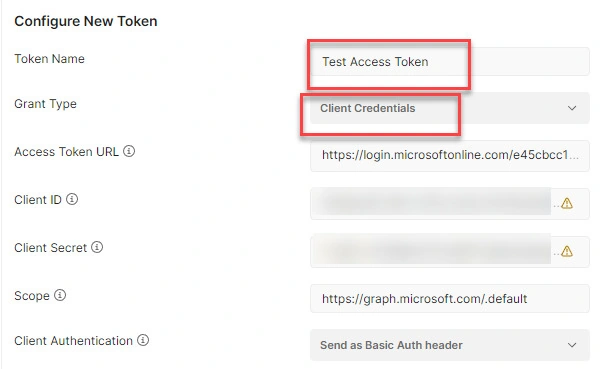
On scrolling down, you should see a section on the right side called ‘Configure New Token’. Enter the following details.
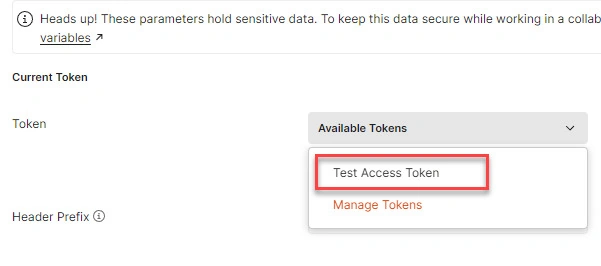
Token Name: It can be anything for your reference. I am entering it as ‘Test Access Token’.
Grant Type: Client Credentials, since we are using client ID and client Secret to get access tokens.
Access Token URL: it is in the format https://login.microsoftonline.com/{TENANTID}/oauth2/v2.0/token. Replace the Tenant ID with your organization's Tenant.
https://login.microsoftonline.com/e45cbcc1-1760-419a-a16b-35802285b3b3/oauth2/v2.0/token
Client ID: The client ID value while creating the Azure AD App Registration.
Client Secret: The client secret value. As mentioned in the reference article, Creating Azure AD app, when setting up client secret, the secret will only appear once during the initial setup and is required to save the secret value at the very first time.
Scope: Enter the scope value as https://graph.microsoft.com/.default
Client Authentication: Leave it as default, which is ‘Send as Basic Auth header’
Step 5. On scrolling down further, at the very end you should see the button called ‘Get New Access Token’. You should see the below option window that says ‘Authentication Complete’.
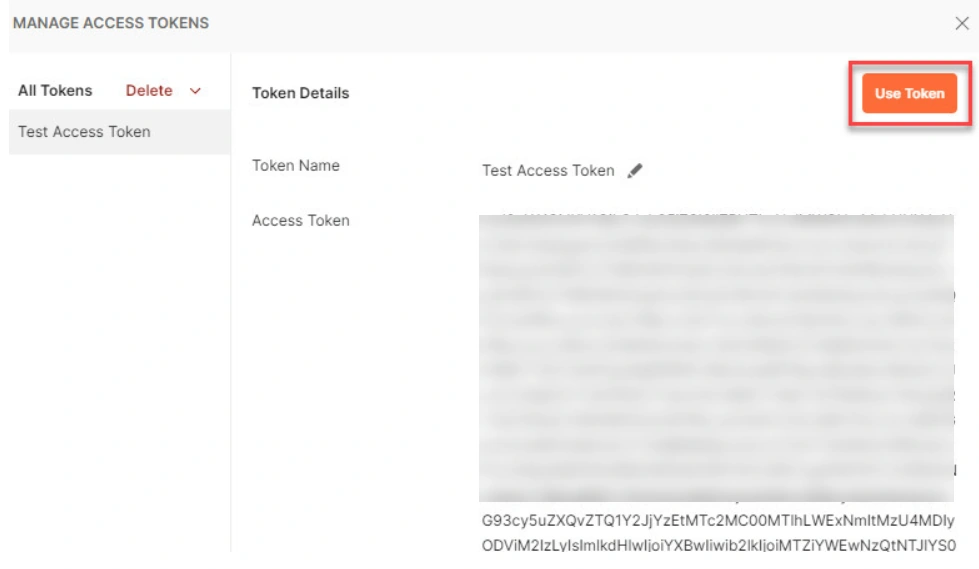
Immediately, there is another window that shows the output of the Access Token that was generated. Click on the button ‘Use Token’.
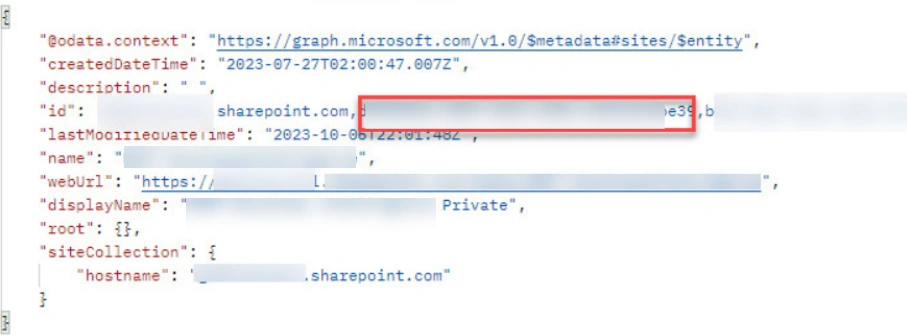
Step 6. Now click on ‘Send’. On success, you should see the message below in a JSON format, and the id column contains the Site Id value, which is the second string. Copy the Site ID. This will be used to retrieve the lists and libraries. In this case, the site ID is d9305f2d-bf54-4e16-ab0a-eafea6ddbe39.
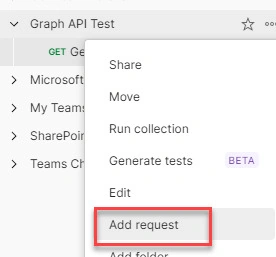
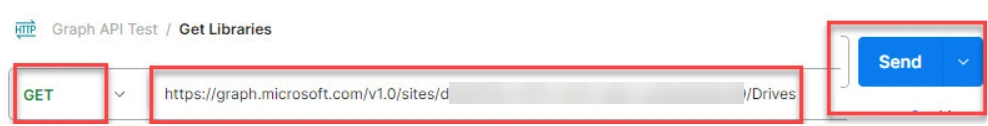
Step 7. Now, enumerate the libraries for the site. In the quick launch, click on the ‘Graph API Test’ tree options (…) and click on ‘Add request’ and name the request as ‘Get Libraries.
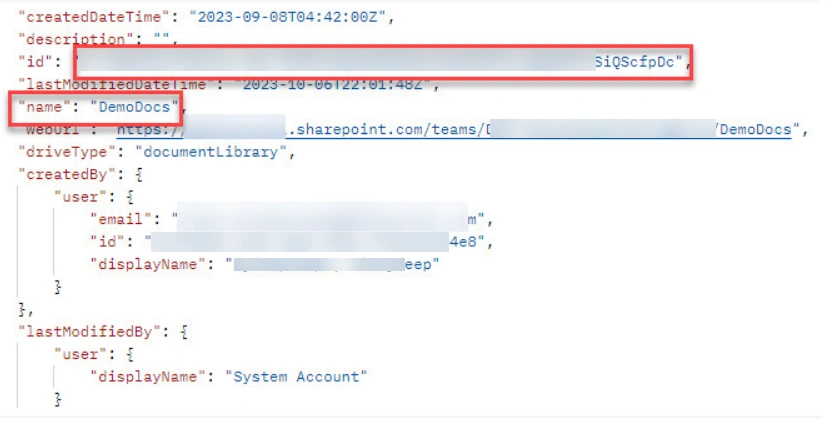
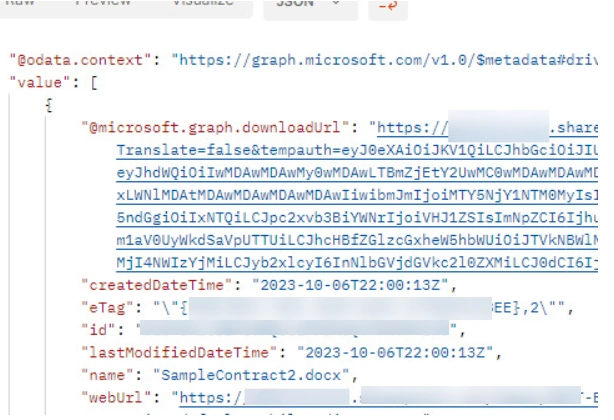
To get the all the libraries within the site, you need to use the below graph API request.
- https://graph.microsoft.com/v1.0/sites/{SITEID}/Drives
- https://graph.microsoft.com/v1.0/sites/abc123456-bcde-1122-abwe-ea122erw/Drives
Join the conversation! Your thoughts help the community grow.