
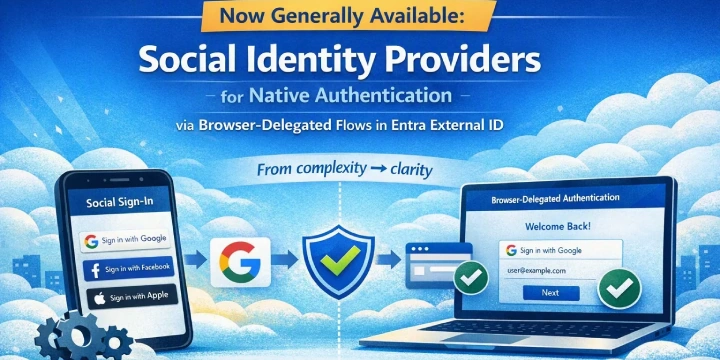
Redmond, WA — Microsoft has announced the general availability of Social Identity Providers (IdPs) for Native Authentication in its identity platform, enabling developers to integrate popular sign-in options like Google, Facebook, and Apple directly into native apps—without compromising security.
The update is part of Microsoft Entra External ID and introduces a hybrid approach that blends native app experiences with secure browser-delegated authentication flows.
Native Apps Finally Get Social Login - The Right Way
Until now, integrating social logins into native apps often forced developers into trade-offs between user experience and security compliance.
With this release, Microsoft enables developers to:
Add Google, Facebook, and Apple sign-in to native apps
Maintain app-native UI for onboarding
Use secure OAuth-compliant authentication flows
👉 The result: seamless user experience without handling sensitive credentials in app code
How It Works: Native UI Meets Web-View Security
Microsoft’s approach uses a browser-delegated (web-view) flow for authentication.
Here’s the flow:
User starts sign-in inside the app (native UI)
Authentication shifts to a secure web-view for the social provider
Additional steps like MFA are completed in the same flow
Tokens are issued back to the app
This ensures compliance with OAuth standards and provider security requirements, while still keeping the experience mostly native.
Why This Matters for Developers
Social login has become essential for modern apps—but it comes with challenges:
Security risks when handling credentials
Compliance requirements from providers
Poor UX when redirecting users out of apps
Microsoft’s solution addresses all three by:
Keeping credentials out of app code
Using standards-compliant authentication flows
Preserving native user experience where it matters most
Built for Conversion, Security, and Scale
Microsoft highlights key benefits for businesses and developers:
Faster onboarding with familiar login options
Higher conversion rates in consumer apps
Support for bring-your-own-identity (BYOI) scenarios
Enterprise-grade security with MFA and Conditional Access
This is especially important for apps targeting external users, customers, and partners.
What’s Available Now (GA Features)
With general availability, developers can now:
Enable social identity providers in native sign-in/sign-up flows
Authenticate users via web-view OAuth flows
Use Entra to issue ID and access tokens securely
Combine social login with advanced security policies like MFA
Join the conversation! Your thoughts help the community grow.