
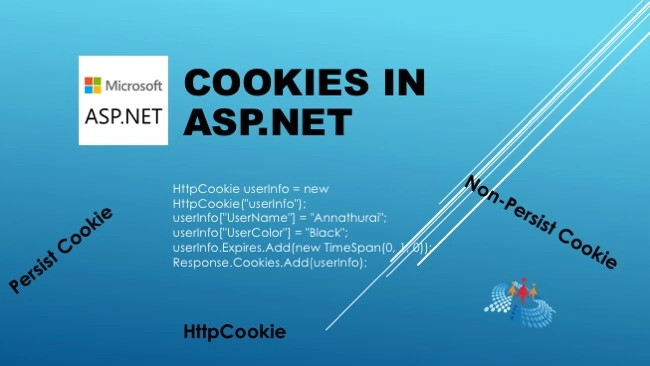
Cookies is a small piece of information stored on the client machine. This file is located on client machines "C:\Document and Settings\Currently_Login user\Cookie" path. It is used to store user preference information like Username, Password, City, PhoneNo, etc, on client machines. We need to import a namespace called System.Web.HttpCookie before we use cookie.
Type of Cookies
- Persist Cookie - A cookie that doesn't have expired time is called a Persist Cookie
- Non-Persist Cookie - A cookie which has expired time is called a Non-Persist Cookie
How to create a cookie?
It is really easy to create a cookie in asp.net with the help of a Response object or HttpCookie.
Example 1
HttpCookie userInfo = new HttpCookie("userInfo");
userInfo["UserName"] = "Annathurai";
userInfo["UserColor"] = "Black";
userInfo.Expires.Add(new TimeSpan(0, 1, 0));
Response.Cookies.Add(userInfo);
Example 2
Response.Cookies["userName"].Value = "Annathurai";
Response.Cookies["userColor"].Value = "Black";
How to retrieve from cookie?
It is an easy way to retrieve cookie value from cookies with the help of Request object.
Example 1
string User_Name = string.Empty;
string User_Color = string.Empty;
User_Name = Request.Cookies["userName"].Value;
User_Color = Request.Cookies["userColor"].Value;
Example 2
string User_name = string.Empty;
string User_color = string.Empty;
HttpCookie reqCookies = Request.Cookies["userInfo"];
if (reqCookies != null)
{
    User_name = reqCookies["UserName"].ToString();
    User_color = reqCookies["UserColor"].ToString();
}
When we make a request from the client to web server, the web server processes the request and gives a lot of information with big pockets, which will have Header information, Metadata, cookies, etc., Then respose object can do all the things with browser.
Cookie's common property
- Domain => This is used to associate cookies to domain.
- Secure => We can enable secure cookie to set true(HTTPs).
- Value => We can manipulate individual cookie.
- Values => We can manipulate cookies with key/value pair.
- Expires => This is used to set expire date for the cookies.
Advantages of Cookie
- It has clear text so the user can read it.
- We can store user preference information on the client machine.
- It is an easy way to maintain.
- Fast accessing.
Disadvantages of Cookie
- If the user clears the cookie information, we can't get it back.
- No security.
- Each request will have cookie information with page.
How to clear the cookie information?
- We can clear cookie information from client machine on cookie folder
- To set expires to cookie object
It will clear the cookie within one hour.userInfo.Expires = DateTime.Now.AddHours(1);
Ed EaglehousePosted Dec 24, 2020, 5:34 PM
The fact that there are multiple types for a cookie is is a design flaw in .Net Framework and ASP.Net framework. System.Net.Cookie (sending cookies to/from a server) and System.Web.HttpCookie (sending cookies to/from a client browser) both represent a web cookie (an HTTP construct). Unfortunately these types and their containers are not interchangeable nor linked by inheritance or many useful methods. Even more confusing is that HttpWebRequest and HttpWebResponse have containers for only Cookie, not the expected HttpCookie. A cookie must be manually converted between the two types to be added to a compatible collection. Note that as late as .Net 5.0, neither cookie type represented the SameSite attribute.
d pPosted Oct 13, 2020, 8:15 PM
Why cookies stored in Chrome not available in Incognito or Microsoft edge browsers, for same app and domain
Raju PrasadPosted Mar 19, 2019, 2:40 AM
HttpCookie is a class which belongs to System.Web NameSpace
Intekhab KhanPosted Feb 26, 2017, 5:13 AM
I think name space should be System.Net
Phaneendra ChakravaramPosted May 25, 2016, 7:33 AM
no system.web.httpcookie is not a name space
Naredla NitheshPosted Aug 31, 2015, 12:25 PM
have a look on the namespace "System.Web.HttpCookie" ,is it really a namespace?