
Introduction
This article shows how to change settings for insights for Microsoft 365 in associations utilizing Microsoft Graph Rest APIs.
In my past article, I covered essential inquiries for Insight settings customization. Underneath questions has been incorporated.
- What does the meaning of Insights Protection Settings?
- What does one need to keep in mind while changing the settings of Insights?
- How this progression will be affected to the behavior of UI in Microsoft 365?
It would not be a great idea to make copy content so i am not composing the same substance on this article that is included in my previous article. Please read basics on "Altering item Insights Security In Microsoft Graph Using PowerShell"
How to configure item insights Using Microsoft Graph REST API?
As expressed before, naturally, Insights security settings are empowered at the organizational level.
You can change the default in one of two different ways:
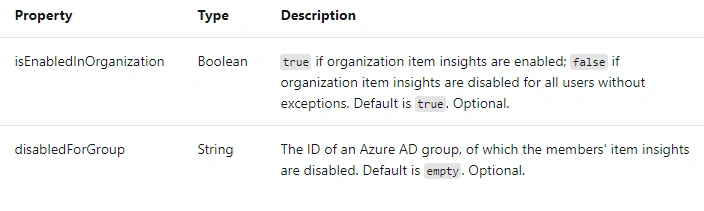
- User can impede/disable item Insights for all users in affiliation using isEnabledInOrganization property in itemInsightSetting resource
- User can impede/disable item Insights for a group of users/subset of users, which is assigned in Azure AD Group
- Using disabled for group property in itemInsightSetting resource
Important
- At the time of writing this article, API is under beta form in Microsoft Graph which is liable to change.
- Utilizing these APIs for production development can put you in truble.Utilize the version selector to check API is accessible in v1.0 or not.
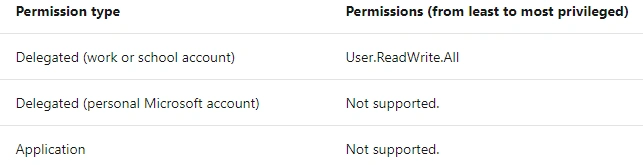
- To update ItemInsightPermission, the Application permission type is not supported yet. Only delegated permission is supported.
- To use delegated permission requires the signed-in user to have a global administrator Role.
 HappyCoding
Join the conversation! Your thoughts help the community grow.