
This series of articles, based on my previous working notes, discusses the main feature of the application security protection. The procedure is a security checking automation to figure out the potential security issues and give the developer a chance to fix them. My previous Security series of articles, such as Example Of Cross-Site Scripting, Reflected, was based on the security scanning tools to detect issues and to indicate the possible security vulnerabilities and solutions.
- Application Security (1), in General --- this article
- Application Security (2), Static Code Scanning --- Fortify
- Application Security (3), Open Source Security --- Sonatype
- Application Security (4), Dynamic Web Scanning --- WebInspect
A - Introduction
This article will introduce Application Security in general and roughly discusses Fortify, Static Code Analysis (SCA), Sonatype, Open Source Security (OSS), WebInspect, and Dynamic Web App Scanning. The content of this article is
- A - Introduction
- B - Application Security
- B - 0 - AppSec Overview
- B - 1 - Secure Code Training --- Earliest Stage of Software Development
- B - 2 - Security Tools plugins --- Early Development
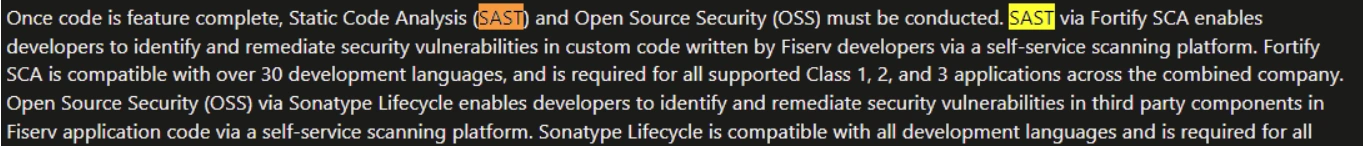
- B - 3 - Static Security Scanning --- after the code is completed
- B - 4 - Dynamic Security Scanning --- after code deployed
- B- 5 - MAST
- C - What is Fortify
- D - What is Sonatype
- E - What is WebInspect
- What is WebInspect?
- Who uses WebInspect?
- Why should we use WebInspect?
- Scope
B - Application Security
Here, we will describe the company Application Security process, although it is from one specific company, it might have generic sense for the process itself.
B - 0 - AppSec Overview
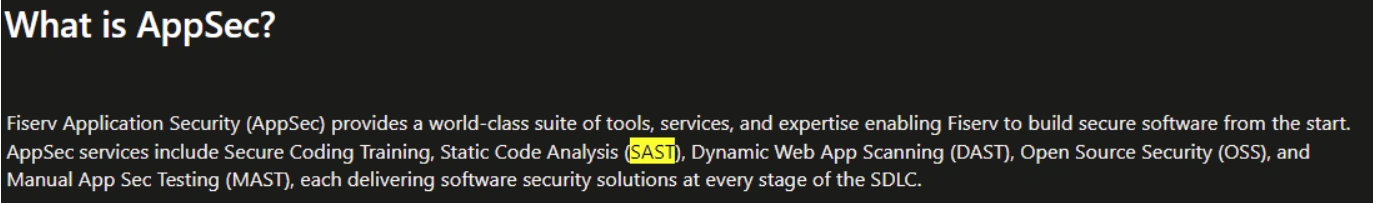
Company Application Security (AppSec) provides a world-class suite of tools, services, and expertise, enabling the Company to build secure software from the start. AppSec services include
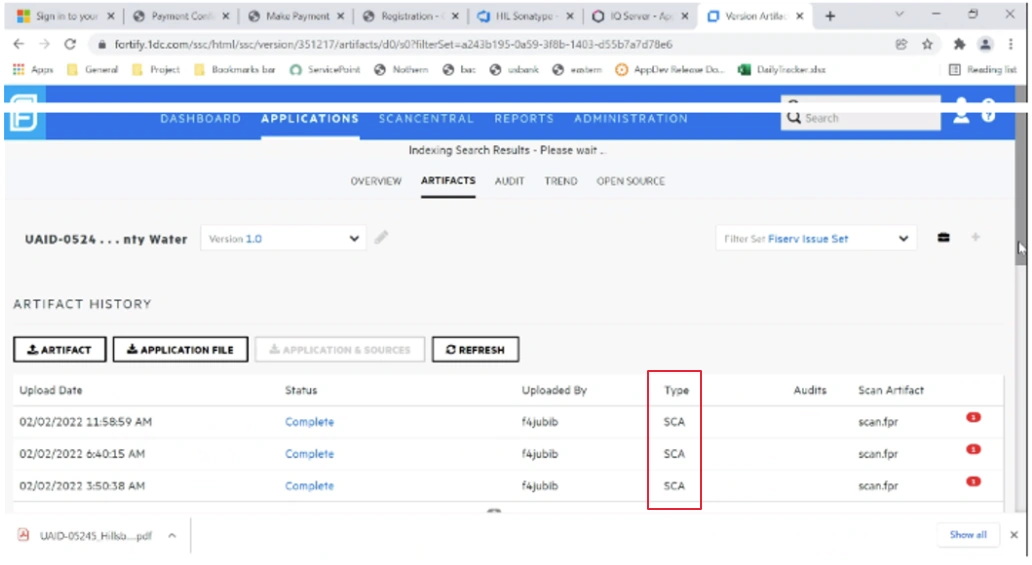
- Secure Coding Training (SCT), Static Code Analysis (SCA), --- Fortify
- Static Code Analysis (SCA)
- Statice App Sec Testing (SAST)
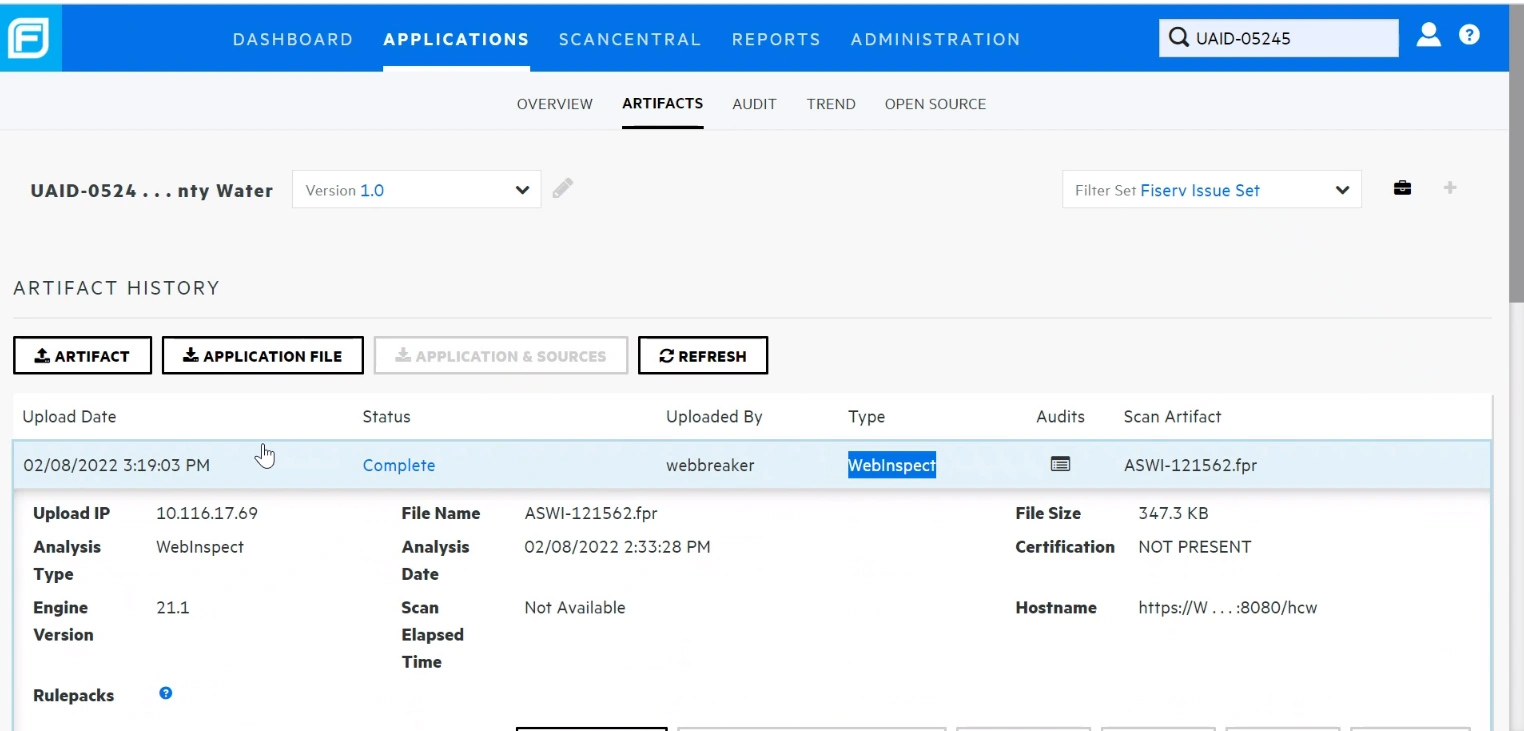
- Dynamic Web App Scanning (DWAS), --- WebInspect
- Dynamic App Sec Testing (DAST)
- Open Source Security (OSS), --- Sonatype
- Manual App Sec Testing (MAST)
B - 1 - Secure Code Training --- Earliest Stage of Software Development
-
A Secure Code Training is offered during the earliest stage of software development.

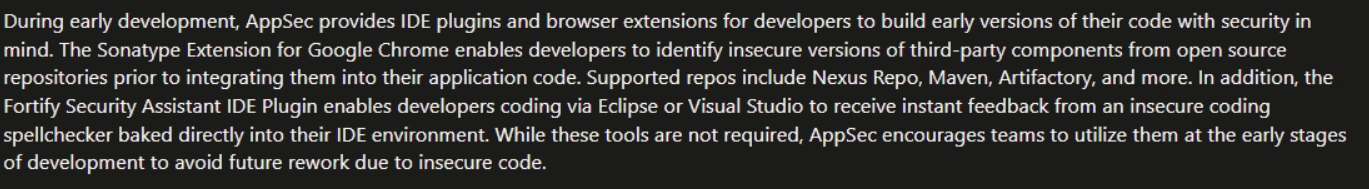
B - 2 - Security Tools plugins --- Early Development:
- Sonatype Extension
- Fortify Security Assistant IDE Plugin


Join the conversation! Your thoughts help the community grow.