
In this article we will learn how to store passwords in encrypted format during registration. We can also login to it by providing the correct credentials. Here the password will be stored in the database in an encrypted format so that no one is able to determine the password when he/she opens the database table.
Table Creation
-- phpMyAdmin SQL Dump
-- version 2.10.1
-- http://www.phpmyadmin.net
--
-- Host: localhost
-- Generation Time: Feb 13, 2013 at 05:52 AM
-- Server version: 5.0.45
-- PHP Version: 5.2.5
SET SQL_MODE="NO_AUTO_VALUE_ON_ZERO";
--
-- Database: `home_work`
--
-- --------------------------------------------------------
--
-- Table structure for table `employee`
--
CREATE TABLE `employee` (
`id` int(12) NOT NULL auto_increment,
`name` varchar(100) default NULL,
`address` varchar(100) NOT NULL,
`password` varchar(50) default NULL,
PRIMARY KEY (`id`),
UNIQUE KEY `name` (`name`)
) ENGINE=MyISAM DEFAULT CHARSET=latin1 AUTO_INCREMENT=2 ;
--
-- Dumping data for table `employee`
--
INSERT INTO `employee` (`id`, `name`, `address`, `password`) VALUES
(1, 'Raj', 'Pune', 'cac5ff630494aa784ce97b9fafac2500');
Note
Here the password "raj123" is stored in encrypted format.
Now let's move to the code.
Config.php
<?php
$DBHOST = "localhost";
$DBNAME = "home_work";
$DBUSER = "root";
$sLink = mysql_connect($DBHOST,$DBUSER,'') or die('Connection with MySql Server failed');
mysql_select_db($DBNAME, $sLink) or die('MySql DB was not found');
?>
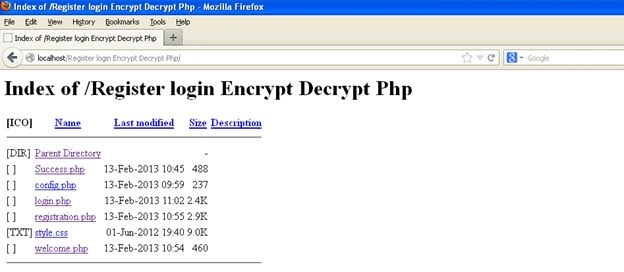
registration.php
<?php
session_start();
include('config.php');
?>
<!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Transitional//EN" "http://www.w3.org/TR/xhtml1/DTD/xhtml1-transitional.dtd">
<html xmlns="http://www.w3.org/1999/xhtml">
<head>
<meta http-equiv="Content-Type" content="text/html; charset=iso-8859-1" />
<title>Employee Registration</title>
<link href="style.css" rel="stylesheet" type="text/css" />
<script language="javascript" type="text/javascript">
function validation()
{
var formName=document.frm;
if(formName.name.value == "")
{
document.getElementById("name_label").innerHTML='Please Enter Name';
formName.name.focus();
return false;
}
else
{
document.getElementById("name_label").innerHTML='';
}
if(formName.address.value == "")
{
document.getElementById("address_label").innerHTML='Please Enter Address';
formName.address.focus();
return false;
}
else
{
document.getElementById("address_label").innerHTML='';
}
if(formName.password.value == "")
{
document.getElementById("password_label").innerHTML='Please Enter Password';
formName.password.focus();
return false;
}
else
{
document.getElementById("password_label").innerHTML='';
}
}
</script>
</head>
<?php
if($_REQUEST["action"]=='register')
{
$name=mysql_real_escape_string($_POST['name']);
$address=mysql_real_escape_string($_POST['address']);
$password=mysql_real_escape_string($_POST['password']);
$password=md5($password); // Encrypted Password
$sql="Insert into employee(name,address,password) values('$name','$address','$password');";
$result=mysql_query($sql);
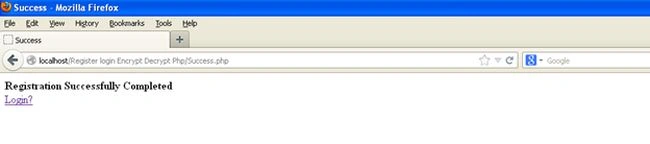
echo "Registration Successfully Completed";
echo "<script>window.location.href='Success.php'</script>";
}
?>
<body>
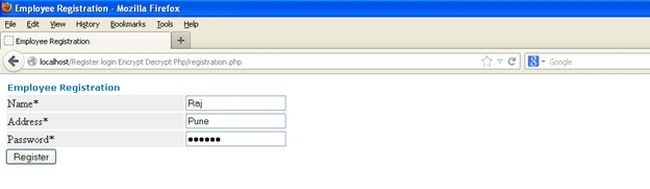
<form method="post" id="frm" name="frm" action="registration.php?action=register" onSubmit="return validation();">
<table width="500" border="0">
<tr>
<td class="deepbluetextbold"><b>Employee Registration</b></td>
</tr>
<tr>
<td class="colouredCell">Name*</td>
<td>
<input type="text" name="name" id="fullname" autocomplete="off" value="<?php echo $_REQUEST[name]; ?>"/> <label id="name_label" class="level_msg"></label> </td>
</tr>
<tr>
<td class="colouredCell">Address*</td>
<td><input type="text" name="address" id="email" autocomplete="off" value="<?php echo $_REQUEST[address]; ?>"/> <label id="address_label" class="level_msg"></label></td>
</tr>
<tr>
<td class="colouredCell">Password*</td>
<td><input type="password" name="password" id="password" autocomplete="off"/> <label id="password_label" class="level_msg"></td>
</tr>
</table>
</tr>
<tr>
<td>
<input type="submit" name="Submit" value="Register" /> </td>
<td> </td>
</tr>
</table>
</form>
</body>
</html>
Comments
Join the conversation! Your thoughts help the community grow.