
Introduction
Security is an essential part of an application and it should be taken into consideration from the grass-roots level of an application's design. Security is all about protecting your assets from unauthorized actions.
But Code Access Security (CAS) is a feature of .NET CLR that enables you to control the permissions that an individual .NET application has on your system during its execution. As a developer, you must understand how to create applications that work, even when some permission is restricted or to restrict your application from performing certain tasks, for example, a user can't delete/create a file in the "C:\Windows" directory.
Security Model
When you perform some action on the user interface, such as click a button, your application connects to the internet, downloads the modules into the Download Assembly Cache, and begins executing. Behind the scenes, what evidence do you actually have that you can trust the code your computer is downloading?
.NET enforces security polices around assemblies. It uses the evidence that an assembly has, such as the origination of the file. The runtime places all code from the local intranet into a specific group. It then uses the security policies to decide what permissions the code should be granted at a granular level.
MSIL Verification
When .NET code is compiled, the output it produces is an intermediate language (IL) code that requires a runtime to execute the IL. So during assembly load at runtime, it first validates the metadata then examines the IL code against this metadata to see that the code is type safe. When MSIL code is executed, it is compiled Just-in-Time and converted into a platform-specific code that's called native code.
Thus any code that can be converted to native code is valid code. Code that can't be converted to native code due to unrecognized instructions is called Invalid code. During JIT compilation the code is verified to see if it is type-safe or not.
To determine whether your code is verifiably type safe, you can use the "peverify" utility at the .NET command prompt as in the following;
peverify ConsoleApplication1.exe
After executing the aforementioned command, you will get the following output:
All classes and Methods in ConsoleApplication1.exe Verified
Code Access Security
Code Access Security enables users to restrict, on a very granular level, what managed code can do according to a level of trust. If the CLR trusts the code enough to allow it to run then it will begin executing the code depending on the permissions given to the assembly. If the code is not trusted and attempts to perform some action it does not have relevant rights for then a security exception is thrown.
It is important to understand that code access security is about protecting resources, such as directories, local drives, event logs, user interface and the network from malicious code. It is not primarily a tool for protecting software from users.
Code Access Security can be applied only to managed applications. Unmanaged applications run without any CAS restrictions and are limited only by the operating system's role-based security. If CAS is used to restrict the permissions of an assembly then the assembly is considered partially trusted. Partially trusted assemblies must undergo CAS permission checks each time they access a protected resource. Fully trusted assemblies, like unmanaged code, can access any system resource that the user has permissions to access
Elements of Code Access Security
Every security system needs some sort of mechanism (such as user name, password and Access Control List (ACL)) to identify the users and determine what a user can or can't do. However CAS identifies and assigns permissions to application rather than to application users.
CAS identifies assemblies using evidence, there are a few elements by which an assembly can be identified, such as location, hash code and signature of the assembly. Evidence is the information that the runtime gathers about an assembly to determine which code group the assembly belongs to. Code groups in turn grant an assembly a permission set.
Components Of Code Access Security
Code Group
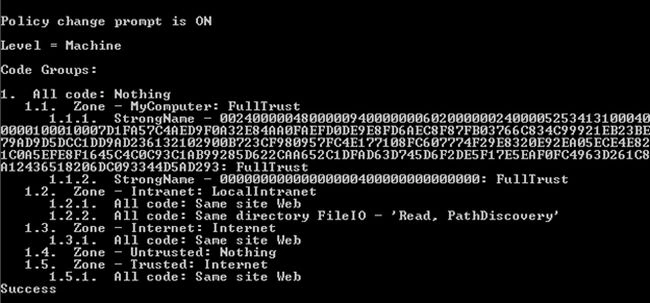
The evidence provided by an assembly is used as the condition for granting and revoking permissions to it. It is done by putting the code in an appropriate code group. Every code group stipulates a membership condition and has specific conditions attached to it. Any assemblies that meet the condition become a member of the group. Code groups are arranged in a hierarchy and assemblies are nearly always matched to several code groups. The code group at the root of the hierarchy is called All Code and contains all other code groups.
Evidence
In order for the CLR to determine which code group to place assembly information into, the first step is to read supplied evidence. There are two main sources of information, they are internet and intranet. The group internet defines code that is sources from the internet and the group intranet defines code sources from a LAN. The examination of the assembly evidence makes the authentication part of the security process. The following table depicts the major type of evidence an assembly can present to the CLR.
| Evidence | Description |
| Zone | The region such as intranet, local, trusted from which the code originated. |
| URL | The specific URL from which the code originated. |
| Strong Name | Unique verifiable name for the code. |
| Site | The website from which the code originated. |
| Harsh Value | The hash value of the assembly contents. |
| Publisher | The assembly digital signature that uniquely identified the developer. |
| Application Directory | The directory in which assembly resides. |
Permissions
Permissions are the actions you allow each code group to perform. The system administrator usually manages the permissions at the enterprise, machine and user levels. The CLR Virtual Execution System (VES) loads and runs programs. It provides the functionality required to execute managed code and uses assembly metadata to connect modules together at runtime. When VES loads an assembly, it matches the assembly to one or more code groups. Each code group is assigned to one or more permissions that specify what actions assemblies can do in that code group.
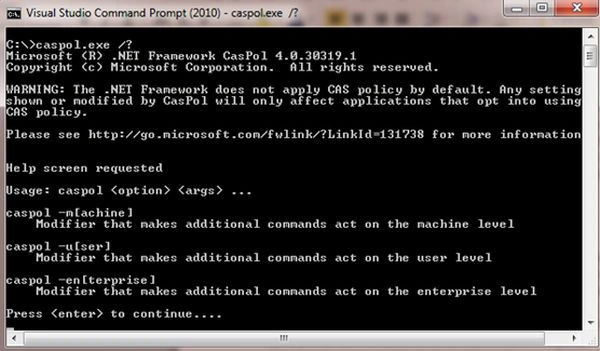
Note: mscorcfg.msc is no more a part of .NET 4.0; you can use caspol.exe instead to do the same work.
Permissions Sets are unique combinations of security configurations that determine what each user with access to a machine can do on that machine. There are several permission sets shipped with the .NET Framework as in the following table:
| Permission | Description |
| FullTrust | Allow full access to all resources. |
| Everything | Allow full access to all resources (group isn't added to assembly list) |
| Internet | Grant Default rights. |
| SkipVerification | Bypass all security verification |
| Nothing | Denies all access including Execution |
| Execution | Allows execution-only access. |
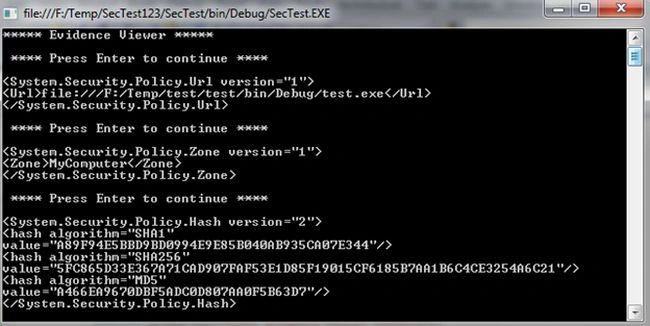
We will now create simple applications that will hard-code the name of an assembly with full path to load it into memory. At this point, we will enumerate over each supplied form of assembly evidence and print the data to the console window.
To begin, the Program type provides a Main() method that allows users to enter the full path to the assembly they wish to evaluate. We will pass the Assembly reference to another helper method named DisplayEvidence(). The following is the story so far:
using System;
using System.Collections;
using System.Security.Policy;
using System.Reflection;
Anant DhasPosted Apr 8, 2017, 1:46 AM
Very well.....>>>>>
Sonu ChaudharyPosted Apr 26, 2016, 4:01 AM
good one...
Kuppurasu NagarajPosted Apr 11, 2016, 1:56 PM
Nice Sharing...