
Introduction
Cybersecurity’s main objective is to manage the security of all IT devices and software applications that manage data. In recent years, the number of vulnerabilities is on the rise, and organizations need to be more secure handling customer data and general organizational data, depending on its importance. Given the number of vulnerabilities that have rapidly increased, organizations now need to optimize which vulnerabilities they should deal with first. This article discusses the Common Vulnerability Scoring System (CVSS), a vulnerability management tool that organizations may use to identify which vulnerabilities they need to prioritize depending on their numeric severity as calculated by the Common Vulnerability Scoring System (CVSS).
Common Vulnerability Scoring System (CVSS)
The CVSS is a sophisticated, free, and standard tool for assessing the severity of computer system security vulnerabilities. Using formulae, the tool tries to match severity scores to vulnerabilities prompting organizations and general users to prioritize their security responses and resources according to the amount of threat. The scores range between 0.0-10.0 and are metric-based formulae that are comprised of different characteristics of the vulnerability, including its impact and environmental endurance over time.
The CVSS comprises 3 metric groups, namely Base, Temporal, and Environmental metrics, which are all used to determine the severity of a vulnerability using different approaches. Each metric is assigned a description that is associated with a numerical value.
The Base Metrics Group
This is made up of two metrics the Exploitability metrics and Impact metrics. It is concerned with the natural characteristics of the vulnerability which will not change in time or due to various user environment platforms.
- The Exploitability metrics – The Exploitability metrics show the characteristic ‘part that is vulnerable’ formally referred to as the ‘vulnerable component’. Every metric under the Exploitability should be scored according to the vulnerable component showing the properties of the vulnerability which lead to the vulnerable component’s successful attack. Basic metric scores assume that that attacker has in-depth knowledge of the target system which includes basic configuration and general defense mechanisms. This means that if an attacker requires others beyond general configurations to successfully exploit the vulnerability it will not be included in the CVSS Base scoring. Most organizations only use the Base Metric Group to rate their systems.
Example
Exploitability metrics – Attack Vector (AV)
|
Value
|
Description
|
Score
|
|
Local(N)
|
In this form of attack, the perpetrator is likely to have an account or have physical access to the targeted system. e.g they may promote their access privileges
|
0.395
|
|
Adjacent Network(A)
|
An attack requires the perpetrator may have access to the collision domain or broadcast. E.g. Bluetooth
|
0.646
|
|
Network (N)
|
This may be perpetrated remotely e.g an attacker may cause a denial-of-service attack remotely.
|
1.0
|
Diagram
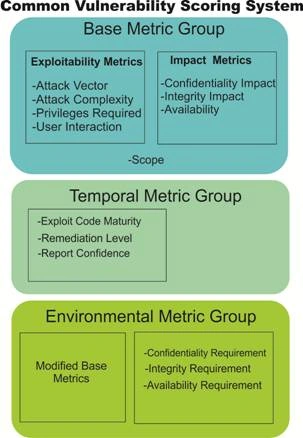
Exploitability metrics include:
- Attack Vector
- Attack Complexity
- Privileges Required
- User Interaction
- Impact Metrics
This metric is mainly concerned with the impact or effects of the successful attack on the system. The Impact is resolved using:
- Confidentiality Impact
How much sensitive information was accessed and the effects of losing that information.
- Integrity Impact
This is concerned with the amount of manipulation the affected data was exposed. Organizations normally check if they can restore the data and trust or it may be severe that it may cause disrepute to the organization.
- Availability Impact
Normally this impact refers to the state of the affected system. Organizations are concerned if they can still access the affected system and restore functionality or at times they may have completely lost the system.
Temporal Metric Group
These metrics measure the techniques used in the exploit of the vulnerability. It checks for patches, workarounds, or confidentiality of the vulnerability description. Remediation Level (RL) values include the availability of a patch or a possible workaround that may be used to mitigate the vulnerability. At its best value, it gives options for a Temporary fix or an Official way to patch the vulnerability and completely mitigate the vulnerability Temporal Metrics consists of:
- Exploit Code Maturity (E)
- Remediation Level (RL)
- Report Confidence
Environmental Metric Group
Environmental metrics are an improvement of Base metrics, in that their analysis is based on the value of the affected IT asset to the organization, depending on the organization’s security implementation. They are more concerned with the security controls which are put in place by the organization and these will be used to determine the score. They check the Confidentiality; Integrity and Confidence measures put in place by the particular organization and use these to calculate the eventual score comparing each of the three attributes. Their metric values can be defined among High, Medium, Low, or Not Defined. This metric is normally used by end-users of a system to determine their risk after checking their particular security environment.
Environmental metrics are comprised of:
- Security Requirements (CR), (IR), (AR)
Conclusion
At the end of each metric group, i.e Base, Temporal, and Environmental, a special formula is used to calculate a score and this score is used in decision making as to which vulnerability is prioritized. Organizations may secure themselves by doing so.
Join the conversation! Your thoughts help the community grow.