

In this article, we will discuss how to create a self-signed certificate in mac os as well as Windows. Also, we will look into what the use of that is and where we can use it.
At an API call time, security is the most important thing that needs to persist, and client secrets are the common methods to use for authentication in Azure Active Directory. Certificate-based authentication is a better choice in terms of security and validity.
For the Azure APP, there are two types of Certificates which is required
.cer - to upload to App registration
.pfx - to upload your Azure function app
Prerequisites
Azure subscription
Azure AD App registration permissions
.Net 6 or later version installed in your local
PowerShell
Basic knowledge of Azure function
Let`s start with macOS,
There are two easy ways to create a self-signed certificate in macOS.
By command
Using Keychain app
By command:
Open PowerShell in your mac if it is not installed then download from here for mac os.
Once PowerShell is installed then run the below command. you can replace MyAzureFUnctionCert with your preferred certificate name.
openssl req -x509 -newkey rsa:2048 -keyout MyCertificate.key -out MyCertificate.cer -days 365 -nodes -subj "/CN=MyAzureFunctionCert"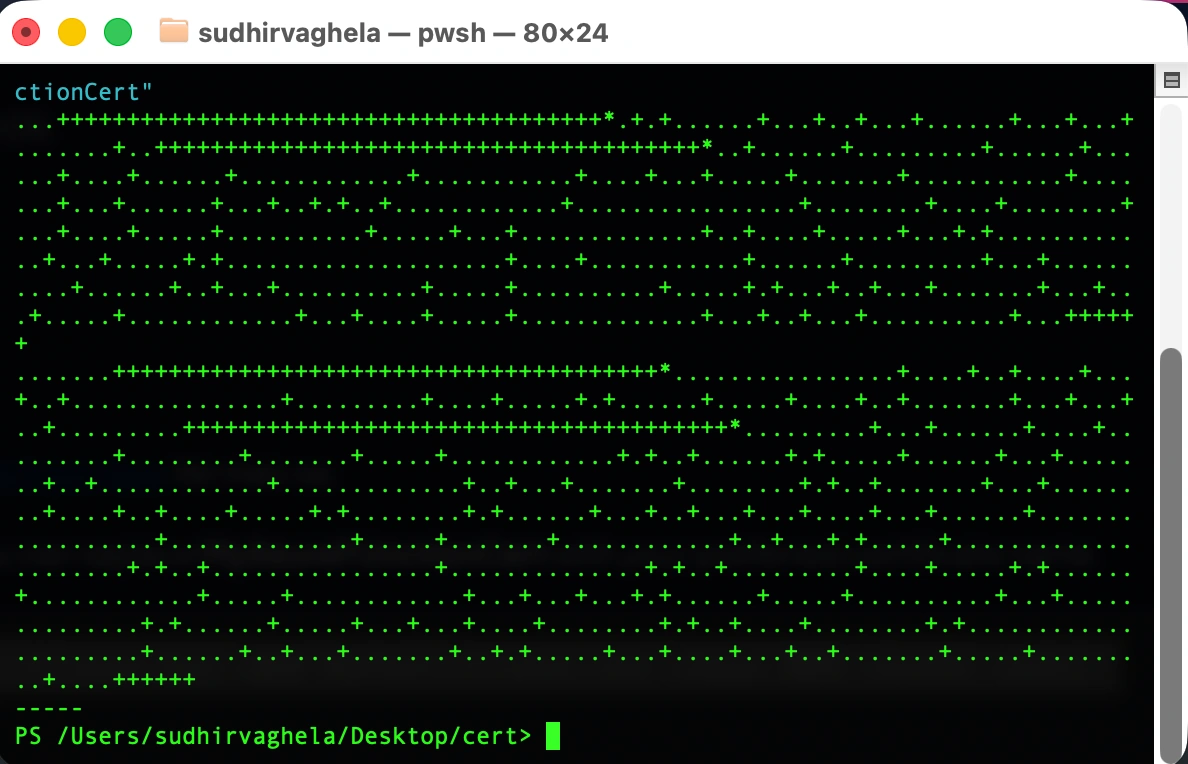
When you paste that command and hit enter, it will show this kind of result like (…...) and (+++++++) signs which is ok. It is a part of certificate generation.
Now, paste below command, you can replace MyCertificate with your preferred certificate name.
openssl pkcs12 -export -out MyCertificate.pfx -inkey MyCertificate.key -in MyCertificate.cerThis command will generate an actual certificate and export it to your path. Also it will ask for a password to export certificates.
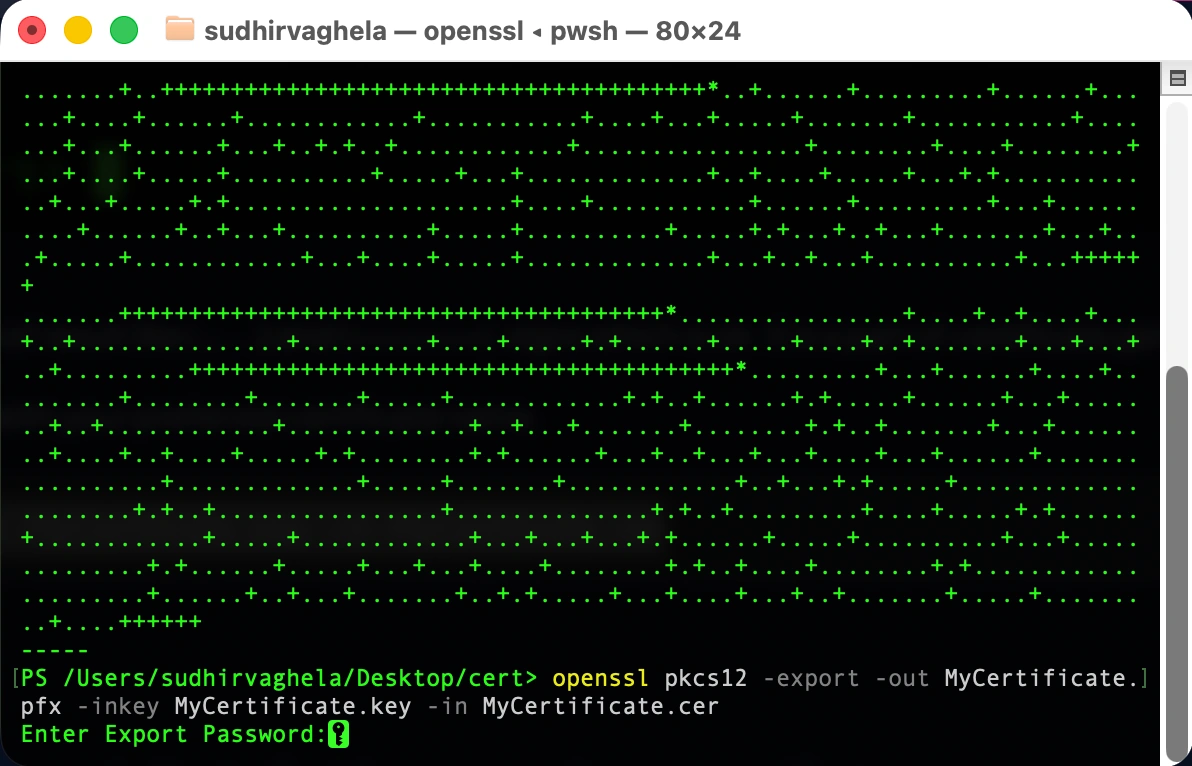
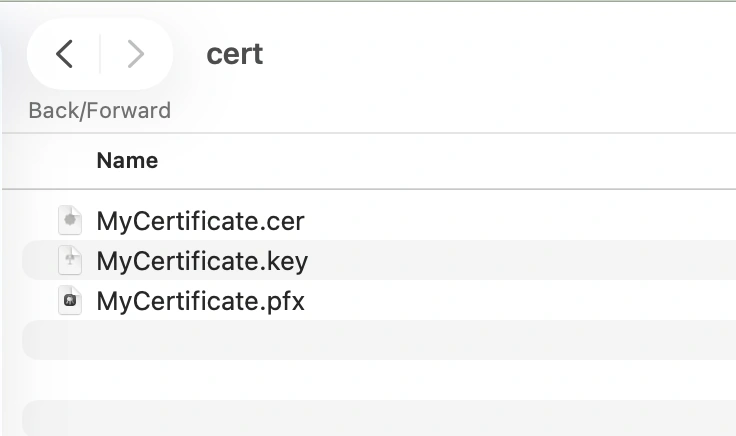
As you provide passwords it will give you a certificate you can check. I have it in my desktop folder like in the image below.
Now, let's jump into how we can generate certificates with the keychain app in mac os.
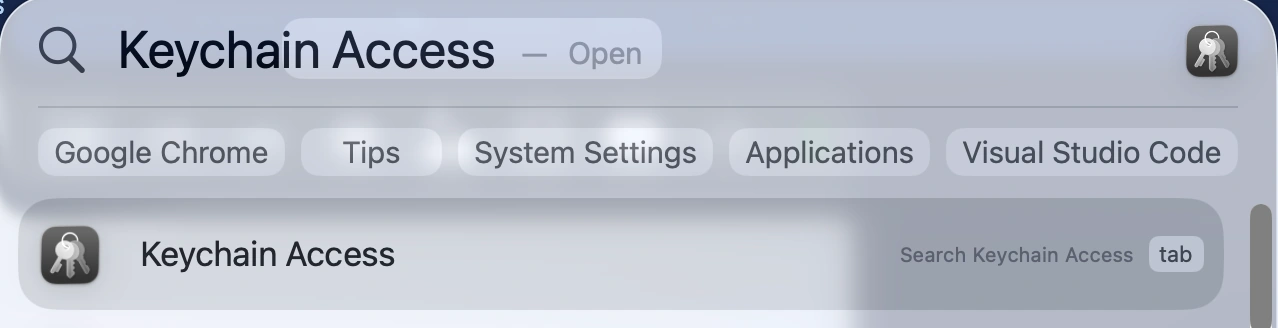
Search in Launchpad in mac or press cmd + shift and search Keychain it will show the app like in the image below.
Now once you click on that it will give you a small Model like shown in image below.
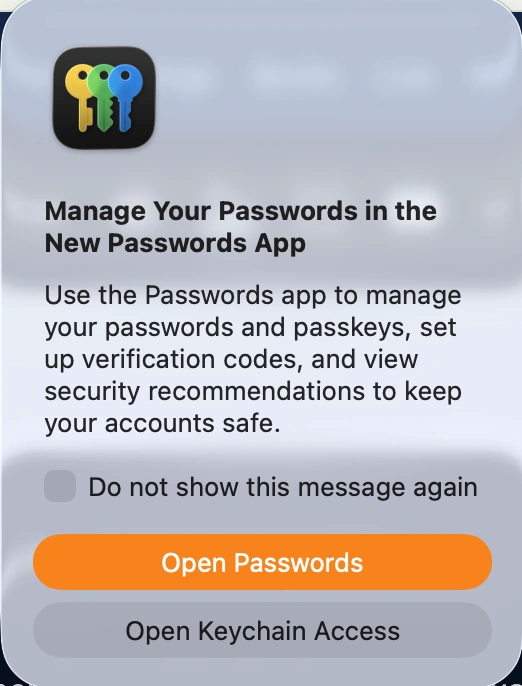
In this model click on the second button “Open Keychain Access” it will ask you a password of your system if you have and there will be another window open.
Now, click on Keychain Access as shown in image below.
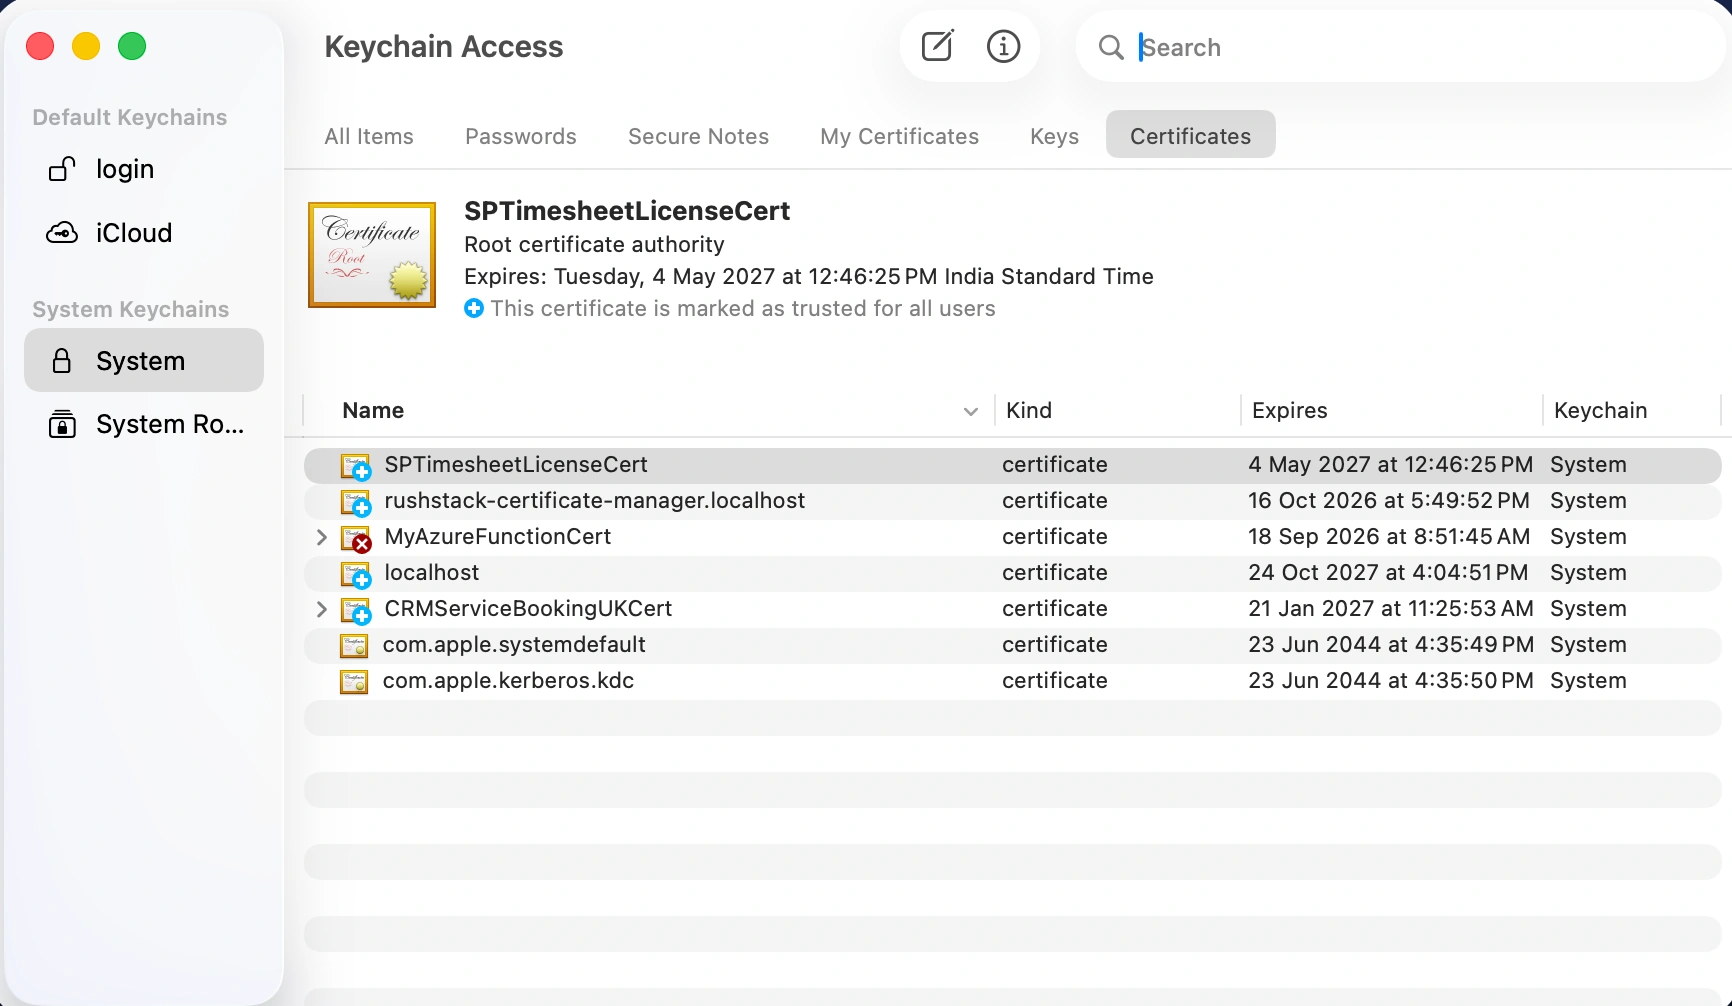
By clicking on Keychain Access it will open a below option.
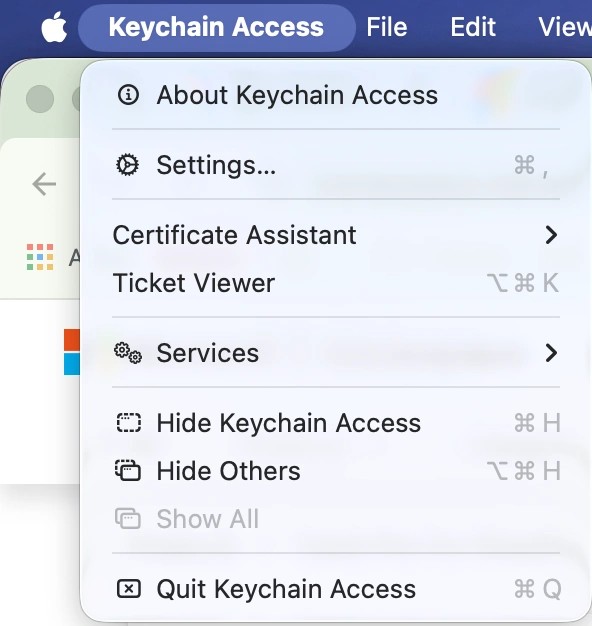
Certificate Assistant -> Create a Certificate this will give you an another window like in image below.
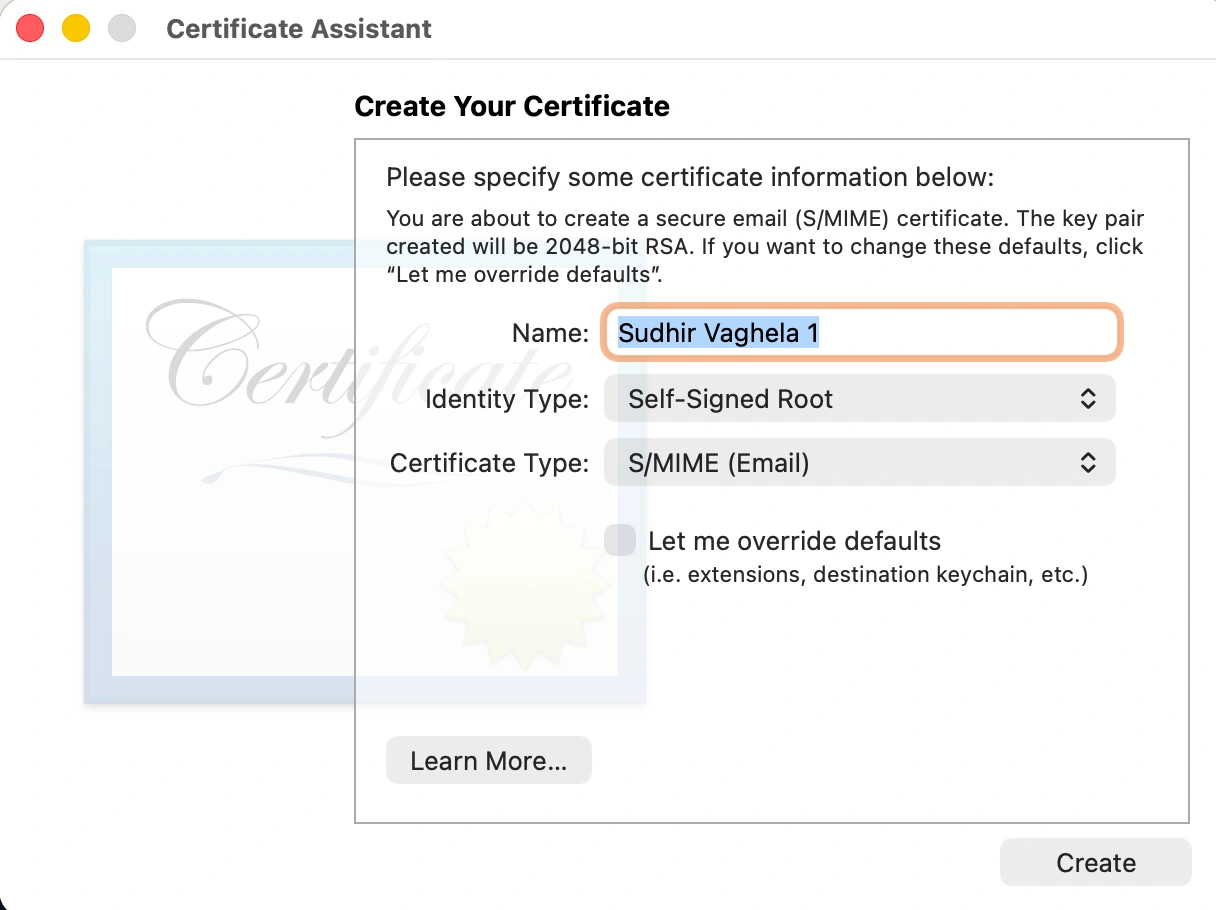
Now give a name to your certificate as you desire and select identity type to “Self-Signed Root” and Certificate type to “SSL Server” and click on Create button.
Once you create the certificates it will not be directly added to you system you will need to export it from the keychain access app.
Open you Keychain Access window and click on the login tab there would be your certificates which needs to export.
Now click on the certificate which you created and right click. It will open a new dropdown, select Export “MyCertificate” (name would be based on Certificate name).
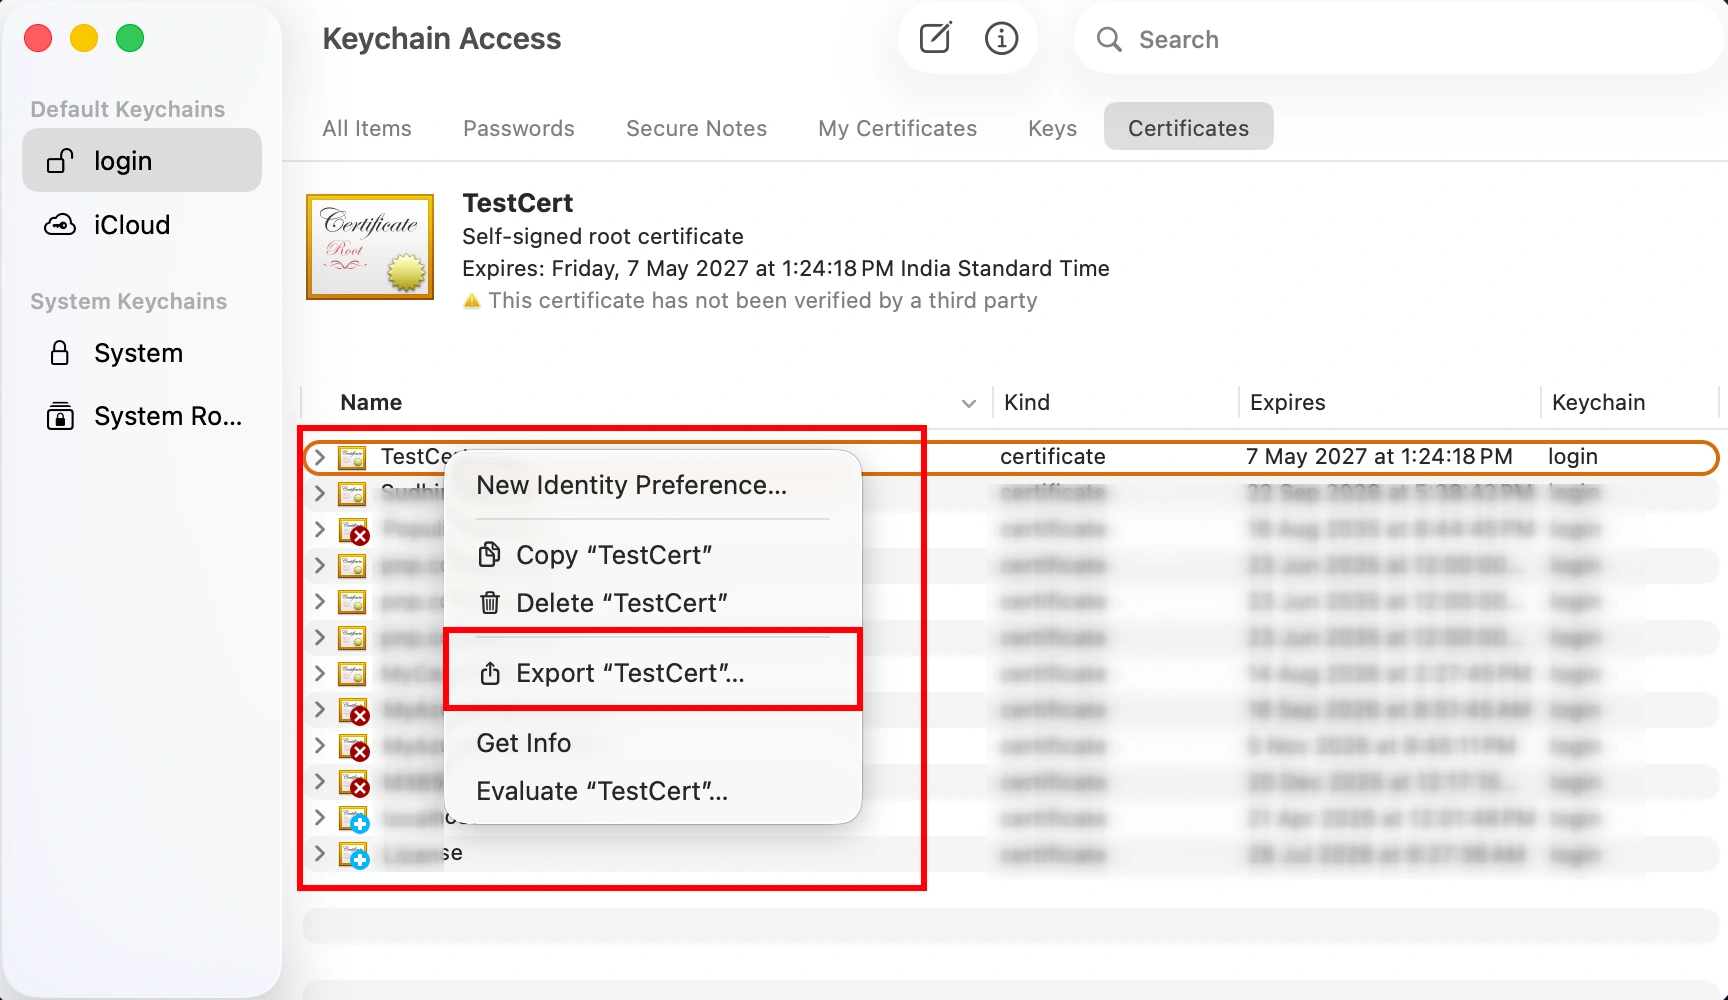
As you click on export “MyCertificate” it will give you another window to save in your system, and there is .cer formatted certificate to upload to APP Registration in Azure AD.
Now, we need to get .pfx formatted certificate to add in our azure function. To get that again go to Keychain access and below our certificate there is same name private key shown in image below.

Just right click and export, it will again show a save window but there would be that different format like .p12 just save and manually change the extension by yourself.

Now we have both easy scenarios to download Open SSL self signed certificate For Mac Os.
Now let see how to generate same certificates in windows
For windows there is a very simple way which is defined below, follow the below steps,
In windows open microsoft PowerShell terminal if it is not installed then download from here.
Once you download the PowerShell then open it and go to the folder or drive where you want to download those certificates.
Once you are at your desired location for download, run below commands which will generate those certificates.
For .cer certificate
$cert = New-SelfSignedCertificate -Subject "CN=MyAzureFunctionCert" -CertStoreLocation "Cert:\CurrentUser\My" -KeyExportPolicy Exportable -KeySpec Signature -KeyLength 2048 -NotAfter (Get-Date).AddYears(1)The above command stores self signed certificates in your windows certificate store.
Now export that .cer certificate.
Export-Certificate -Cert $cert -FilePath "$env:USERPROFILE\Desktop\MyCertificate.cer"This command will download that certificate with name “MyCertificate.cer”.
For .pfx certificate
$pfx = ConvertTo-SecureString -String "YourPfxPassword" -Force -AsPlainTextIn above command add your .pfx certificate Password as your need, which will be asked at import time.
Now export this certificate with the below command.
Export-PfxCertificate -Cert $cert -FilePath "$env:USERPROFILE\Desktop\MyCertificate.pfx" -Password $pwdNow, we have both .cer and .pfx certificates with a very easy approach for windows.
Now let's talk about why we use these certificates and what are the use cases in the real world.
Authentication
It actually acts as an ID card which says that “I am that one, who i claim to be”. Just like a password that defines your identity and says yes you are what you claim to be. just like that certificate defines your genuine identity.
While you are working with Azure AD and your app has Certificates then Azure checks against that Certificate what is registered. And let you access accordingly.
Encrypted Communication
Data sent between two systems can be encrypted by public key so only the intended receiver can read it.
Ensure data integrity
Each message and data are signed with a Public key, so whenever there is data altered then no sign matches and you can detect that it is data tempered.
Real world examples
Now, if you are working with Azure function and that function call secure API like sharepoint REST API or graph API.
Instead of giving a function a client secret (Passwords), you give it a Certificate where there is a public key which is safe and encrypts data.
So what happens when the Azure function runs.
It loads the certificate which we have provided as a thumbprint (Private key).
Use that to request Azure AD by signing.
Azure AD verifies that and checks with the public key which we have uploaded to app registration.
If it matches Azure AD issues a token and you can make an api call.
The benefits of this are
No hardcoded password needs to be provided.
Certificates can last longer than client secrets comparatively.
Stronger security because of private key.
Note:- if your are not able to sync in above real world examples, dont worry i will come up with another article which will be about connection with SharePoint via Azure function.
Conclusion
This article demonstrates that certificate based authentication is a better approach instead of client secret usage directly in function. This approach provides more security, validity as well as data encryption so if there is any kind of data alternation it direct notifies that data is tempered.So, we must use this certificate based authentication instead of client sacred which is risky.
Join the conversation! Your thoughts help the community grow.