
Introduction
Accessing Microsoft 365 data (SharePoint, Outlook, Teams, or OneDrive) through a client application involves securely authenticating to Microsoft Entra ID (Azure AD) and requesting tokens to call APIs like Microsoft Graph or SharePoint REST.
This article explains:
How Microsoft 365 authentication works
When to use delegated vs app-only permissions
When tokenization and app registration are required
How SPFx apps access Microsoft 365 without manual app registration
Authentication Models
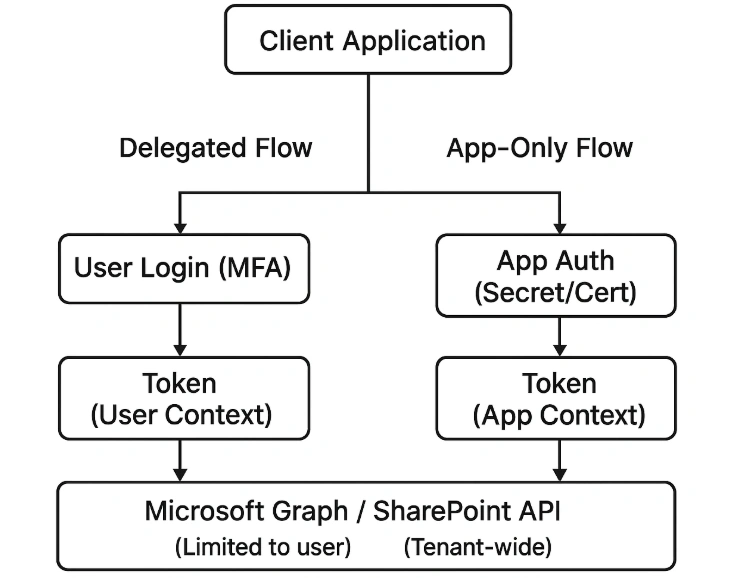
Before a client application can access Microsoft 365 services (like SharePoint, OneDrive, Teams, or Outlook), it must first authenticate. There are two main models of authentication for client applications:
1. Delegated (User) Authentication
Also called: On-behalf-of authentication.
Scenario: Your application acts on behalf of a signed-in user.
How it works:
The user signs in and grants consent to the app.
The app gets an access token for the user.
The app can only access resources that the signed-in user has permission for.
Use cases:
Web or mobile apps where a user interacts with Microsoft 365.
Accessing user emails, calendars, or OneDrive files.
Token Type: OAuth 2.0 access token with user context.
Example:
A SharePoint client app that reads the logged-in user’s documents in OneDrive.
2. Application (App-Only) Authentication
Also called: Client credentials flow
Scenario: The app acts as itself, without a signed-in user.
How it works:
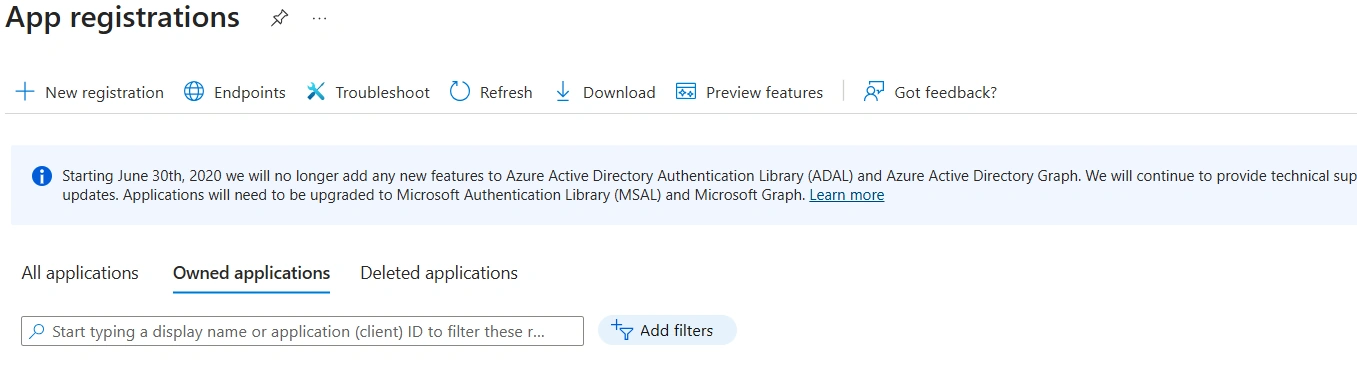
You register your application in Azure AD and assign it the required permissions.
The app uses its client ID and secret/certificate to authenticate and obtain an access token.
The app can access resources at the application level, independent of any user.
Use cases:
Automated workflows, background services, or daemons.
Accessing SharePoint sites, Teams data, or mailboxes for all users.
Token Type: OAuth 2.0 access token for app-only context.
Example:
A service that automatically archives emails from all user mailboxes in an organization.
When Do You Need Tokenization and App Registration?
You need App Registration and Tokens when
| Scenario | Reason |
|---|---|
| Client or Console App (Python, C#, Node.js) | You must register your app in Entra ID to get a Client ID and Secret/Certificate to authenticate. |
| Custom Web App connecting to Microsoft Graph | Web apps outside Microsoft 365 need tokens to prove identity and permissions. |
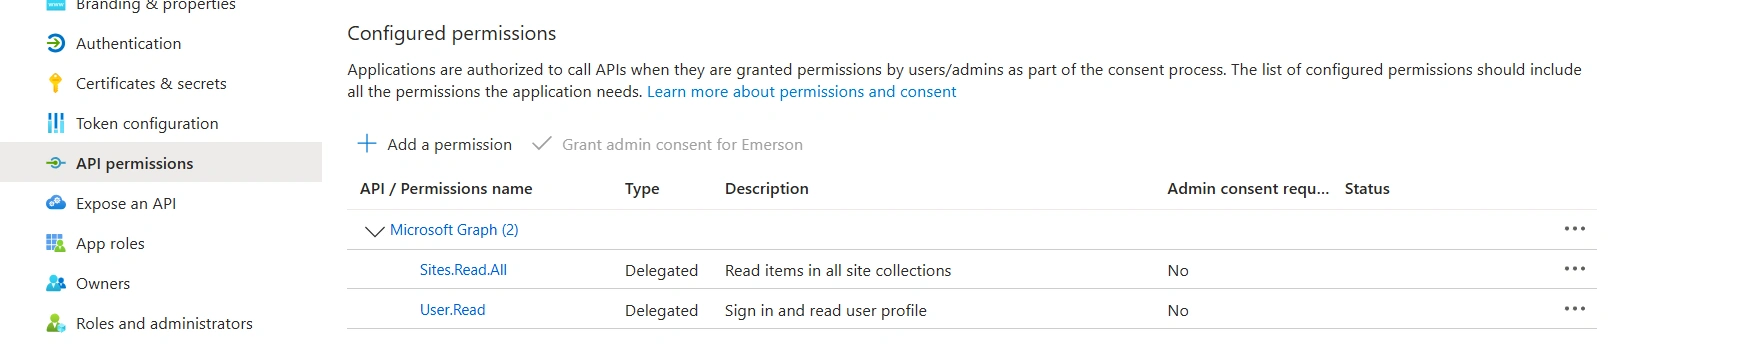
| Background/Migration Tools (App-Only) | Need tenant-wide access, require Sites.Read.All or Sites.FullControl.All. |
| Service Accounts replaced by Modern Auth | Token-based auth replaces legacy username-password. |
| PowerShell Graph scripts (using MSAL) | Each script authenticates via an app registration or managed identity. |
You do not need App Registration or Tokens when
| Scenario | Why |
|---|---|
| SPFx (SharePoint Framework) web parts or extensions | SPFx runs within the SharePoint security context, automatically using the user’s existing Azure AD session. |
| Graph calls made via MSGraphClient or AadHttpClient in SPFx | These clients use SharePoint’s pre-registered Azure AD application. No manual registration or secrets are needed. |
| Power Automate / Power Apps | Tokens are handled internally by Microsoft’s Power Platform identity layer. You simply grant permissions via connectors. |
| SharePoint Add-ins (legacy model) | Add-ins are registered in SharePoint directly and use the built-in OAuth trust (not Entra ID registration). |
Join the conversation! Your thoughts help the community grow.