
This is the “HTTP Message Handler in Web API” article series. In our previous two articles we learned the basic concepts of Message Handlers and the execution of HTTP custom Message Handlers. You can read them here.
- HTTP Message Handler in Web API: Implement Server-side Message Handler
- HTTP Message Handler in Web API: Execution Sequence of Custom Message Handler
HTTP Message Handler in Web API
In this article we will see a few real-time applications with a custom HTTP Message Handler. Though those examples are not full-fledge examples ready for a production server but they provide an idea of custom HTTP handlers.
As in the previous explanation we have learned that we can inject our custom Message Handler within a system Message Handler and we can form the handler chain. When a HTTP request arrives at the controller, it will pass through those custom handlers.
So, the custom handlers are a good place to perform some business logic and security implementation. For example there might be a condition in the Web API that only the HTTPS protocol can access the application. Let’s implement it in our custom Message Handler.
Allow only HTTP protocol to access the application
Step 1: Implementation of custom Message Handler
In this step we will implement a custom Message Handler that will filter the HTTP request. We have implemented a MessageHandler1 class derived from the DelegatingHandler class. Within that we are checking the HTTP type using a request object.
- public class MessageHandler1 : DelegatingHandler
- {
- protected async override Task<HttpResponseMessage> SendAsync(HttpRequestMessage request, CancellationToken cancellationToken)
- {
- if (!String.Equals(request.RequestUri.Scheme, "https", StringComparison.OrdinalIgnoreCase))
- {
- return await Task.Factory.StartNew(() =>
- {
- return new HttpResponseMessage(HttpStatusCode.BadRequest)
- {
- Content = new StringContent("HTTPS is Required to access the application")
- };
- });
- }
- return await base.SendAsync(request, cancellationToken);
- }
- }
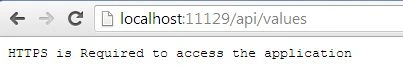
When the type is HTTP, we are creating one response message with response type “Bad Request”. In other words, we are not allowing the request to move towards a controller and within the custom Message Handler we are generating a response.
Step 2: Register the custom Message Handler
If it is necessary to register a custom Message Handler then we can inject our own Message Handler logic into a HTTP request and response pipeline.
- protected void Application_Start()
- {
- WebApiConfig.Register(GlobalConfiguration.Configuration);
- GlobalConfiguration.Configuration.MessageHandlers.Add(new MessageHandler1());
- }
Step 3: Implement sample controller
This is a small stub controller that we will call from a browser window. We have just modified the default values of the controller by adding a Get() action.
- public class ValuesController : ApiController
- {
- //api/Get
- public string[] Get()
- {
- return new string[] { "Sourav", "Kayal" };
- }
- }
Dipen VedPosted Jan 8, 2019, 3:13 AM
"Allow only HTTP protocol to access the application " is misleading. Should be https*. Nice and informative blog