
Introduction
In this article, we are going to look at other injection flaws. We are going to look at the different types of injections, how they affect the web applications, and how they can be countered. There are various kinds of injection flaws out there that serve different purposes.
Injection flaws are a group of attack vectors aimed at causing malfunction or compromise the primary purpose of any given web application or website. These attacks are implemented using user input to a system. Attackers make use of various tools to incapacitate an application, thereby disrupting the application’s purpose or getting unauthorized access to the application. An attacker may end up having access to confidential information or interrupting the integrity stored in an application’s database. Largely, this causes disrepute between the organization and its customers, resulting in great financial loss.
Types of Injection Flaws
In this article, we are going to look at the following types of Injection Flaws:
- SQL Injection
- Command Injection
- HTML Injection
- Code Injection
- XML Injection. All these are different types of attacks that attackers use to manipulate websites/web applications using input data.
SQL Injection
This is a form attack that attackers use with the help of SQL statements, i.e. they use input controls to supply SQL statements that may reveal sensitive information or delete sensitive information, thus negatively impacting the legit users of the system. It is also known as SQLi.
There are different types of SQL injections, including:
- In-band Injection (Classic)
- Error-based Injection
- Union-based Injection
- Inferential Injection (Blind)
- Boolean-based Injection
- Time-based Injection
- Out-of-band Injection
The three types of injection have a common implementation, which is the Structured Query Language. Attackers use this database language in input controls to gain unauthorized access to web applications, thus compromising their integrity and confidentiality.
Example
By supplying a query like this in the input field, an attacker may gain access to the database information and use it to manipulate other statements such as DROP TABLE, etc.
'OR '1'='1';Select @@version--'
After supplying this, an attacker will get knowledge about the database, as shown below:

SQL Injection is a common attack vector and normally attacks those applications with SQL statements that use a dynamic way of supplying their parameters.
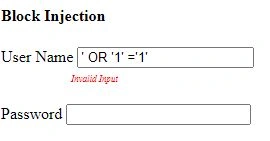
SQL Injection can be prevented by strongly validating input fields such that user input is filtered before it is submitted or by the use of online software tools that scan your web application for injection vulnerabilities. Other prevention techniques include using password encryption and managing the error messages revealed to users so that they only show that there has been an error, but the internal details are not revealed.
Example of validation:
Command Injection
Command Injection is when the attacker injects operating system commands on a user input field. The attacker may inject malicious commands to the host's operating system and get sensitive information from the webserver.
Command Injection attacks are common in languages such as Perl or PHP. These languages encourage programmers to reuse operating system binaries. Command Injection requires the attacker to manipulate script parameters that execute arbitrary system commands. These problems occur when scripts execute external commands using input parameters to construct command lines, but fail to filter the input data.
Example in PHP:
http://www.attacker.com/view_user.php?username=ivanr;cat%20/etc/pwd
It will display the contents of the PWD file on the server. This means that the attacker will have compromised the host operating system and he may proceed to start a Telnet server and log into the server as a user, try to gain root access, try to download and compile the source code of the application, and execute any binary on the server.
Another common Command injection attack is through the email sending in form-to-email scripts. These scripts are usually written in Perl. They accept data from an HTTP POST request and they construct the message and use sendmail.
# send email to the recpient
open(MAIL, "|/usr/lib/sendmail $email");
Join the conversation! Your thoughts help the community grow.