Introduction
Microsoft Entra ID (formerly Azure Active Directory) is Microsoft's cloud-based identity and access management service, helping organizations secure their applications and resources. It provides enterprise-grade authentication, single sign-on (SSO), and multi-factor authentication capabilities, making it an ideal choice for modern web applications.
Blazor Server is a powerful framework for building interactive web applications using C# instead of JavaScript. It runs on the server side with real-time communication to the browser via SignalR, offering a rich, interactive user experience while keeping your business logic secure on the server.
In this article, we'll see the complete process of integrating Microsoft Entra ID authentication into a Blazor Server application, enabling secure user login and logout functionality.
Prerequisites
• .NET 8.0 SDK or later
• Visual Studio 2022 or VS Code
• An Azure subscription with access to Microsoft Entra ID
• Basic knowledge of C# and Blazor
Integration
Step 1: Register an Application in Microsoft Entra ID
Before integrating authentication into your Blazor app, you need to register your application in Microsoft Entra ID:
1.1 Navigate to Azure Portal
Sign in with your Azure account
1.2 Register a New Application
Select App registrations from the left menu
Click + New registration
Fill in the registration form:
Name: Enter a descriptive name (e.g., "MS_EntraID_Blazor_Server")
Supported account types: Choose "Accounts in this organizational directory only" for single-tenant, or select the appropriate option for your use case
Redirect URI: Select "Web" and enter https://localhost:5224/signin-oidc.
Note: Adjust the port if different
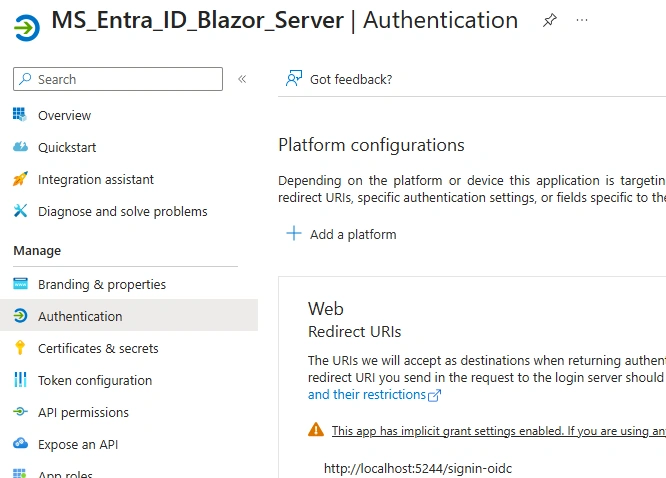
4.Click Register
1.3 Configure Authentication Settings
After registration, you'll be taken to the app overview page:
Note down the following values (you'll need them later):
Application (client) ID
Directory (tenant) ID
Step 2: Set Up Your Blazor Server Application
Now let's configure the Blazor Server application to use Microsoft Entra ID authentication.
2.1 Install Required NuGet Packages
Add the below Microsoft Identity Web packages to your project
Microsoft.Identity.Web
Microsoft.Identity.Web.UI
2.2 Configure Application Settings
Update your appsettings.json with the Azure AD configuration values from Step 1.3:
{
  "AzureAd": {
    "Instance": "https://login.microsoftonline.com/",
    "Domain": "yourdomain.onmicrosoft.com",
    "TenantId": "your-tenant-id",
    "ClientId": "your-client-id",
    "CallbackPath": "/signin-oidc"
  },
  "Logging": {
    "LogLevel": {
      "Default": "Information",
      "Microsoft.AspNetCore": "Warning"
    }
  },
  "AllowedHosts": "*"
}
Replace the placeholder values:
yourdomain.onmicrosoft.com - Your Azure AD domain
your-tenant-id - The Directory (tenant) ID
your-client-id - The Application (client) ID
2.3 Configure Program.cs
Update your Program.cs file to add authentication services and middleware:
using Microsoft.AspNetCore.Authentication.OpenIdConnect;
using Microsoft.Identity.Web;
using Microsoft.Identity.Web.UI;
using MS_EntraID_Blazor.Components;

var builder = WebApplication.CreateBuilder(args);

// Add authentication services with MS Entra ID
builder.Services.AddAuthentication(OpenIdConnectDefaults.AuthenticationScheme)
    .AddMicrosoftIdentityWebApp(builder.Configuration.GetSection("AzureAd"));

builder.Services.AddAuthorization();
builder.Services.AddRazorComponents()
    .AddInteractiveServerComponents();


builder.Services.AddControllersWithViews()
    .AddMicrosoftIdentityUI();


builder.Services.AddCascadingAuthenticationState();

var app = builder.Build();

if (!app.Environment.IsDevelopment())
{
    app.UseExceptionHandler("/Error", createScopeForErrors: true);
    app.UseHsts();
}
app.UseHttpsRedirection();
app.UseStaticFiles();
app.UseAntiforgery();
app.UseAuthentication();
app.UseAuthorization();
app.MapControllers();

app.MapRazorComponents<App>()
    .AddInteractiveServerRenderMode();

app.Run();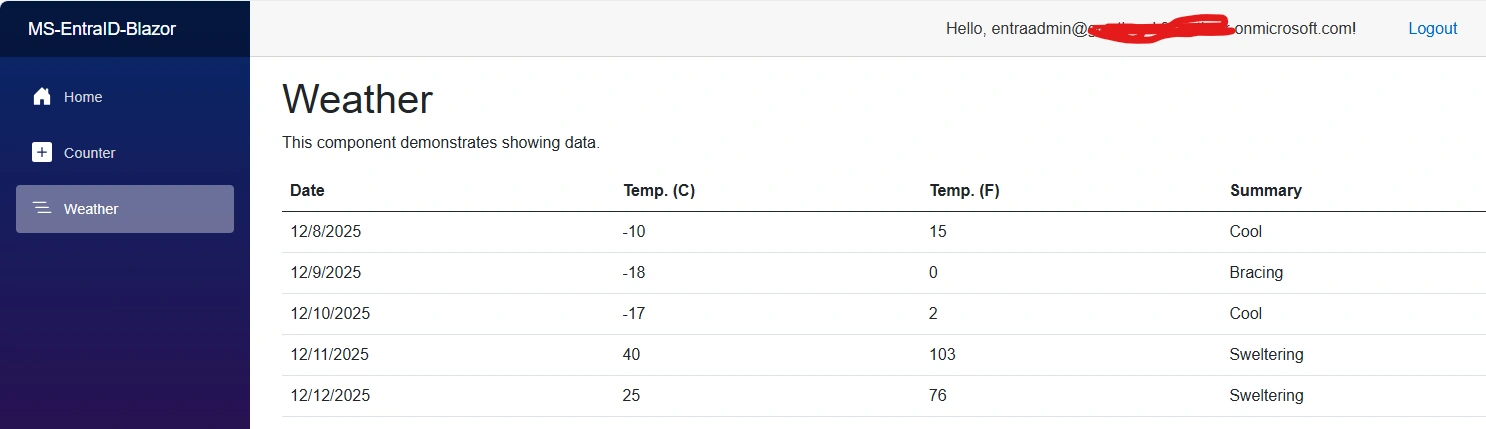
Join the conversation! Your thoughts help the community grow.