
Image Courtesy: Medium
JSON Web Tokens (JWTs) Explained: A Complete Guide with Corporate Office Analogy
Ever wondered how JSON Web Tokens (JWTs) work in modern web security? Imagine walking into a bustling corporate office, complete with receptionists, visitor badges, and security guards. This simple analogy helps break down JWTs step-by-step—from authentication to authorization, with a real-world use case, pros and cons, and alternatives—so you can decide if JWT is right for your web application.
Let’s step into the corporate headquarters and explore how JWTs secure the digital world!
The Corporate Office Analogy: Understanding JWTs
Picture yourself arriving at the headquarters of a large corporation. Only authorized people can access certain floors or rooms. This is exactly how JWTs function in web applications.
1. Authentication: Proving Who You Are
You walk into the lobby and approach the receptionist (the server).
- Receptionist: “Who are you?”
- You: Show your ID (username and password).
- Receptionist: Verifies your credentials against the database.
Authentication = confirming your identity. Once verified, you can move to the next step.
2. Authorization: Deciding What You Can Access
- Receptionist: “Which department are you visiting?”
- You: “Marketing, 7th floor.”
- Receptionist: Checks access rules:
- Allowed: Marketing floor
- Not allowed: IT server room
Authorization = determining what resources or areas you can access based on your role.
3. JWT Issued: Your Digital Visitor Badge
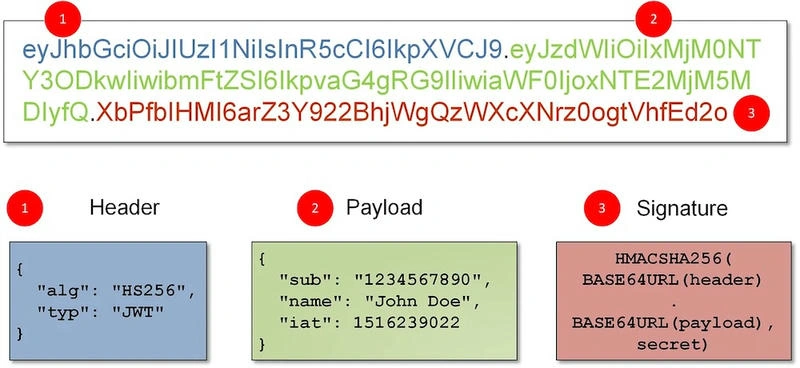
Once authenticated and authorized, the receptionist gives you a visitor badge (JWT). This badge has three key parts:
- Header: Identifies it as a JWT and specifies the algorithm (e.g., HMAC-SHA256).
- Payload: Contains your details:
- Name (user ID)
- Permissions (allowed floors)
- Expiry time
- Signature: A secure stamp ensuring the badge can’t be forged.
The JWT is encoded as a compact, URL-safe string: header.payload.signature, making it easy to pass around.
4. Stateless Access: No Repeated Verification
At the elevator, the security guard scans your badge. The badge already contains your permissions, so there’s no need to verify your identity with the receptionist every time.
- Stateless Authentication: JWTs are self-contained, allowing servers to handle requests without querying the database every time.
- Expiry: When the badge expires, you need a new JWT (via a refresh token), enhancing security.
5. Security Risks: Handle JWTs Carefully
A lost badge can be misused. Similarly, stolen JWTs (e.g., via MITM attacks) pose risks. Mitigate risks by:
- Storing JWTs securely (HTTP-only, secure cookies)
- Using HTTPS for encryption
- Setting short expiry times with refresh tokens
Real-World Example: JWT in a Corporate Web App
Imagine a corporate project management tool like Trello or Asana. Employees log in to access projects and sensitive data.
Scenario: Secure API Access with JWT
- User Login
- Employee logs in with username/password (
jane.doe,securePass123). - Server verifies credentials and issues a JWT.
- Employee logs in with username/password (
- JWT Structure
Header:
{
  "alg": "HS256",
  "typ": "JWT"
}

Payload:
{
  "sub": "jane.doe",
  "role": "manager",
  "exp": 1697043600
}

Signature:
Created using server secret key
Example JWT:
eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJzdWIiOiJqYW5lLmRvZSIsInJvbGUiOiJtYW5hZ2VyIiwiZXhwIjoxNjk3MDQzNjAwfQ.Signature - API Requests
- Client sends JWT in
Authorization: Bearer <JWT>header. - Server validates signature and expiry, granting access if valid.
- Client sends JWT in
- Stateless Operation
- Server doesn’t query the database for every request.
- Token contains all necessary user info and permissions.
- Token Expiry & Refresh
- JWT expires after 1 hour.
- Refresh token issues a new JWT without re-entering credentials.
- Security Measures
- HTTPS to prevent interception
- HTTP-only cookies to prevent XSS
- Short-lived tokens with refresh options
Benefits
- Scalable and stateless
- Cross-platform usage
- Granular role-based access control
Pros & Cons of JWT
Pros
- Stateless & Scalable: No server-side session storage needed
- Cross-Domain Compatible: Ideal for microservices or SSO
- Compact & Self-Contained: Easy to transmit
- Flexible Payload: Add custom claims like roles
- Wide Adoption: Supported in Node.js, Django, Spring, and more
Cons
- Security Risk: Stolen JWTs can be misused
- No Built-In Revocation: Blacklists reduce stateless benefits
- Large Token Size: Many claims can bloat requests
- Implementation Complexity: Proper handling of refresh tokens and signatures is critical
- Not Always Necessary: Simple apps may not need JWTs
Alternatives to JWT
- Session-Based Authentication
- Stores session data server-side
- Easy revocation but limited scalability
- OAuth 2.0 Access Tokens
- Delegated access supports refresh tokens
- Complex setup, needs an authorization server
- Opaque Tokens
- Random string mapped to server data
- Easier revocation, less flexible for APIs
- SAML
- XML-based, robust for enterprise SSO
- Heavyweight for modern REST APIs
Best Practices for JWT
- Always use HTTPS
- Set short expiry times (15 min–1 hour)
- Store in HTTP-only, secure cookies
- Validate signatures
- Avoid sensitive data in the payload
- Implement refresh tokens
- Use strong signing keys (HS256, RS256)
Why JWTs Are Perfect for Modern Web Development
JWTs are like digital visitor badges: compact, secure, and versatile. They excel in:
- Microservices
- Mobile & web apps
- Single-page applications (SPAs)
By encoding user data and permissions in one token, JWTs simplify access control while improving scalability and efficiency.
For simple apps or frequent token revocation scenarios, consider sessions or opaque tokens instead.
Get Started with JWTs Today
- Choose a Library:
jsonwebtokenfor Node.js,PyJWTfor Python, etc. - Set Up Authentication: Endpoints for login and token issuance
- Secure Tokens: Follow storage, expiry, and validation best practices
- Test Thoroughly: Simulate token theft or expiration
Join the conversation! Your thoughts help the community grow.