
Introduction
Granting access to SharePoint online can be done in different ways. We can grant the following access.
- User access
- Service account access
- App access
User Access is something that we already know, where site owners grant access to the users of the sites to access the content within the SPO site.
Service account access is giving a service account. Usually, the service account is used by backend jobs to monitor the site or to perform specific tasks such as adding or modifying content, adding or deleting users, etc.
App Access: If a third-party app / Provider-hosted app wants to get access to the SPO site, they can currently do it by registering the Application registration and then configuring the Service Principal (SPN) access to the site.
The article comprises three sections.
- Creating App Registration
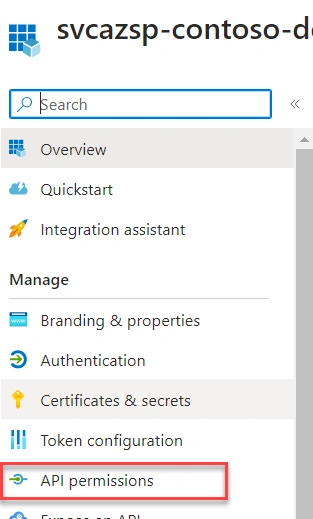
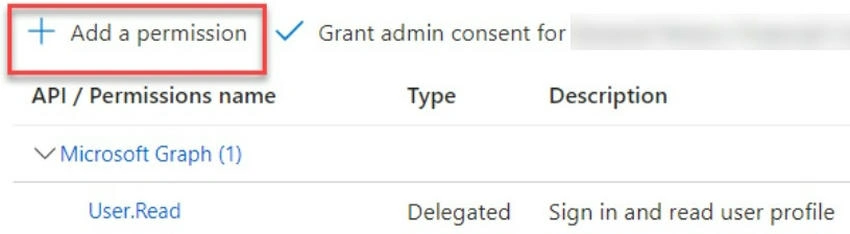
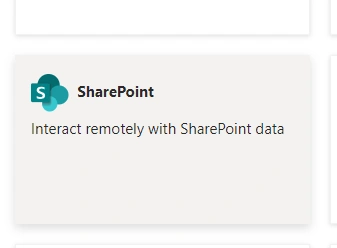
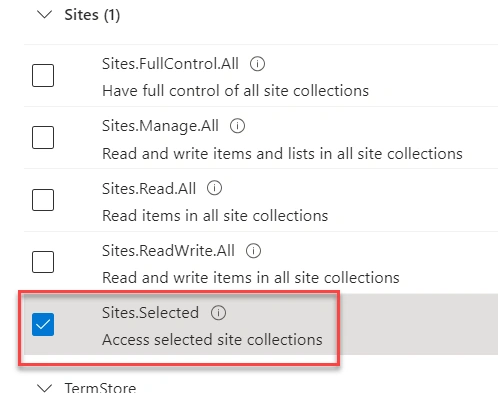
- Granting API Access
- Configuring the Permissions
Legacy authentication is required for the Apps that are still using Client credentials flow (Client ID and Client Secret for authentication).
Before the App registration existed, for granting access to SharePoint online sites using Windows Azure Access Control Services, we were using /_layouts/15/appregnew.aspx. This AppRegNew.aspx creates the Enterprise App with Client Id and secret and Application Name. The Application registration done this way will have access only to that site. The same client credentials cannot be used for different site collections. For different sites, other client credentials need to be created.
The use case here is to create an App Registration and use it for different site collections.
Note. Azure Access Control Services (ACS) acts as a trusted token provider for SharePoint provider-hosted apps and remote components in an OAuth2.0 Authorization flow. Starting November 27th, 2023, the Azure ACS for SharePoint online has been deprecated, and it will stop working after 04/02/2026. It is better to look for modern authentication using OAuth2.0 that supports certificate-based authentication.
Before going to the next steps, check whether your M365 tenant supports legacy authentication. Work with SharePoint Admin or Global Admin to check if custom app authentication is enabled.
get-potent -DisableCustomAppAuthentication
If the value is set to $false, then the custom app authentication is allowed, which will support the Client Credentials flow. If the value is set to $true, then the custom app authentication is disabled, which means that the client credentials flow will no longer work.
Creating App Registration
For this step, it is required to follow the below steps to create an app. As a pre-requisite, you should have access to Azure Portal and either a privileged admin role or a global admin role to grant the admin consent.
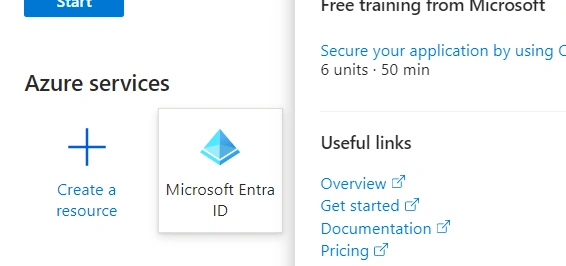
Step 1. Log in to the Azure portal. https://portal.azure.com using the organization account. Click on 'Microsoft Entra' on the home page. If you cannot find you can also search for Entra.

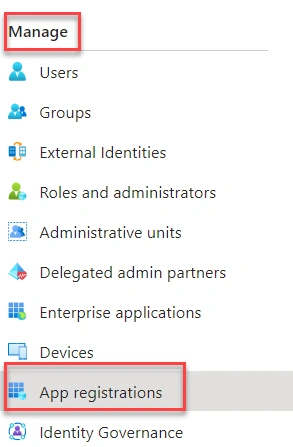
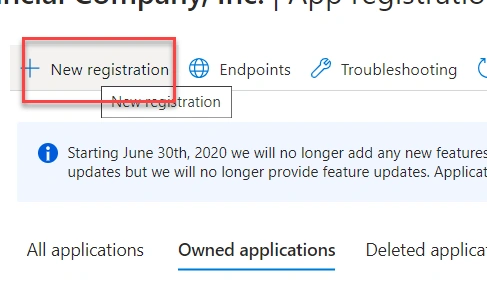
Step 2. From the Entra page, under the 'Manage' section, click on 'App Registration' and then click on 'New Registration'.
Step 3. On the new registration page, give some names. Here, I have given as svcazsp-contoso-dev-access. Leave the rest of the options as default. We are configuring this app only for the existing tenant.
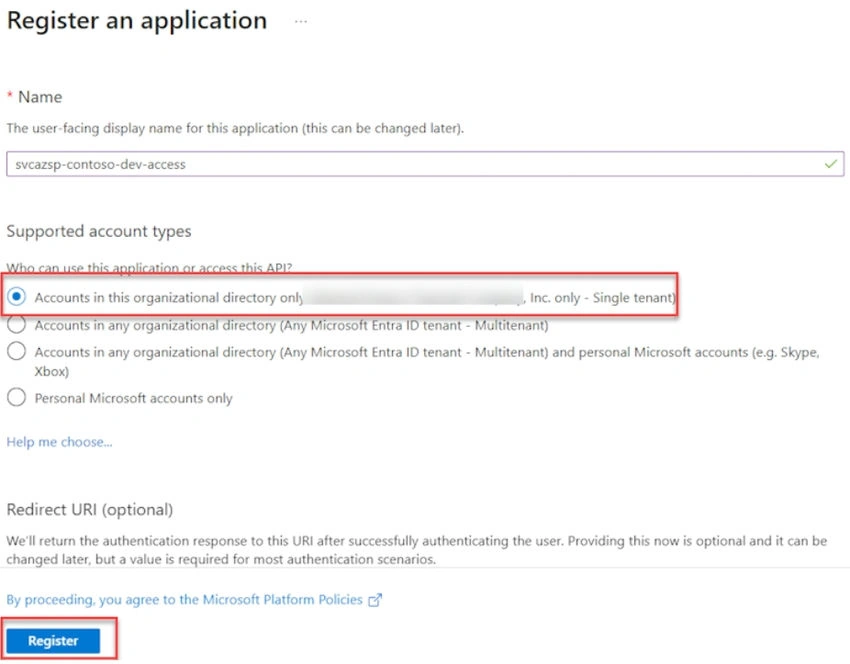
Step 4. Once the App Registration is successfully completed, it will navigate to the app home page, where you can see the
The above steps conclude with creating the App registration.
Configuring Client Credentials
In this section, we will configure client credentials.
Step 1. Click on 'Certificates and Secrets' --> New Client Secret.
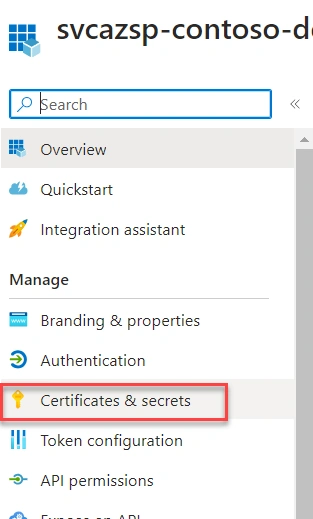
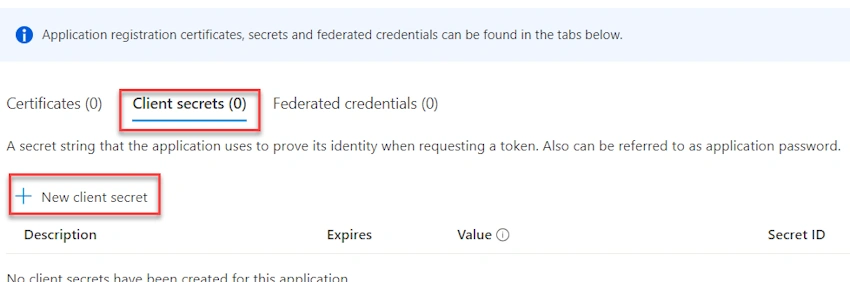
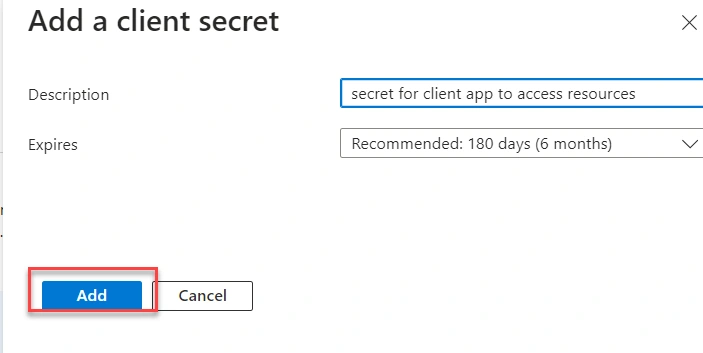
Step 2. Enter the description. In this case, I have chosen the expiry default, which is six months, and it can be extended up to 2 years.



Join the conversation! Your thoughts help the community grow.