
Introduction
In today’s dynamic digital landscape, securing sensitive data and actions within applications is more critical than ever. Microsoft Entra’s Conditional Access offers a robust framework for implementing Zero Trust principles, and one of its standout features Authentication Contexts takes security to the next level by enabling precise, context-aware access controls. This article dives into how authentication contexts work, their unique benefits, and practical steps to leverage them for enhanced security, tailored for organizations looking to balance user experience with stringent access policies.
What Makes Authentication Contexts Unique?
Authentication contexts in Microsoft Entra allow administrators to tag specific resources, data, or actions within an application with customized Conditional Access policies. Unlike broad, application-level policies, authentication contexts provide surgical precision, applying rules only to high-sensitivity tasks or data. For instance, imagine a Microsoft Teams environment where general chats require standard access, but accessing a channel with proprietary project files demands multi factor authentication (MFA) and a compliant device. Authentication contexts make this level of granularity possible.
These contexts are defined in the Microsoft Entra admin center as identifiers (c1 to c99), each with a name and description, and can be integrated with Microsoft 365 services like SharePoint or custom applications via OpenID Connect. This flexibility empowers organizations to secure specific operations without overcomplicating access to less sensitive areas.
Why Authentication Contexts Matter
Authentication contexts address the challenge of balancing security with usability. Here’s why they’re a game-changer:
- Precision Security: Apply strict controls only where needed, reducing unnecessary friction for users accessing low risk resources.
- Dynamic Protection: Combine with signals like user risk, device state, or location to enforce adaptive policies that respond to real time conditions.
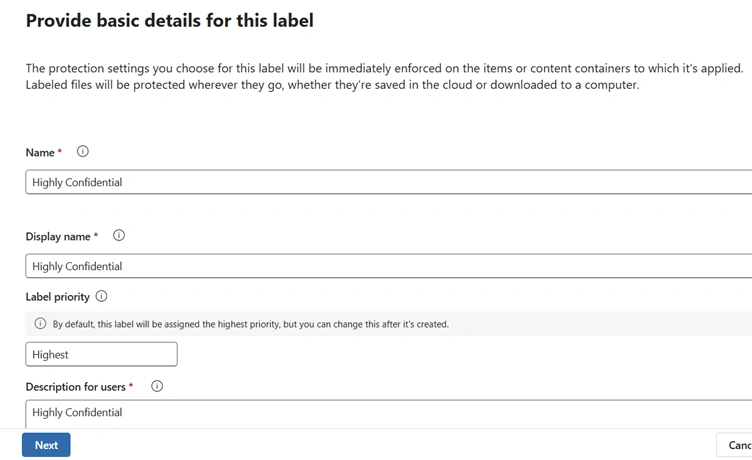
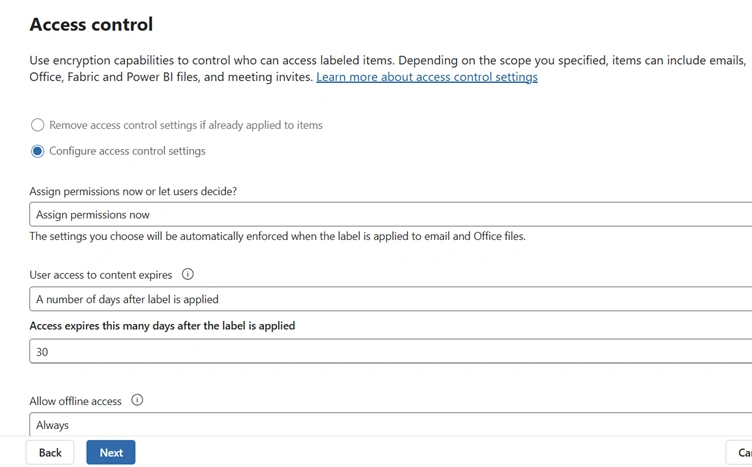
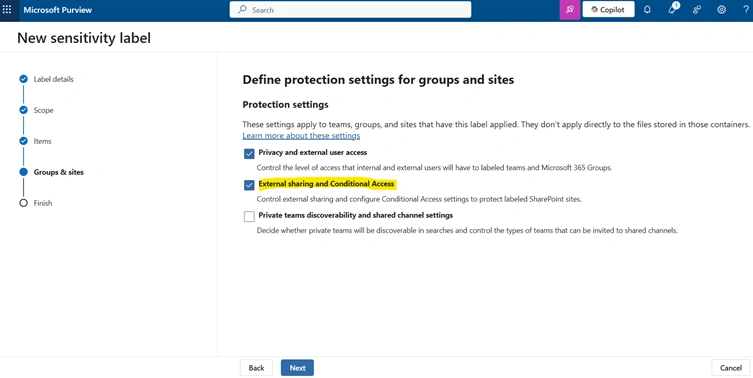
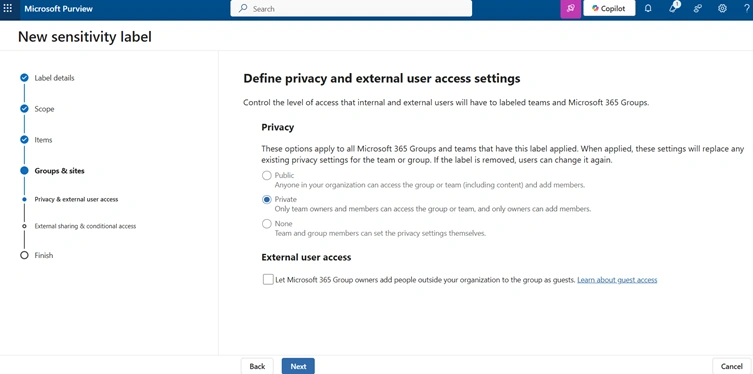
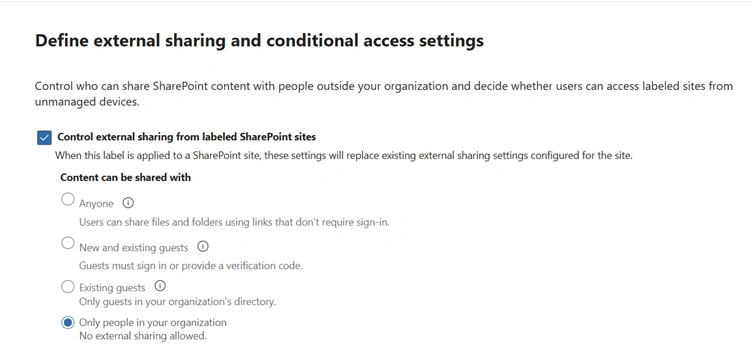
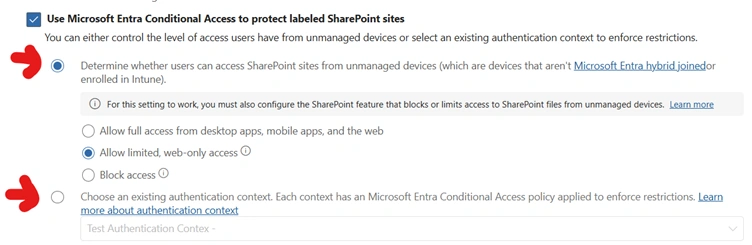
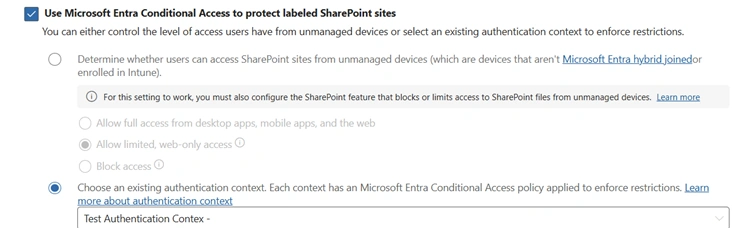
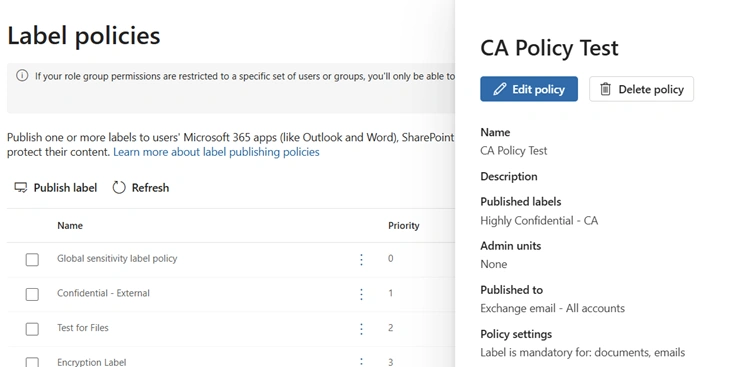
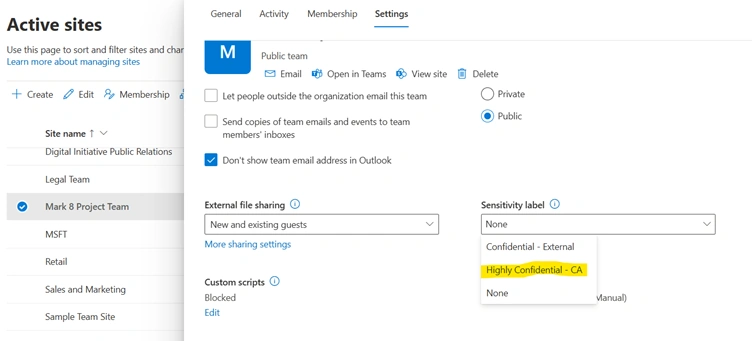
- Seamless Integration: Work hand in hand with Microsoft Information Protection sensitivity labels to automatically enforce policies on labelled content in SharePoint, Teams, or Microsoft 365 groups.
- Custom App Support: Enable developers to embed step up authentication in custom apps, ideal for high-value transactions like financial approvals or data exports.
- Scalability: With up to 99 contexts, organizations can create reusable, modular policies for diverse use cases across their ecosystem.
How to implement Authentication Contexts and Policies?
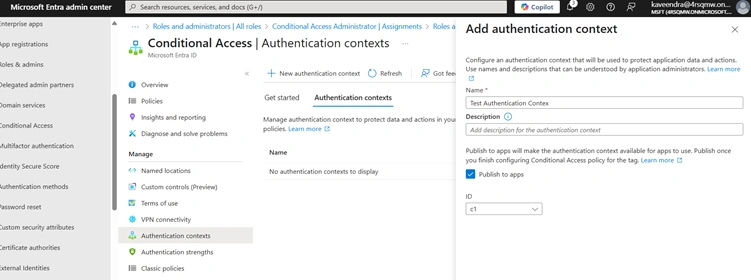
Login to Entra Admin Center --> Conditional Access --> Authentication context
Click New authentication context, name it (e.g., “Secure Financial Reports”), add a description, and ensure Publish to apps is checked. Note the assigned ID (e.g., c1)
Create a Conditional Access Policy
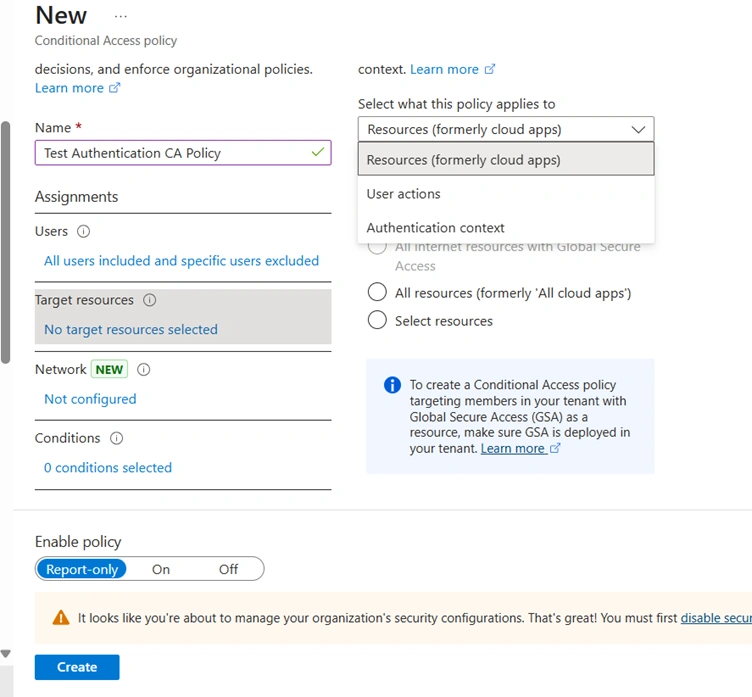
- Go to Conditional Access > Policies and select New policy.
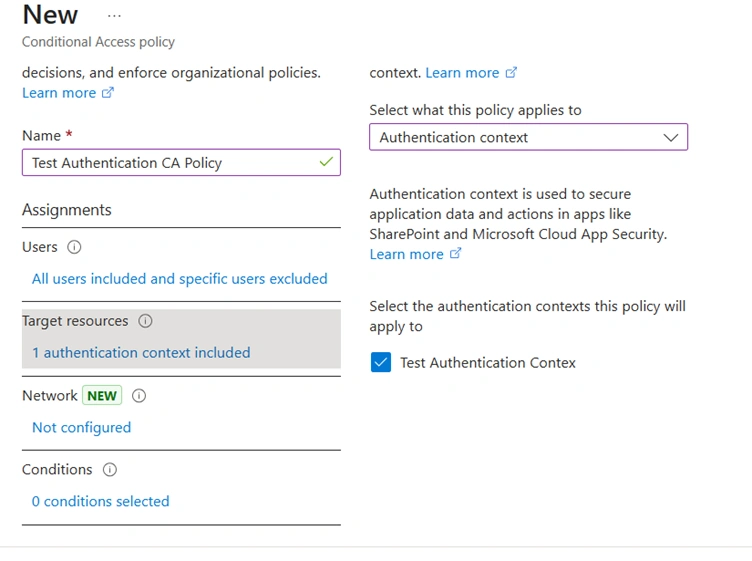
- Under Assignments > Target resources, choose Authentication context and select the context from Step 1.
- Configure the policy:
- Users: Apply to specific groups or all users, excluding emergency accounts.
- Conditions: Require MFA and compliant devices; optionally, restrict to trusted locations.
- Access Controls: Set to Block or Grant with conditions as needed.
- Enable the policy in Report-only mode initially to test its impact.
Join the conversation! Your thoughts help the community grow.