
In enterprise AI, securing the perimeter is only half the battle. Once a request passes the gateway, the backend must strictly enforce Authorization (what is this user allowed to do/see?) based on the Validation (is this token genuine and unexpired?) of the JWT.
In a serverless architecture (AWS Lambda + API Gateway), doing both efficiently is critical for cost, latency, and security. Furthermore, when orchestrating a Multi-Agent LangGraph RAG system, JWT claims must be deeply integrated into the graph's state to enforce data isolation at the retrieval level.
This article provides an end-to-end guide to implementing JWT validation and authorization in a serverless backend, applied to a highly regulated enterprise RAG use case.
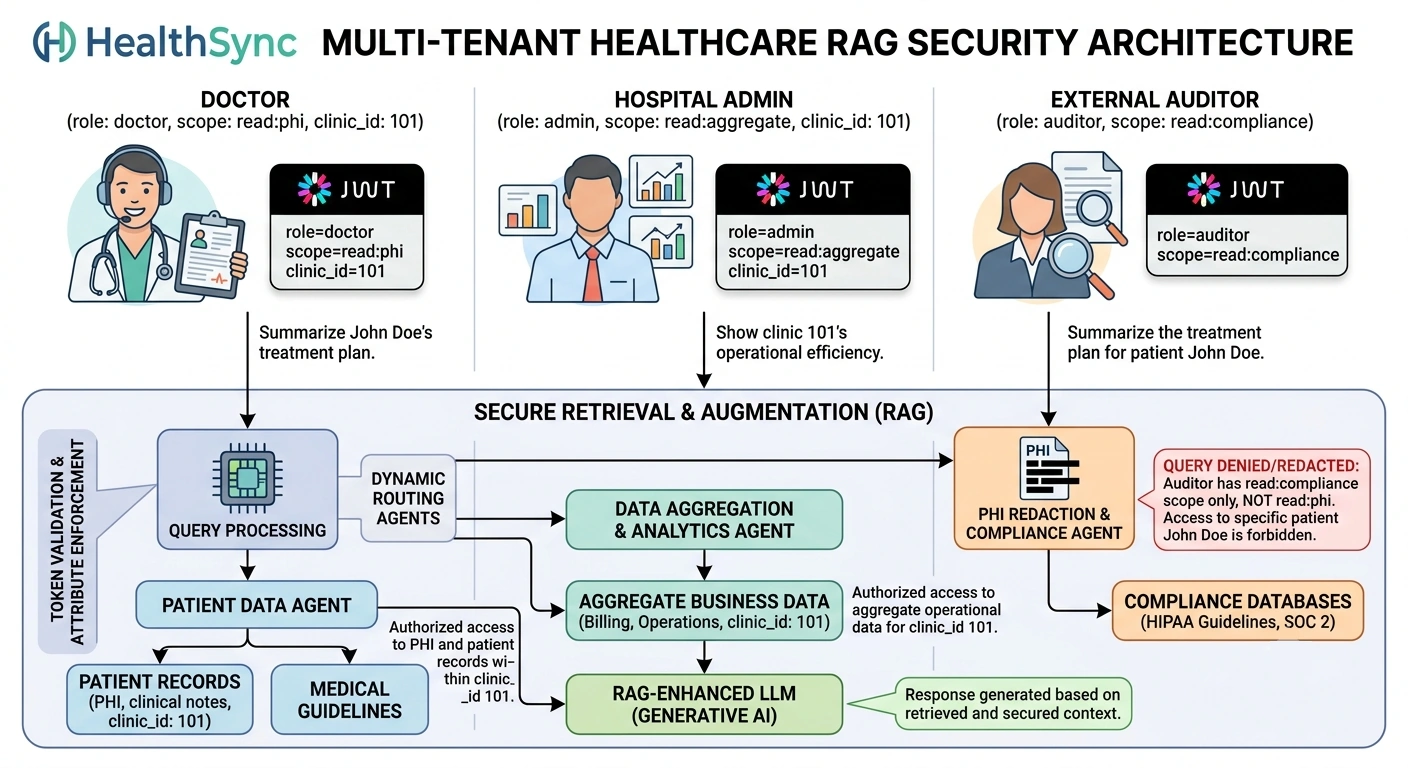
1. Real-Time Use Case: "HealthSync" Multi-Tenant Healthcare RAG
The Scenario: A SaaS provider hosts a medical analytics RAG platform for multiple hospital networks.
The Actors & JWT Claims:
Doctors (
role: doctor): Can query patient records and medical guidelines only for their assignedclinic_id. Scope:read:phi(Protected Health Information).Hospital Admins (
role: admin): Can query aggregate billing and operational data for theirclinic_id. Scope:read:aggregate.External Auditors (
role: auditor): Can query compliance guidelines but are strictly forbidden from seeing any PHI. Scope:read:compliance.
The Challenge: If an Auditor asks, "Summarize the treatment plan for patient John Doe," the system must not just refuse; it must dynamically route the query through a compliance agent that redacts PHI, or deny it entirely based on the JWT scopes.
2. High-Level Serverless Architecture
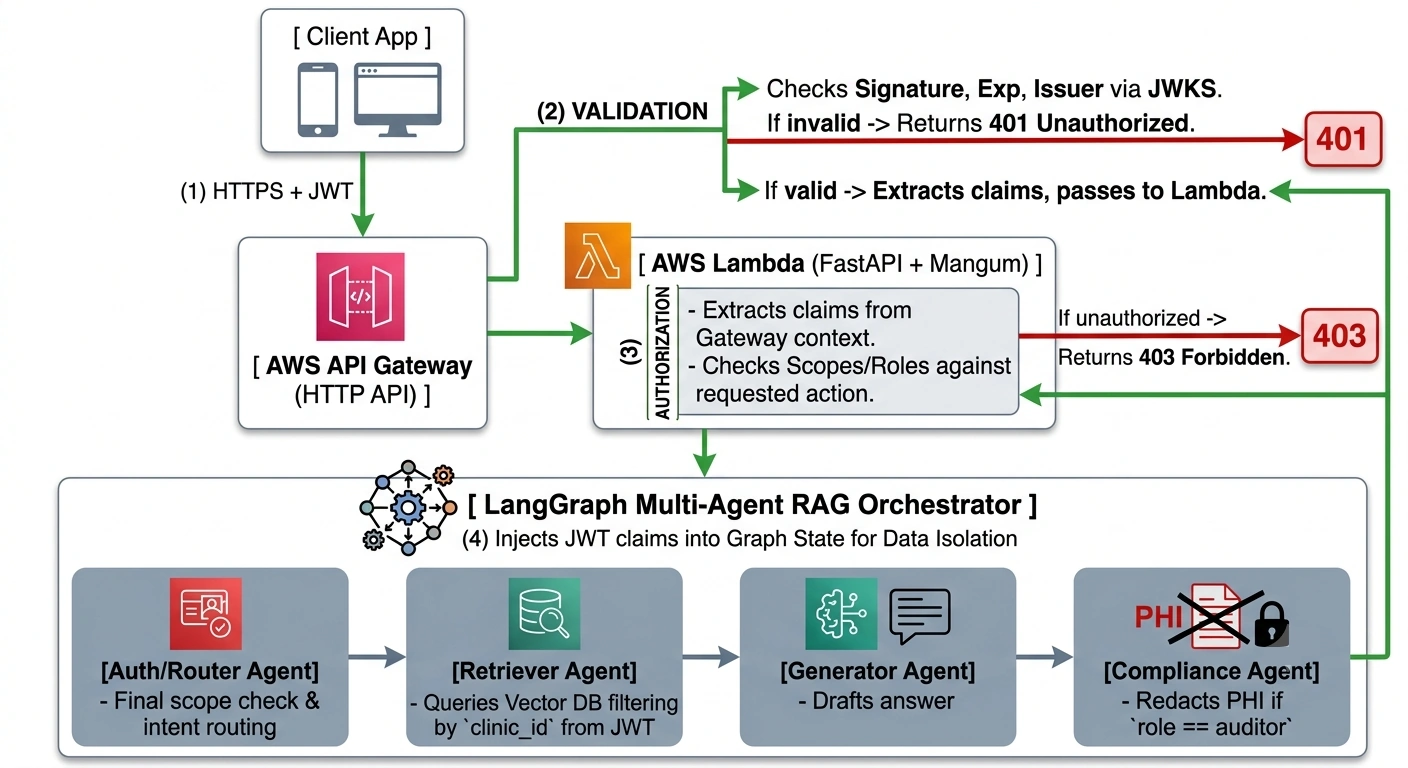
In a serverless paradigm, we split Validation and Authorization to optimize for cold starts and compute costs.
3. Phase 1: Serverless JWT Validation (API Gateway)
Architectural Rule: Never validate JWT signatures in AWS Lambda if API Gateway can do it. Signature verification (RSA/ECDSA) is CPU-intensive and will increase your Lambda execution time and cost.
Configure API Gateway Authorizer: Create a JWT Authorizer in API Gateway. Provide your Identity Provider's (IdP) JWKS (JSON Web Key Set) URI (e.g., Auth0, Cognito, Okta).
Define Claims: Map the required claims (e.g.,
role,clinic_id,scope).Attach to Route: Attach this authorizer to your
/queryPOST route.
Result: API Gateway now handles Validation. By the time the request hits your Lambda, the JWT is guaranteed to be cryptographically valid and unexpired.
4. Phase 2: Designing the Multi-Agent LangGraph RAG
We will build a LangGraph where the JWT claims dictate the flow.
Step 1: Define the Graph State and Agents
# graph_agents.py
from typing import TypedDict, Sequence, List, Literal, Any
from langchain_core.messages import BaseMessage, HumanMessage, AIMessage
from langchain_openai import ChatOpenAI
from langchain_core.prompts import ChatPromptTemplate
from langgraph.graph import StateGraph, END
import re

# 1. Define the State (Notice the jwt_claims)
class AgentState(TypedDict):
    messages: Sequence[BaseMessage]
    jwt_claims: dict       # Contains sub, role, clinic_id, scope
    documents: List[str]
    next_step: str
    is_authorized: bool

llm = ChatOpenAI(model="gpt-4o", temperature=0)

# 2. Define the Nodes (Agents)

def auth_router_agent(state: AgentState):
    """Checks JWT scopes against the user's intent."""
    claims = state["jwt_claims"]
    query = state["messages"][0].content.lower()

    # Simple intent-to-scope mapping
    requires_phi = any(word in query for word in ["patient", "john doe", "medical record", "treatment"])

    user_scope = claims.get("scope", "")

    if requires_phi and "read:phi" not in user_scope:
        return {
            "messages": [AIMessage(content="Access Denied: Your role does not permit viewing Protected Health Information (PHI).")],
            "is_authorized": False,
            "next_step": "end"
        }

    return {"is_authorized": True, "next_step": "retrieve"}

def retriever_agent(state: AgentState):
    """Retrieves data. CRITICAL: Enforces multi-tenancy using JWT claims."""
    claims = state["jwt_claims"]
    clinic_id = claims.get("clinic_id")
    query = state["messages"][0].content

    # In production, this is passed to the Vector DB (e.g., Pinecone/Weaviate)
    # metadata_filter = {"clinic_id": clinic_id}
    # docs = vector_db.similarity_search(query, filter=metadata_filter)

    # Simulated retrieval based on tenant
    mock_docs = [
        f"Guideline 4A for Clinic {clinic_id}: Standard protocol for patient intake.",
        f"Billing code 99213 applied for Clinic {clinic_id} visits."
    ]
    return {"documents": mock_docs, "next_step": "generate"}

def generator_agent(state: AgentState):
    """Generates the initial response."""
    docs = "\n".join(state["documents"])
    query = state["messages"][0].content

    prompt = ChatPromptTemplate.from_template(
        "Context:\n{context}\n\nQuestion: {query}\n\nProvide a professional medical response."
    )
    chain = prompt | llm
    response = chain.invoke({"context": docs, "query": query})

    return {"messages": [AIMessage(content=response.content)], "next_step": "compliance"}

def compliance_agent(state: AgentState):
    """Redacts PHI if the user is an Auditor, otherwise passes through."""
    claims = state["jwt_claims"]
    role = claims.get("role")
    last_message = state["messages"][-1].content

    if role == "auditor":
        # Simulated PHI Redaction (In prod, use Presidio or a dedicated NER model)
        redacted_text = re.sub(r'\b(?:John Doe|Patient ID \d+)\b', '[REDACTED PHI]', last_message)
        return {"messages": [AIMessage(content=redacted_text)], "next_step": "end"}

    return {"next_step": "end"}

# 3. Build the Graph
def create_healthsync_graph():
    workflow = StateGraph(AgentState)

    workflow.add_node("auth_router", auth_router_agent)
    workflow.add_node("retrieve", retriever_agent)
    workflow.add_node("generate", generator_agent)
    workflow.add_node("compliance", compliance_agent)

    workflow.set_entry_point("auth_router")

    workflow.add_conditional_edges(
        "auth_router",
        lambda x: x["next_step"],
        {"retrieve": "retrieve", "end": END}
    )
    workflow.add_edge("retrieve", "generate")
    workflow.add_edge("generate", "compliance")
    workflow.add_edge("compliance", END)

    return workflow.compile()

rag_graph = create_healthsync_graph()
Join the conversation! Your thoughts help the community grow.