
In the world of containers and microservices, security is like a trusted co-pilot: you hope it’s doing its job quietly in the background so you can focus on flying the plane. Yet every container image can hide sneaky vulnerabilities – out-of-date libraries or security holes – that might crash your flight if left unchecked. That’s where Docker Scout comes in. Think of Docker Scout as an extra-diligent mechanic or a metal detector for your Docker images. It automatically inspects the “ingredients” of your containers (the OS packages, programming libraries, and other bits inside the image), builds a Software Bill of Materials (SBOM), and matches it against a constantly updated vulnerability database. In other words, it scans your Docker images for known security issues and tells you how to fix them.
As a developer or DevOps engineer, you might remember scanning images with tools like Trivy or Snyk. Docker Scout is Docker’s built-in solution for this task, tightly integrated into the Docker ecosystem. It works inside Docker Desktop (starting from version 4.17), the Docker CLI, and even Docker Hub. It not only finds vulnerabilities but also suggests fixes or safer base images to use. In this article, I’ll take you through Docker Scout in a friendly, hands-on way – from why scanning matters to how to use Scout, plus tips and comparisons with Trivy and Snyk. I’ll share a few stories and analogies too, so even if you’re new to container security, you’ll get it.
Why Container Image Scanning Matters
Before diving into Docker Scout, let’s talk about why we need these tools. Imagine you bake a cake using a recipe. If the recipe is old or incomplete, you might accidentally use a spoiled ingredient – yuck! Similarly, Docker images are built from layers of software “ingredients” (libraries, packages, system tools) maintained by others. If any of those ingredients have known vulnerabilities (like an expired carton of eggs), attackers could exploit them.
I remember a time when my team shipped an application container, only to find out later that one of the base images (Ubuntu 18.04) had dozens of unpatched CVEs. We spent a frantic weekend patching dependencies and redeploying. It felt like performing a last-minute check of the oil, brakes, and seatbelts after the plane had already taken off! Clearly, we needed a scanner to catch these issues before production.
Tools like Docker Scout automatically analyze container images to prevent exactly that. They generate an SBOM – basically a detailed ingredients list of your image – and compare it to vulnerability feeds (from the likes of Debian, RedHat, Python, etc.). If any listed component is known to be dangerous, Scout flags it for you. It’s a proactive check-up, so you’re less likely to push an image that’s a ticking time bomb.
Scout “aggregates real-time vulnerability data from multiple sources” and keeps the information “up-to-date with the latest insights”. This means Scout is continuously learning about new CVEs (Common Vulnerabilities and Exposures) as they are discovered, rather than relying on an outdated snapshot. In practice, that’s like having a guard dog that not only sniffs around your code once but keeps smelling the air every moment for new trouble.
Docker Scout: A Friendly Introduction
So, what exactly is Docker Scout? In simple terms, Docker Scout is Docker’s built-in image analysis and scanning tool, part of Docker Desktop and Docker Hub, as well as available via the Docker Scout CLI plugin. It goes through your Docker image’s contents, builds the SBOM (imagine writing down every software component in the image), and then checks each one against a continuously updated advisory database.
An official Docker docs description says.
Note. Docker Scout is a solution for proactively enhancing your software supply chain security. By analyzing your images, Docker Scout compiles an inventory of components, also known as a Software Bill of Materials (SBOM). The SBOM is matched against a continuously updated vulnerability database to pinpoint security weaknesses.
In other words, Scout is your image’s personal detective and doctor rolled into one. It spots the “bad ingredients” and even suggests remedies.
A useful analogy: think of SBOM as a detailed recipe card listing all the ingredients (and their versions) that went into making your container image. Just like you wouldn’t want to eat a dish if you’re allergic to one of its ingredients, Scout makes sure you’re not “eating” (deploying) any vulnerable software. Docker Scout even integrates seamlessly with Docker Desktop – you can use the Docker Dashboard GUI or just run docker scout commands in the terminal, whichever you prefer.
Another key point: Docker Scout was introduced as an upgrade to the older “docker scan”. (You might recall that Docker previously partnered with Snyk to provide a docker scan command.) The Earthly blog puts it this way: “If you’re familiar with Docker Scan, consider Docker Scout as an upgrade that offers a more comprehensive approach to Docker image analysis”. Unlike docker scan, Docker Scout is integrated into Docker Desktop’s UI and into Docker Hub, providing reports and recommendations right there. You could even say Scout is like the next-generation replacement for Docker Scan – more features, better integration, and continuous updates.
Key Features of Docker Scout
Let’s break down Docker Scout’s core features and benefits in everyday terms.
- Automatic SBOM Generation: When you scan an image with Scout, it extracts the software bill of materials (SBOM) for that image. Think of this as writing down a full list of every piece of software and library in your container. This SBOM is then stored (in your Docker organization’s Scout database) so Scout knows exactly what’s inside your image.
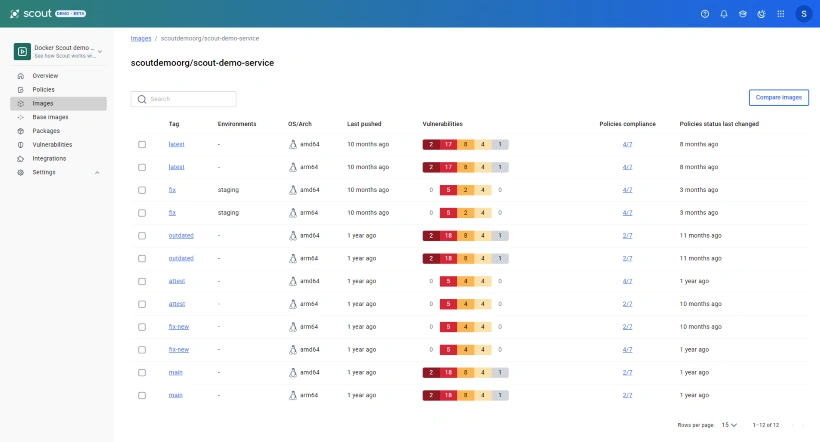
- Vulnerability Database Matching (in Real-Time): Docker Scout doesn’t rely on stale lists. It continuously aggregates vulnerability data from over 20 different trusted sources (like Debian, Ubuntu, RedHat, GitHub Advisory DB, Python Packaging DB, and more). This means as soon as a new CVE is published, Scout’s database knows about it. When Scout scans your SBOM, it cross-references those CVEs and immediately alerts you if any component in your image is affected. It’s like having a constantly updated dictionary of known security flaws that get checked against your recipe.
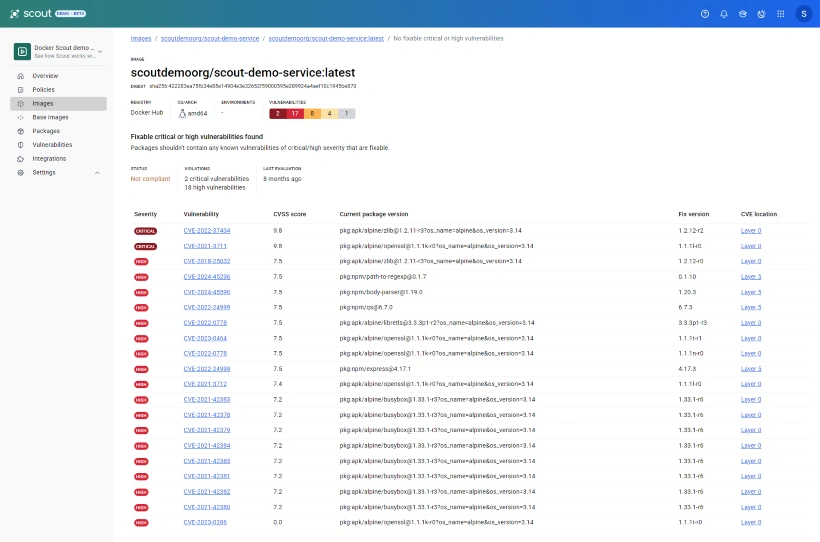
- Local Vulnerability Analysis: Scout can scan images locally on your machine (not just remote repos). The Docker Desktop UI has an “Images” view where you can click on any local image and see a breakdown of what Scout found – packages and their vulnerabilities. It’s a quick way to preview the security “health” of an image you just built.
- CLI Commands (docker scout Quickview, cves, compare): For those who prefer the terminal, Scout offers easy commands. For example, docker scout Quickview <image> gives you a summary of all found vulnerabilities in the image and its base image. The output looks something like a scorecard: e.g., “Your image has 2 critical, 8 medium, 15 low vulnerabilities; Base image has 1 critical, 3 high, etc.”. It even tells you how updating the base image might improve things (showing before and after counts). The docker scout cves command lists all the detailed vulnerabilities and affected packages, which is handy if you want to drill down or output a report. And docker scout compare lets you compare two images side-by-side, such as “What changed from last week’s build to this week’s build?” (very useful for regression tracking).
- Proactive Recommendations (Image Remediation): A big plus of Scout is that it suggests fixes. If a vulnerability is due to an outdated base image, Scout will often suggest an updated base or a patch. If it’s in a package, it might recommend upgrading that package. The Docker product page highlights “Image Remediation” as a feature – meaning Scout doesn’t just say “something’s wrong”, it helps you fix it. For example, in the Quickview above, it showed how moving from Debian Buster to Debian Stable cuts out all critical and high issues.
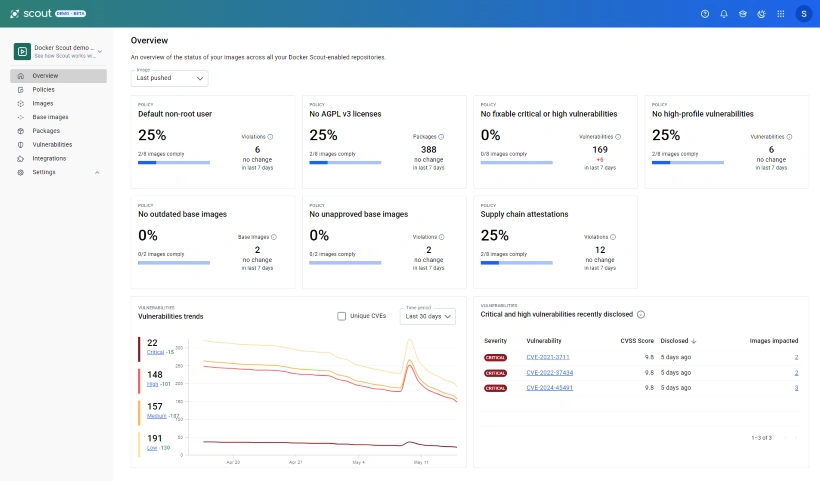
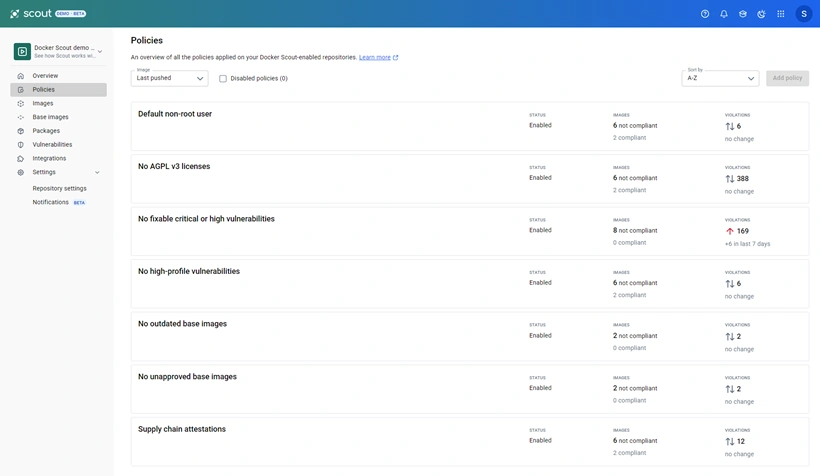
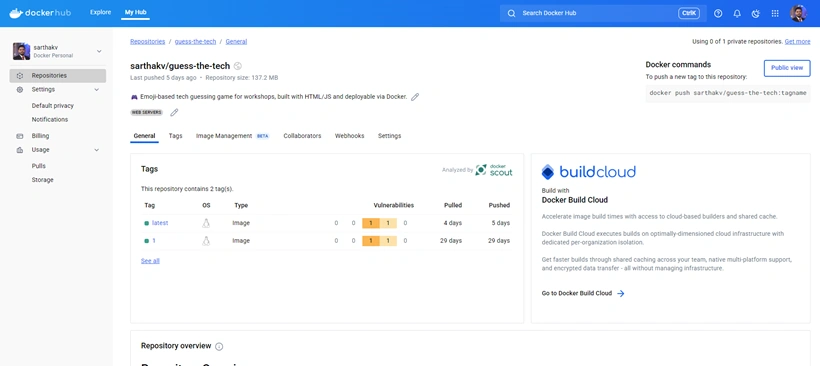
- Integration with Docker Hub and Policies: Scout extends beyond local machines. On Docker Hub, you can turn on Scout image analysis for any repository. Once enabled, every time you push a new image tag, Docker Hub will automatically run Scout on it in the background. This gives you an always-up-to-date report for any image on Docker Hub. Moreover, Docker Scout offers policy evaluation. You can define security policies (e.g., “no Critical vulnerabilities allowed”) and enforce them – builds or deployments can be stopped if they violate policies. This is like having an automated gatekeeper ensuring only safe containers progress through your pipeline.
- Software Development Lifecycle (SDLC) Integrations: Scout is designed to fit into your CI/CD workflow. It has integrations (and templates) for GitHub Actions, GitLab, Jenkins, etc. For instance, you might add a step in your Jenkinsfile to run docker scout cves on the built image – if any high-severity issues are found, you could fail the build automatically. An example CI integration from an Overcast blog shows how in Jenkins one could do,
This ensures every build is scanned.stage('Security Scan') { sh 'docker scout cves my-image:latest' } - Package URL (PURL) Matching: Under the hood, Scout uses Package URLs (PURLs) to match packages to CVEs instead of the broad Common Platform Enumeration (CPE) method that many older scanners use. What this means in practical terms is fewer false positives. Scout is focusing on exact package names and versions, so it’s usually more precise about what's really affected. In plain English, it’s like checking for bad apples by name and batch number rather than just saying “all apples from France” – more accurate.
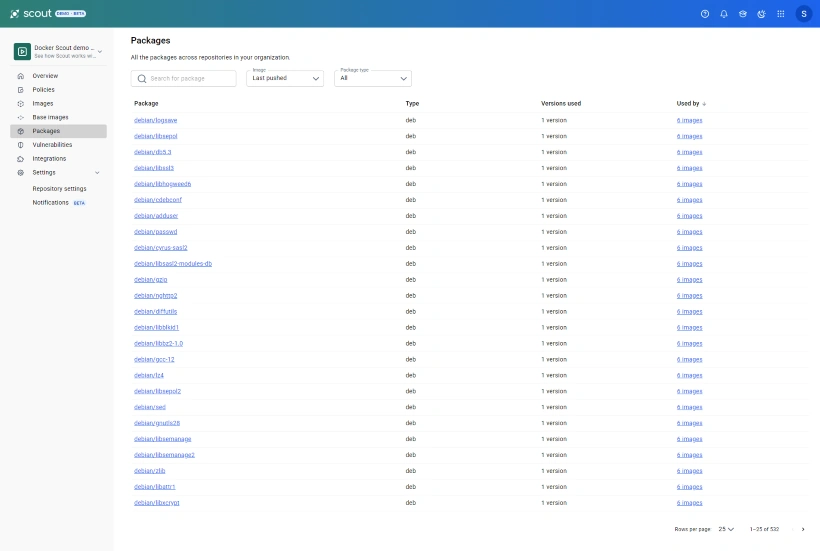
- Supported Ecosystems: Scout isn’t just for Linux OS packages. It supports a range of languages and ecosystems: .NET, Java, JavaScript/Node, Python, Ruby, PHP, and more, along with common Linux package formats (RPM, DEB, APK for Alpine, etc.). It can also use SBOMs from tools like Syft (for example) to analyze Docker images with dependencies in various languages.
So, to summarize: Docker Scout is an image security tool built into Docker’s ecosystem. It automatically scans images (both locally and in Docker Hub), detects vulnerabilities via an SBOM, suggests fixes, and fits into your CI/CD. It’s like having a built-in security guard that watches over your containers from development through deployment.
Using Docker Scout in Practice
How do you actually use Docker Scout? Let’s walk through a typical developer experience (with a sprinkle of anecdotes).
Say you’re building a new web service in a Docker image. You’ve chosen a base image (maybe node:14-alpine) and added your app code. Before pushing to production, you want to make sure your image isn’t carrying any surprises.
Join the conversation! Your thoughts help the community grow.