
As we know, using parameters is more secure, more readable, less error-prone, and negates the need to escape single quotes in text values.
Today, I am going to discuss about retrieving the records based on the values in a specific column in SQL database using IN Clause with sqlcommand.
Suppose, we have one table.
select * from tblemployee
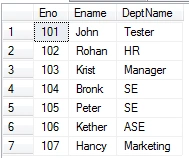
If we want to retrieve the data of "John, Rohan, Krist, Bronk, Peter" using SQL Query, then we can use
select * from tblemployee where ename in('John','Rohan','Krist','Bronk','Peter')
The output is given below.
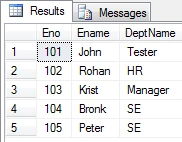
But if we try this with sqlcommand like this -
Today, I am going to discuss about retrieving the records based on the values in a specific column in SQL database using IN Clause with sqlcommand.
Suppose, we have one table.
select * from tblemployee
If we want to retrieve the data of "John, Rohan, Krist, Bronk, Peter" using SQL Query, then we can use
select * from tblemployee where ename in('John','Rohan','Krist','Bronk','Peter')
The output is given below.
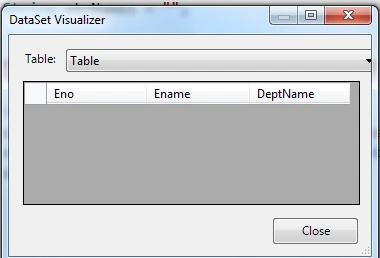
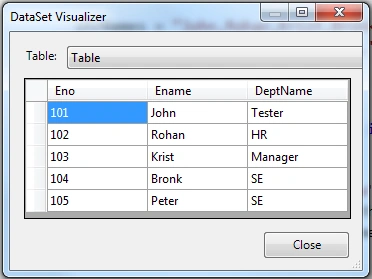
But if we try this with sqlcommand like this -
- DataSet ds = new DataSet();
- String strNames = "";
- strNames = "John,Rohan,Krist,Bronk,Peter";
- SqlCommand cmd = new SqlCommand();
- cmd.CommandText = "select * from tblemployee where ename in(@strNames)";
- cmd.Parameters.AddWithValue("@strNames", strNames);
- SqlDataAdapter da = new SqlDataAdapter();
- da.SelectCommand = cmd;
- da.SelectCommand.CommandTimeout = 0;
- da.Fill(ds);
Hadshana KamalanathanPosted Jul 15, 2018, 9:16 PM
Thank you for sharing information
jyoti singhalPosted May 24, 2018, 3:54 AM
My problem is not solve. i can not understand value of @idparam. where is this variable defined?