
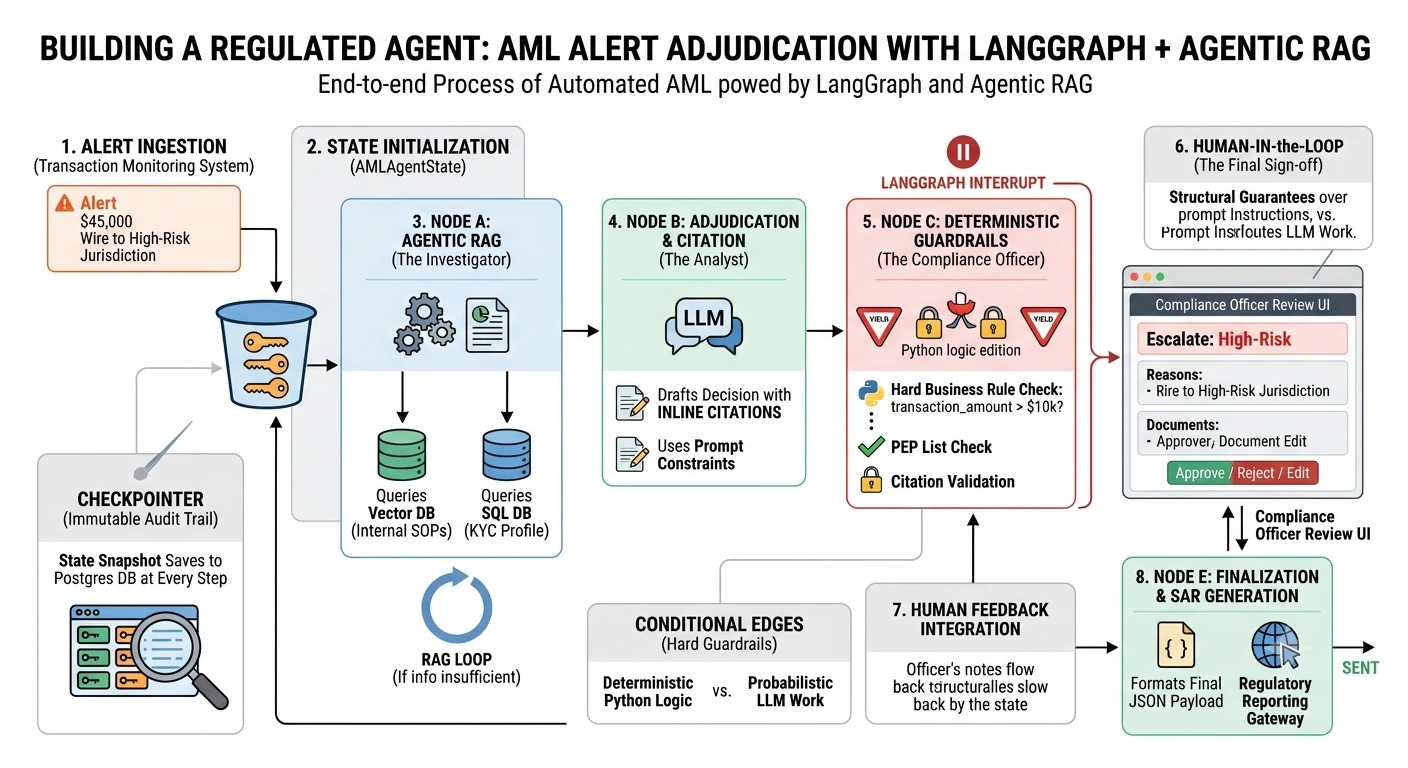
Moving Large Language Models (LLMs) into regulated industries such as finance, healthcare, and legal requires a fundamental shift in mindset. In these environments, an AI agent cannot simply be "smart"; it must be grounded, traceable, and strictly controlled.
Standard Retrieval-Augmented Generation (RAG) pipelines often fall short here. A basic RAG chain retrieves documents and generates an answer, but it lacks the ability to self-correct, enforce compliance guardrails, or pause for human approval.
To build a true Regulated Agent, we must combine the grounding power of RAG with the deterministic, stateful orchestration of LangGraph.
To illustrate this end-to-end, we will explore a high-stakes, real-time use case: Automated Anti-Money Laundering (AML) Alert Adjudication.
The Use Case: Real-Time AML Alert Adjudication
In modern banking, transaction monitoring systems generate thousands of AML alerts daily. For example, a customer who usually spends $500 locally suddenly wires $45,000 to a high-risk jurisdiction.
A human compliance analyst must investigate each alert. They must:
Review the customer's KYC (Know Your Customer) profile.
Analyze historical transaction patterns.
Consult internal Standard Operating Procedures (SOPs) and regulatory guidelines.
Decide whether to dismiss the alert (False Positive) or escalate it to file a Suspicious Activity Report (SAR).
The goal is to build a LangGraph-powered Regulated Agent that ingests these alerts in real time, uses Agentic RAG to gather context, drafts an adjudication decision, and seamlessly hands off to a human for final approval.
Why Standard RAG Fails in Regulated Environments
If we used a simple LangChain RAG chain for this, we would face three critical failures:
The Hallucination Risk: The LLM might invent a regulatory rule that doesn't exist to justify closing an alert.
The "Dead End" Retrieval: If the first retrieval doesn't yield enough context, a standard chain simply generates a low-quality answer. It can't say, "I need to look up the customer's specific business category first."
No Audit Trail: Regulators (like FinCEN or the FCA) require a step-by-step explanation of why a decision was made. A simple prompt-in/text-out chain leaves no structural audit trail.
The Solution: LangGraph + Agentic RAG
LangGraph solves these issues by treating the agent as a State Machine. We define strict nodes for our RAG and reasoning steps, use deterministic edges for compliance guardrails, and utilize LangGraph's native persistence for auditability.
1. Defining the State
In LangGraph, the State is the single source of truth. For our AML Agent, the state must capture the entire lifecycle of the investigation.
from typing import TypedDict, Annotated, List
from langgraph.graph.message import add_messages

class AMLAgentState(TypedDict):
    alert_id: str
    transaction_details: dict
    messages: Annotated[list, add_messages]  # LLM conversation history
    retrieved_kyc_data: dict
    retrieved_sop_docs: List[dict]
    llm_reasoning: str
    proposed_decision: str  # "Dismiss" or "Escalate"
    confidence_score: float
    human_reviewer_feedback: str
2. The Graph Architecture
We construct a StateGraph with specific nodes. Notice how we mix LLM nodes (probabilistic) with Python function nodes (deterministic).
Node A: Triage & Agentic RAG (The Investigator)
Instead of a single retrieval step, this node uses an LLM to perform Agentic RAG. It looks at the alert, decides what data it needs, retrieves it, and evaluates whether it has enough information.
Action:
Queries the Vector DB for internal AML SOPs.
Queries the SQL database for the customer's KYC profile.
Edge:
If the retrieved SOPs don't explicitly cover the transaction type, the LLM generates a new query and retrieves again (a loop).
If sufficient information is available, it routes to Node B.
Node B: Adjudication & Citation (The Analyst)
The LLM drafts the decision.
Crucially, we use a strict prompt requiring inline citations.
Prompt Constraint
"You must cite the specific SOP section or KYC data point for every claim. If you cannot find a regulatory basis to dismiss the alert, you MUST escalate it."
Node C: Deterministic Guardrails (The Compliance Officer)
This is a pure Python node (no LLM). It enforces hard business rules that the LLM cannot override.
Join the conversation! Your thoughts help the community grow.