
Introduction
An Azure Active Directory Domain Services (Azure AD DS) managed domain is deployed into an Azure virtual system subnet. It provides availability to clients and applications. This virtual network subnet should be used for the managed domain resources provided by the Azure platform.
As you make your own VMs and applications, they shouldn't be deployed into the same virtual system subnet. Rather, you might create and deploy your applications into a different virtual network subnet, or in a different virtual network peered to the Azure AD DS virtual network.
Virtual Network Peering
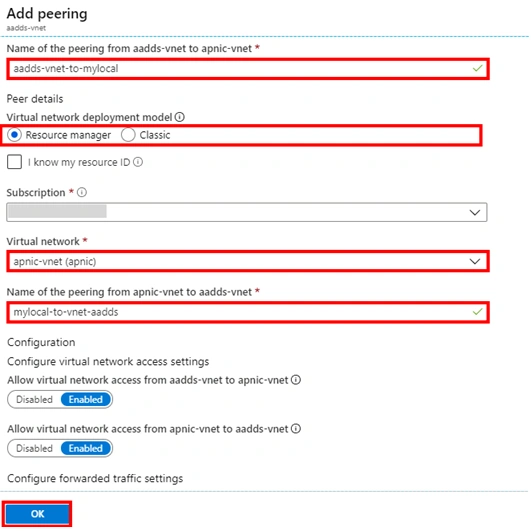
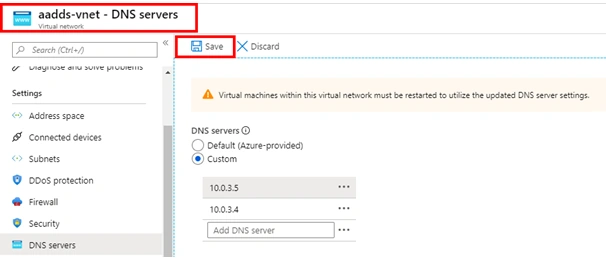
You may have a current Azure virtual network for VMs or keep your Azure AD DS managed domain virtual network isolated. To use the managed domain, VMs in other virtual networks need an approach to communicate with the Azure AD DS domain controllers. This availability can be given using the Azure virtual network peering.
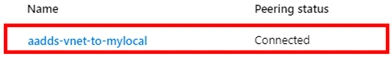
With Azure virtual network peering, two virtual networks are connected, without the requirement for a virtual private network (VPN) device. Network peering lets you rapidly interface virtual networks and confine traffic streams over your Azure environment.
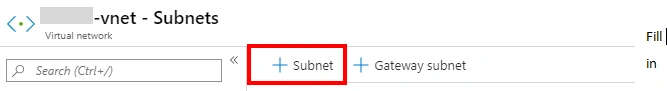
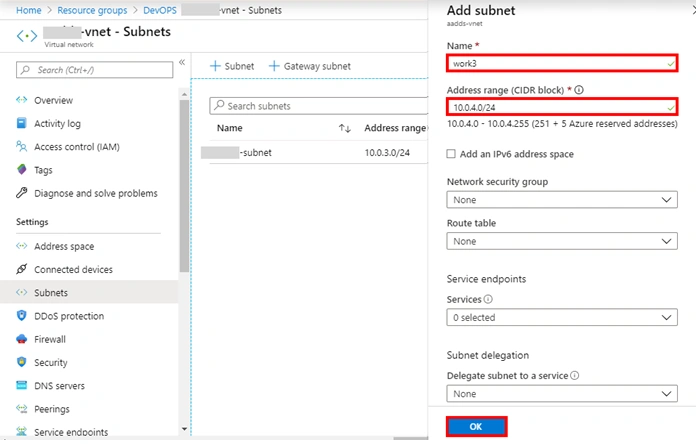
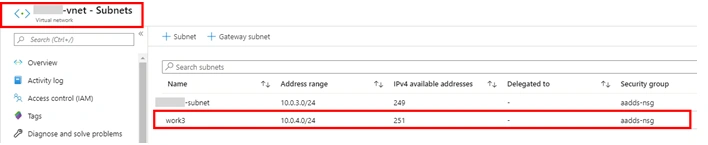
Creating a Virtual Network Subnet
Sign in to the Azure portal. Then click on the Azure portal menu. Select Create a resource. Then, select the resource group of your created Azure AD DS managed the domain from the list of resources.
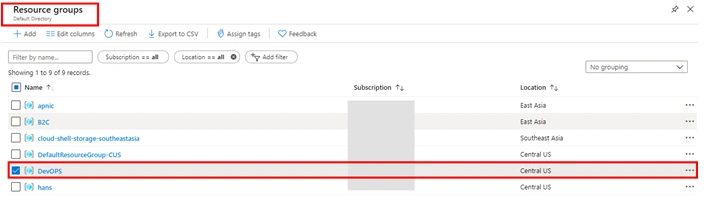
Then, select the default virtual network from the list here and open it.
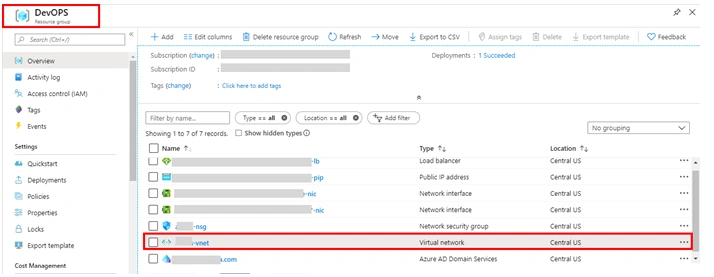
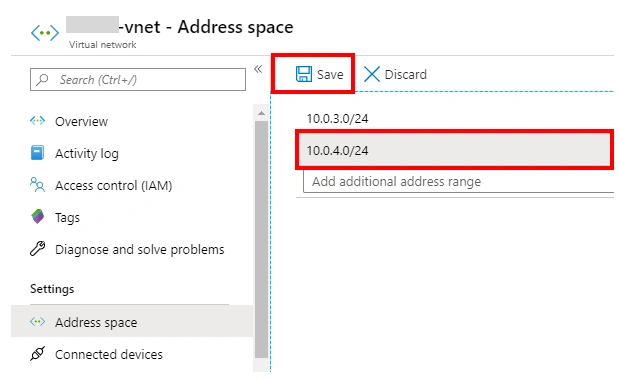
After that, open the Address space for configuring.
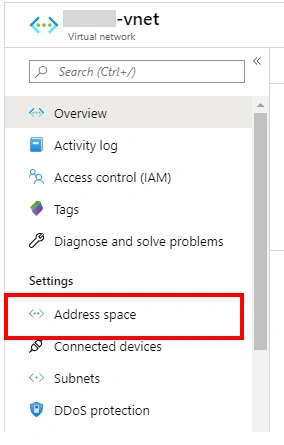
The virtual network is created with a single address and then used by the default subnet. After this, everything is ready. Select Save.
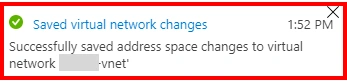
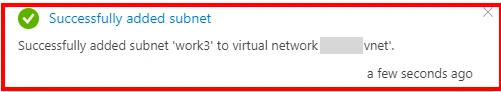
After saving, you should receive a successfully saved address space.

Dasindu PereraPosted Nov 20, 2019, 3:21 AM
Nice article
Chittaranjan SwainPosted Nov 19, 2019, 8:45 AM
Nice article.