
In this article, I am going to explain how to create an Azure Virtual Network, Subnets, and Network Security Groups and how to associate them with Virtual Machines.
To understand more about what Virtual Networks, Subnets, Network Security Groups are and topics around them, read my article here. You will need an Azure Subscription to go ahead with this demo.
Step 1
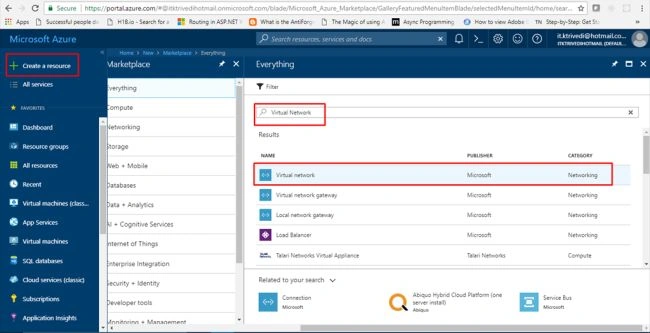
Go to portal.azure.com and sign in with your credentials. Click on "Create a Resource", search for Virtual Network, and click on Virtual Network in the results.
To understand more about what Virtual Networks, Subnets, Network Security Groups are and topics around them, read my article here. You will need an Azure Subscription to go ahead with this demo.
Step 1
Go to portal.azure.com and sign in with your credentials. Click on "Create a Resource", search for Virtual Network, and click on Virtual Network in the results.
Step 2
It will open a new blade. Click on "Create".
Step 3
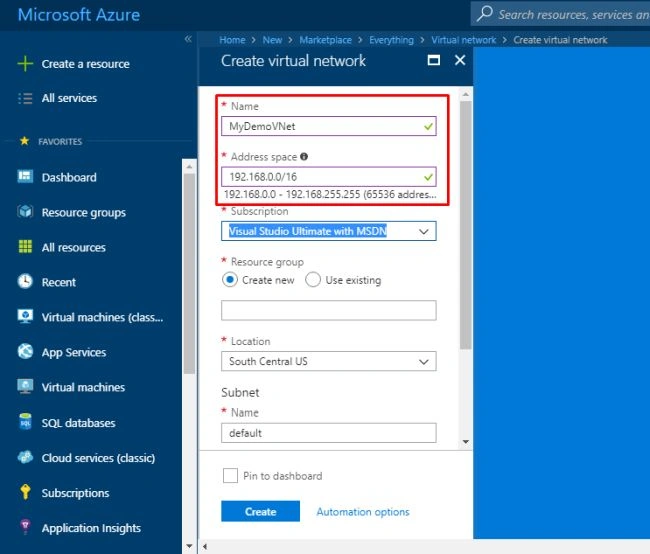
Give a name to your VNet. Since we are going to have subnets inside our VNet, we need to have the address space as 192.168.0.0/16.
Step 4
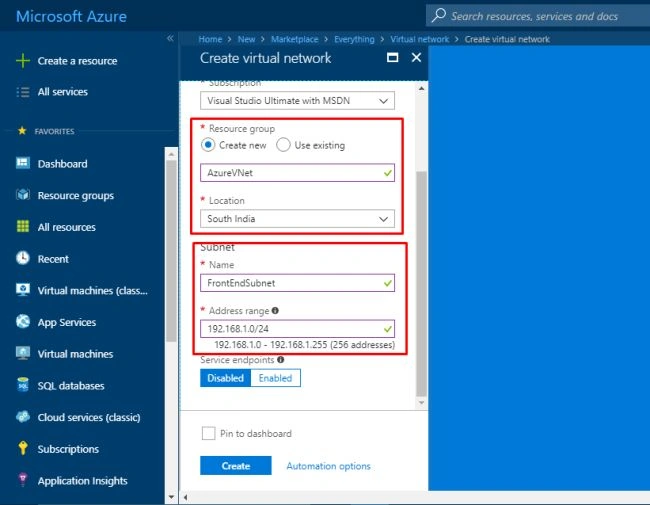
Select the resource group that you want or create a new one. Give a name to your subnet as FrontEndSubnet and give the address range as 192.168.1.0/24. We are going to create another subnet later on. "Pin to dashboard" and click "Create".
Select the resource group that you want or create a new one. Give a name to your subnet as FrontEndSubnet and give the address range as 192.168.1.0/24. We are going to create another subnet later on. "Pin to dashboard" and click "Create".
Step 5
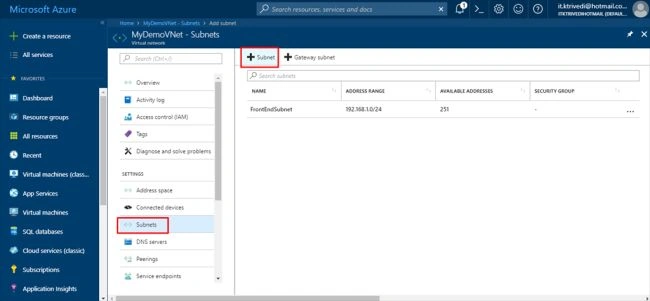
Open your Virtual Network and click on subnets. Click on "Add" to add your second subnet.
Open your Virtual Network and click on subnets. Click on "Add" to add your second subnet.
Step 6
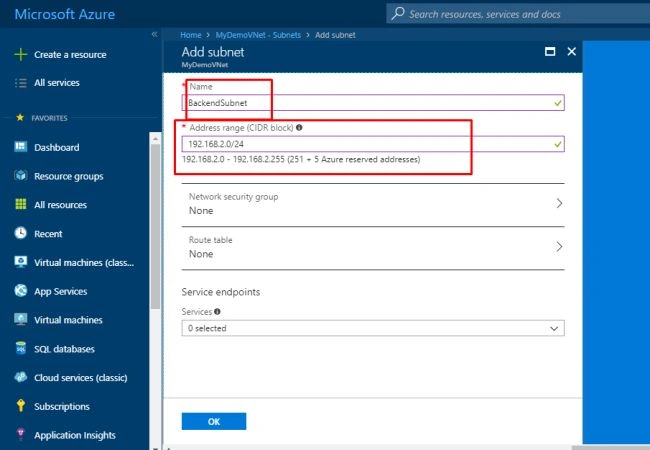
Give the name BackendSubnet to it. Set the address range/CIDR block as 192.168.2.0/24. Leave Network Security Group and Route Table empty since we are going to create them later on. Click on OK.
Give the name BackendSubnet to it. Set the address range/CIDR block as 192.168.2.0/24. Leave Network Security Group and Route Table empty since we are going to create them later on. Click on OK.
Step 7
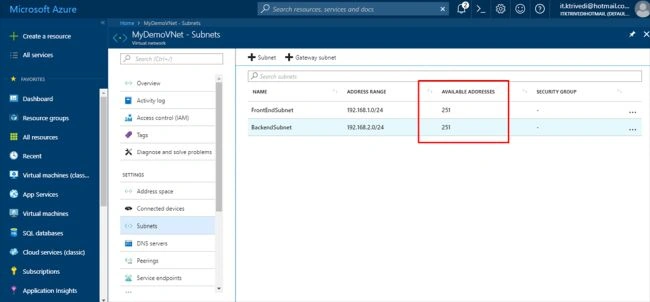
You will see that the available addresses are 251 in both the CIDR blocks. Because the first four and the last, i.e., a total of five, addresses are used for reserve purposes and cannot be used.
You will see that the available addresses are 251 in both the CIDR blocks. Because the first four and the last, i.e., a total of five, addresses are used for reserve purposes and cannot be used.
Step 8
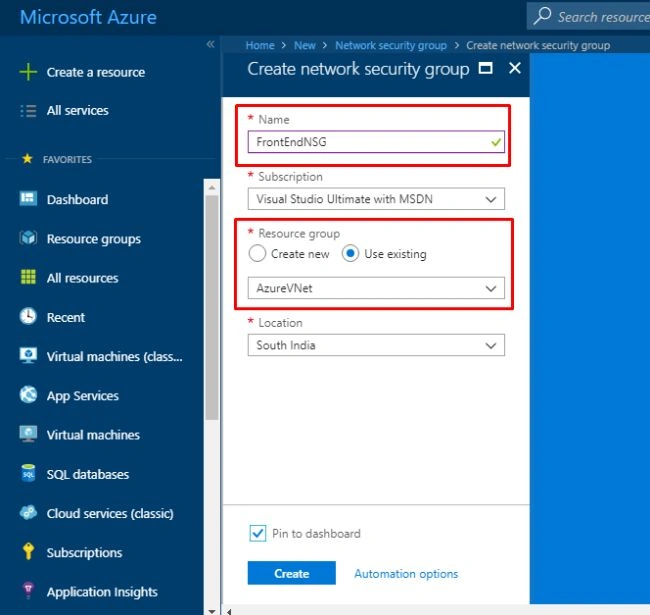
Now, we are going to create two Network Security Groups. One will be for the front-end and the other one will be for the back-end.
Step 9
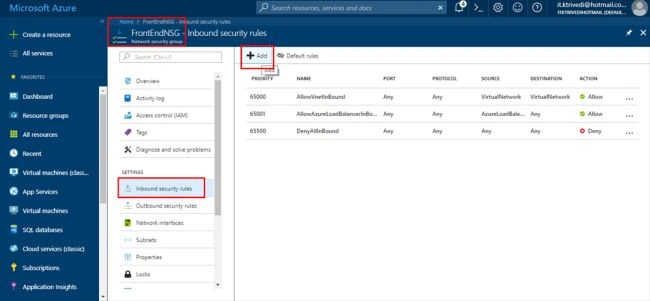
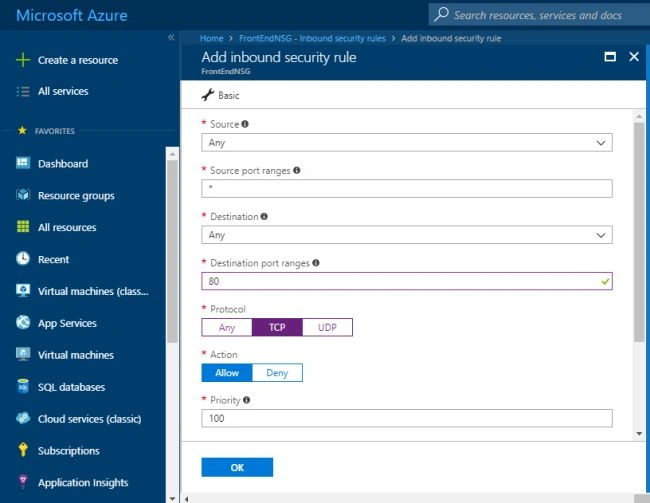
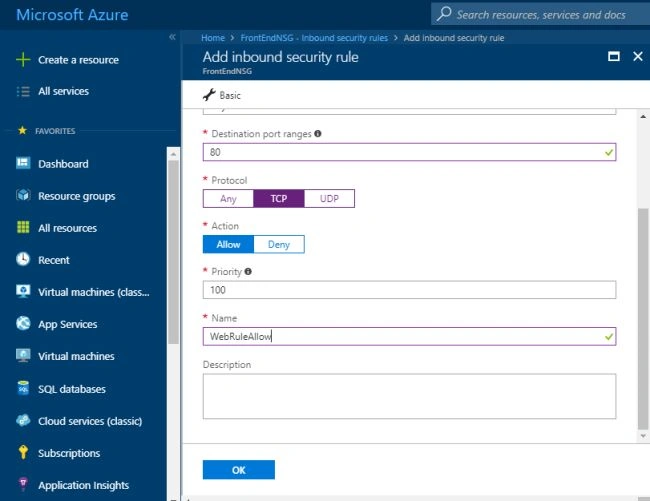
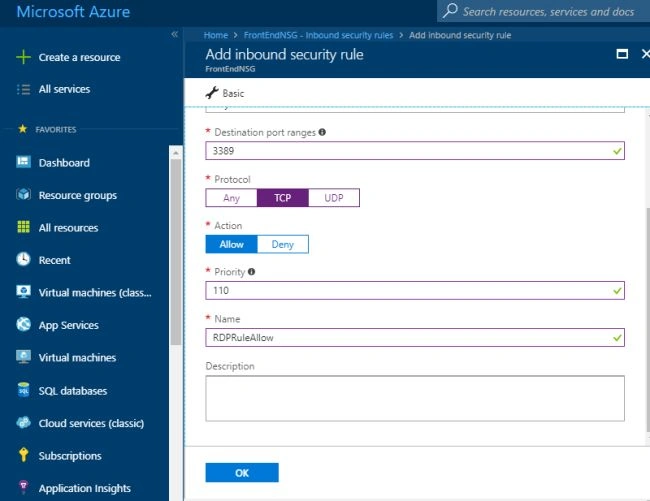
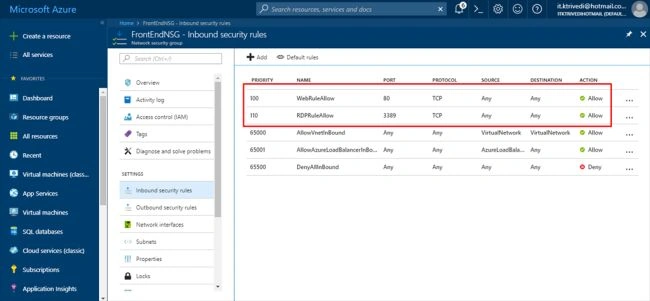
Front End NSG will use two rules,
Now, we are going to create two Network Security Groups. One will be for the front-end and the other one will be for the back-end.
Step 9
Front End NSG will use two rules,
- rdp-rule: This will allow RDP traffic to the Front End Subnet.
- web-rule: This will allow HTTP traffic to the Front End Subnet.
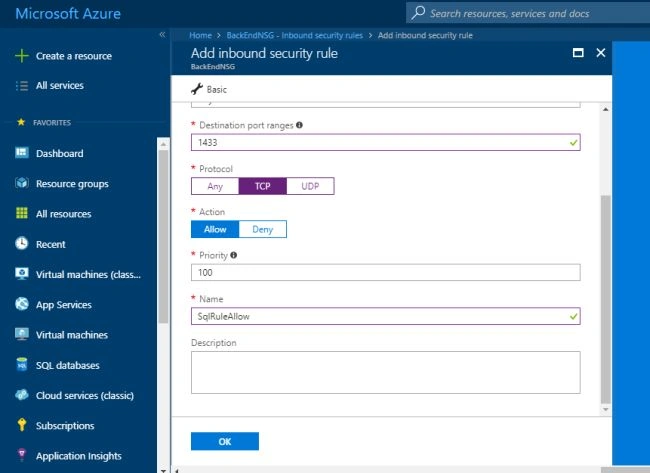
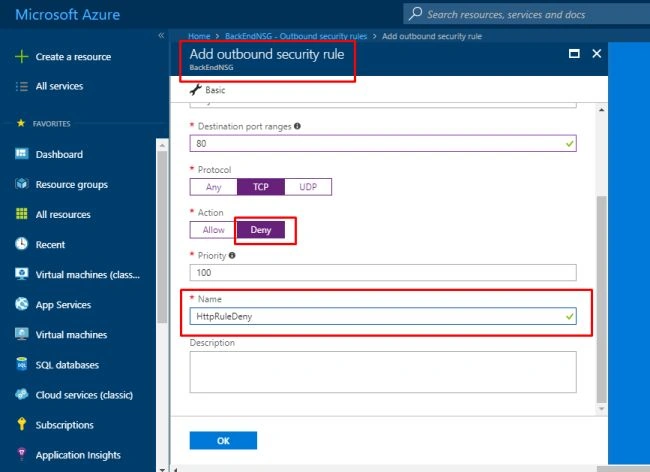
Back End NSG will use three rules,
Join the conversation! Your thoughts help the community grow.