
Introduction
Microsoft Graph API is the unified REST endpoint that enables applications to access data across Microsoft 365 and Microsoft Entra ID (formerly Azure Active Directory). Through a single API surface, developers can securely interact with users, groups, roles, applications, mail, calendars, and many other organizational resources.
In enterprise applications, Microsoft Graph is commonly used to:
Read users and groups from MS Entra ID
Manage access and authorization logic
Integrate Microsoft 365 data into custom applications
Automate identity and security workflows
Because Microsoft Graph exposes highly sensitive organizational data, secure authentication is mandatory. Microsoft Entra ID provides multiple authentication mechanisms for confidential client applications, with client secrets and client certificates being the most common.
Securing Microsoft Graph API Access
Client Secret Authentication
Client secret authentication utilizes a shared secret string generated during app registration. The application presents the client ID and client secret to Microsoft Entra ID to obtain an access token for Microsoft Graph.
When to use?
Local development
Proof-of-concept applications
Short-lived testing environments
Limitations
Secrets are static strings that can be leaked via source control, logs, or misconfiguration
Requires frequent rotation
Higher risk if compromised, as secrets cannot prove application identity cryptographically
While client secrets are easy to implement, Microsoft does not recommend them for production workloads.
Client Certificate Authentication (Recommended)
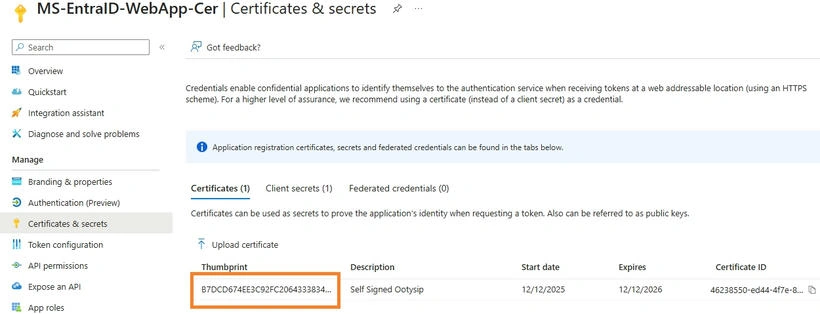
Client certificate authentication uses an X.509 certificate to authenticate the application. Instead of sending a shared secret, the application proves its identity by signing a request using the certificate’s private key.
Microsoft Entra ID validates the signature using the public key uploaded to the app registration.
Why is this more secure?
No shared secret is transmitted
Private keys never leave the application environment
Certificates support cryptographic proof of identity
Strong resistance to credential leakage and replay attacks
Supports hardware-backed protection (HSM, Key Vault)
Due to these security advantages, Microsoft strongly recommends using client certificate authentication for production applications.
Join the conversation! Your thoughts help the community grow.