
Introduction
In the realm of secure system management, Identity and Access Management (IAM) plays a pivotal role, encompassing two crucial aspects: authentication and authorization. While authentication verifies user identity, authorization determines user access rights. This presentation delves into the significance of IAM, particularly focusing on the implications of utilizing a root user account.
Section 1. Understanding Authentication and Authorization
Authentication: This process involves verifying the identity of users attempting to access a system. It ensures that users are who they claim to be through various authentication factors, such as passwords, biometrics, or security tokens.
Authorization: Once a user's identity is confirmed, authorization comes into play. It determines the level of access and actions a user is allowed within the system. Proper authorization guarantees that users can only interact with resources they are permitted to use.
Section 2. Exploring the Root User Account
Role of the Root User: The root user account holds the highest level of authority within a system. It possesses the ability to perform any action, making it an extremely powerful entity. Root user privileges grant unrestricted control over the system's configuration and data.
Security Implications: Entrusting the root user credentials to anyone grants them unfettered access to your system. This unparalleled control could lead to catastrophic consequences if exploited. Hence, it is strongly advised to exercise caution when using the root user account.
The Best approach is to create an IAM user and use the IAM user for day-to-day activities.
Moving forward, let's create an IAM Group. Why IAM Group?
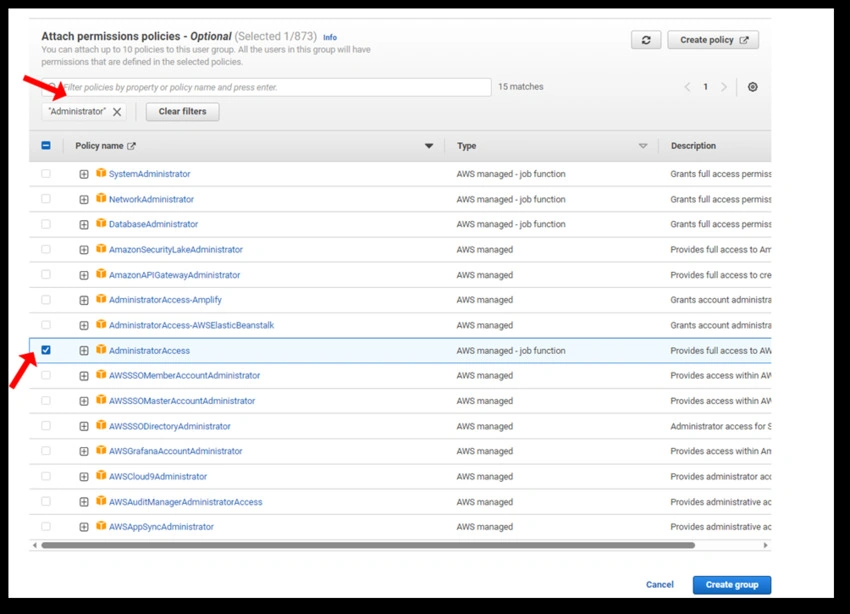
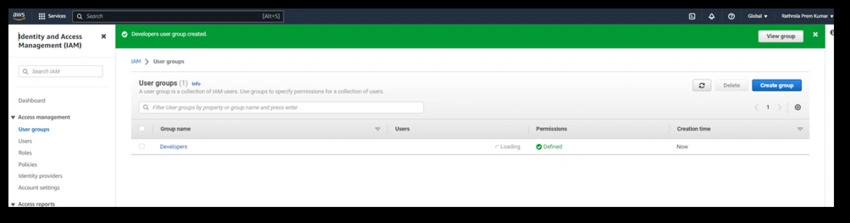
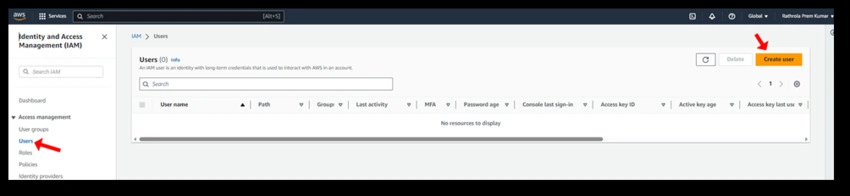
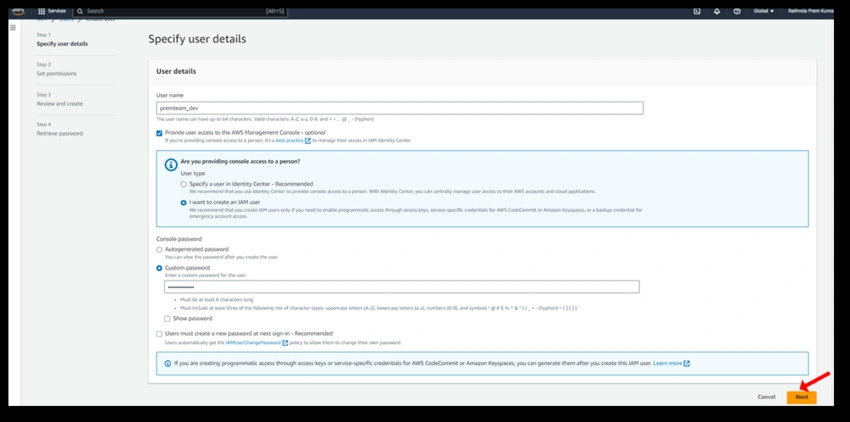
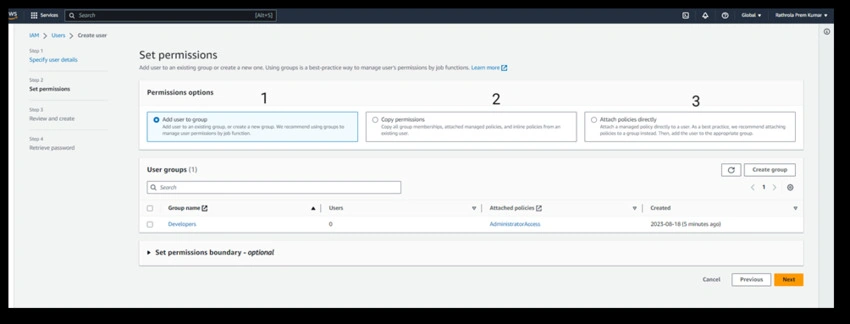
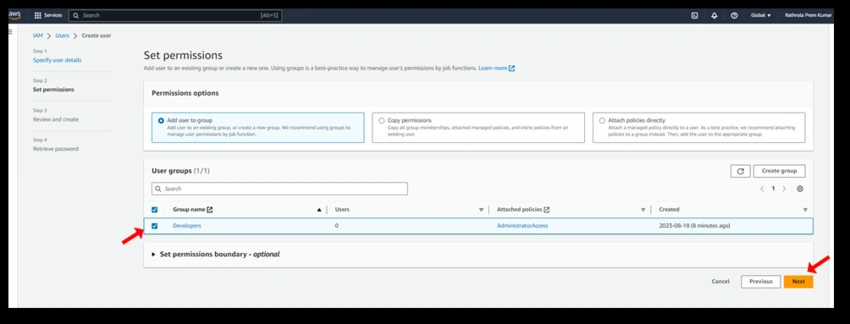
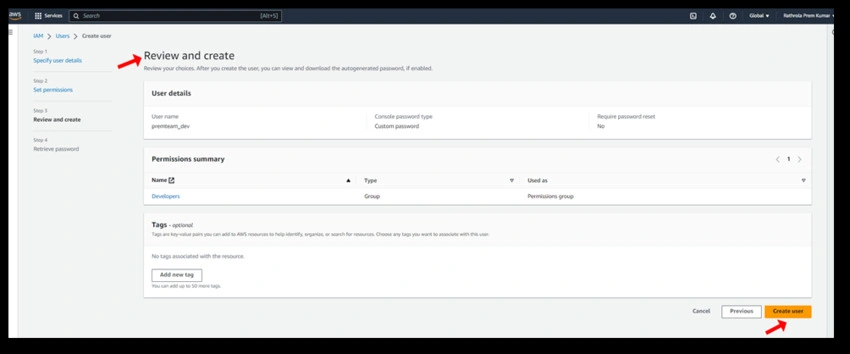
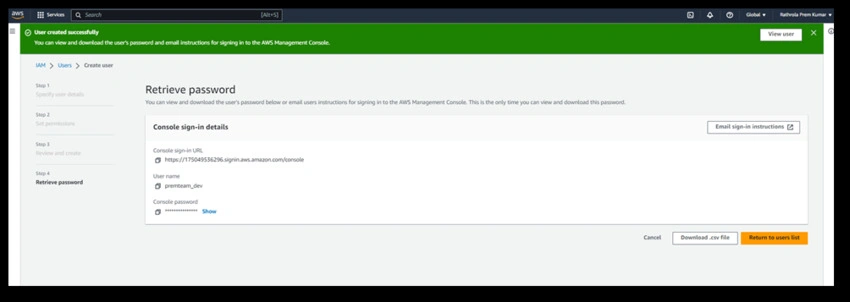
We might have hundreds of IAM Users, but we don’t want to manage permissions for them individually. That’s where we would create an IAM Group. After creating the group, we will create IAM User, and we would make it part of the above newly created IAM Group.
Let’s get started.
Create an IAM Group
Before creating the IAM Group, we will need to login into a management console.
There is a wide variety of things we can do in the management console.
For eg., if you want to see the list of services in the US, you can click the view all services as shown below.
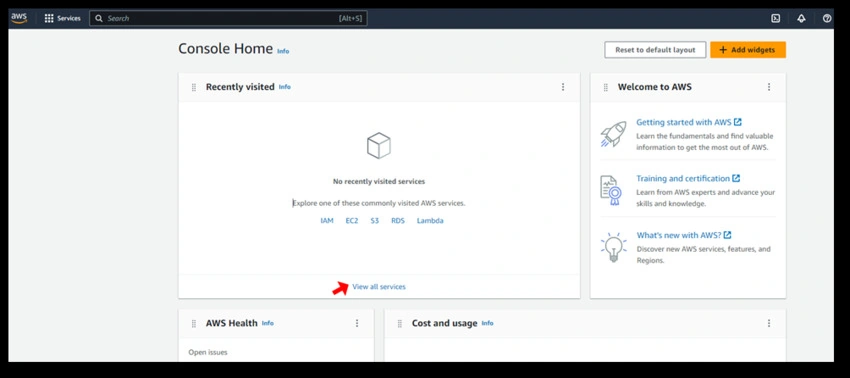
Over here, we can see the list of services that are present under different categories in the US.
Now, search for the IAM as shown below,
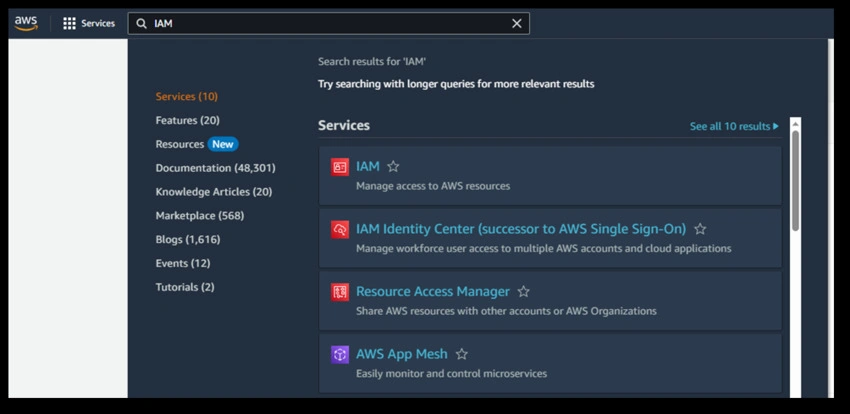
Let's click on IAM.
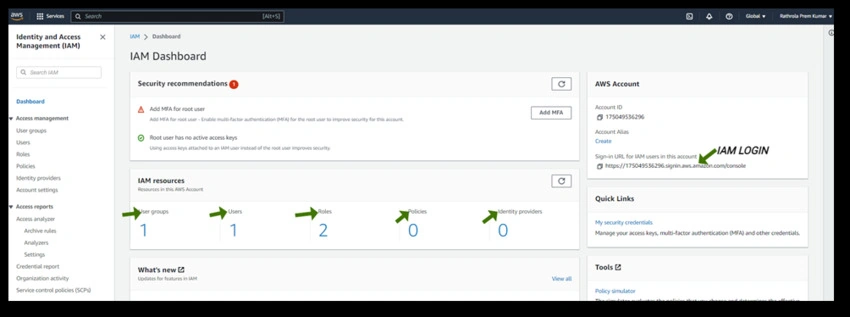
On the IAM page, we can create users, we can create groups, and we can also manage permission for resources.
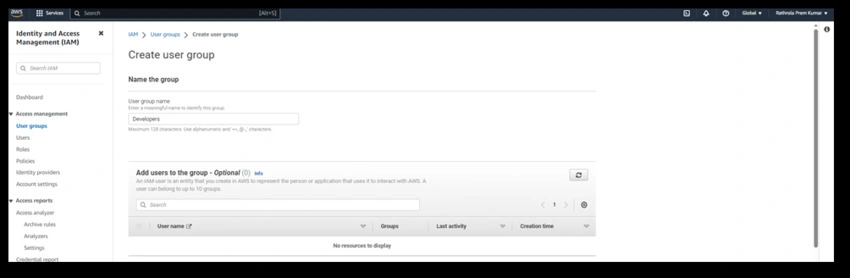
Select User Groups under the Access Management menu and click on Create Group button, as shown in fig.

Join the conversation! Your thoughts help the community grow.