
Introduction
In this article, I will explain how to manage users and permissions in Azure DevOps. Kindly make sure you read my previous article for better understanding. This is the fourth article of my Azure DevOps series. If you feel that it is difficult to manage users and permissions in Azure DevOps service, it's absolutely not. Azure DevOps provides readily available services that allow the organization to manage users and permissions.
Let's get started.
- How to add a user to a particular project in an organization.
- Assign permission to projects in an organization.
Adding a user to an organization
It's important to add users to an organization at the project level up to the number of users in the project. If you are managing a large number of users, then use on-premises active directory. But, if you are managing a small number of users, you can use Azure active directory.
If you are not aware of on-premise active directory and Azure active directory, stay tuned for my next article about active directories. Anyway, it's not important now in this process. You can continue with the basic knowledge of Azure DevOps. In this demo, I am using a separate Microsoft account.
Step 1
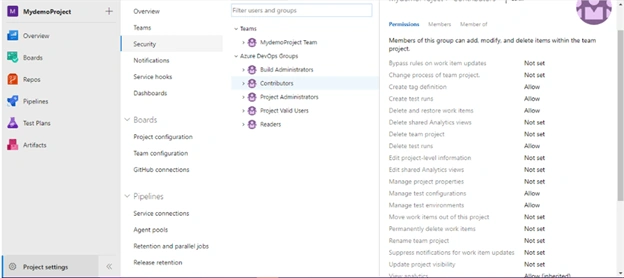
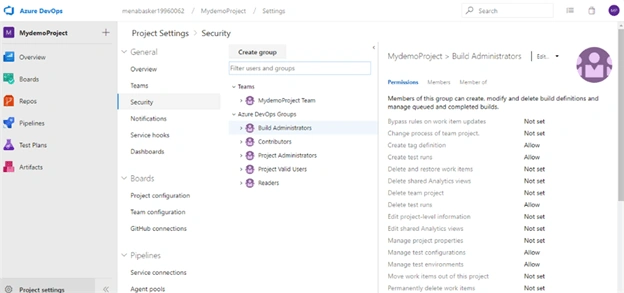
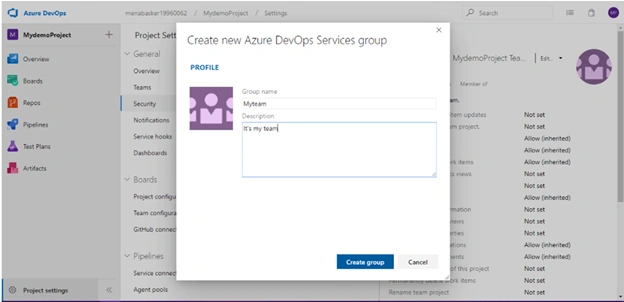
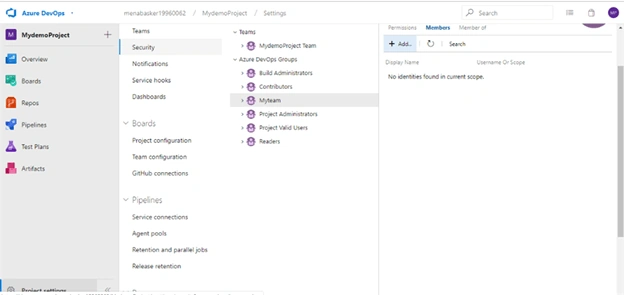
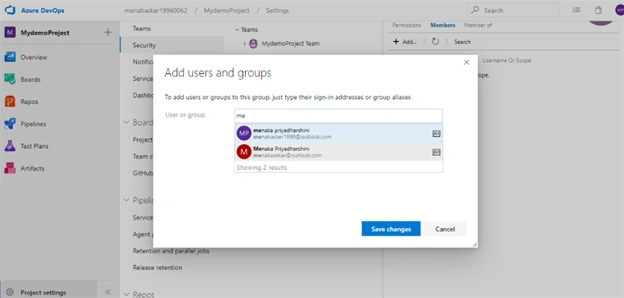
Open project, click project Settings --> Security. Once it is done, the names of default teams along with their security groups will be available. Most of the projects will use default security groups.
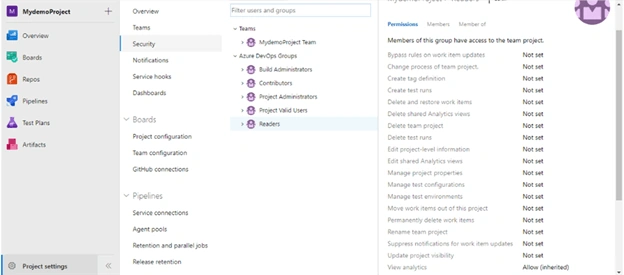
A user having an account with the "reader" permission can view the project. The "Reader" permission allows only to view the project, not to manage or access the project.
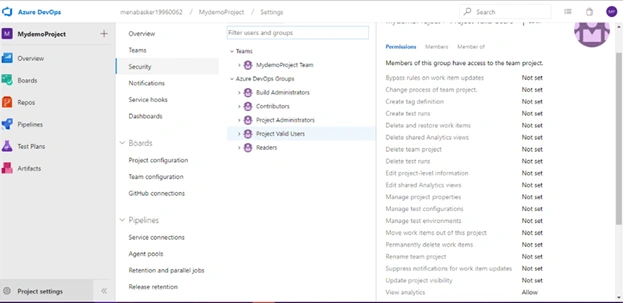
The user with "valid user" permission can access the project but is not allowed to manage the project.
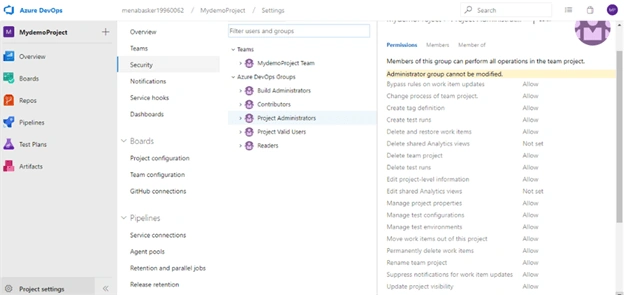
User accounts with "project administrator" permission can perform all operations in the team project.
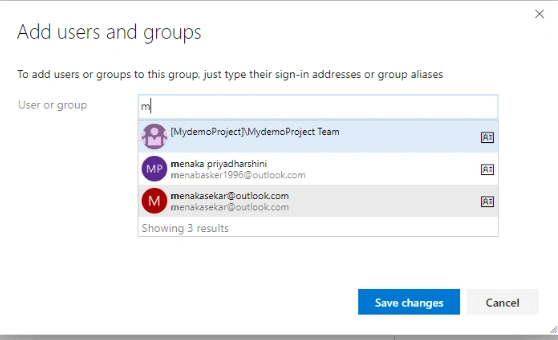
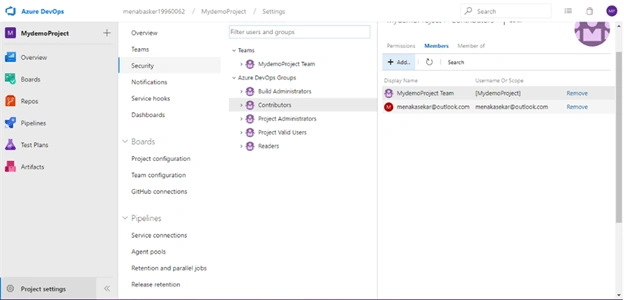
A user account with "contributors" permission can perform all operation as well as track the project. Mostly users are added to contributors.
deepak karmaPosted Jun 9, 2020, 7:07 AM
Can we access list of Groups and members through C# code?