
Introduction
Organizations frequently deploy web applications that need to communicate with backend APIs securely. A common challenge arises when multiple applications are hosted on the same infrastructure, such as an Internet Information Services (IIS) server on an Azure Virtual Machine. Without proper security controls, any application on that server could potentially access backend APIs, creating security vulnerabilities and compliance concerns.
This article presents a comprehensive solution for securing a Blazor .NET 8 web application that calls backend APIs through Azure API Management (APIM). The solution leverages Azure Managed Identity to ensure that only the authorized application can access the backend API.
This is an extension of my previous article, where I wrote about securing Azure API Management with the Zero Trust Architecture and tested it using VisualStudio credentials.
Business Scenario
Consider a scenario where an organization has deployed a Blazor web application on an Azure Virtual Machine running IIS. The application needs to call a Weather API hosted behind Azure API Management. The security requirements include:
Only the Blazor application should be able to call the backend API
No credentials or secrets should be stored in the application configuration
The solution should work seamlessly in production without manual token management
Access should be auditable and easily revocable
Traditional approaches to API security often involve:
Storing API keys or client secrets in configuration files or in the Key Vault
Managing certificate lifecycles
These approaches introduce security risks and operational overhead. Managed Identity eliminates these concerns by allowing Azure resources to authenticate with services that support Azure Active Directory without requiring credentials in code.
The Demo solution consists of the following components:
1. Blazor .NET 8 Client Application
A server-side Blazor application that provides an interactive user interface and makes authenticated calls to the backend API.
2. Azure Virtual Machine with IIS
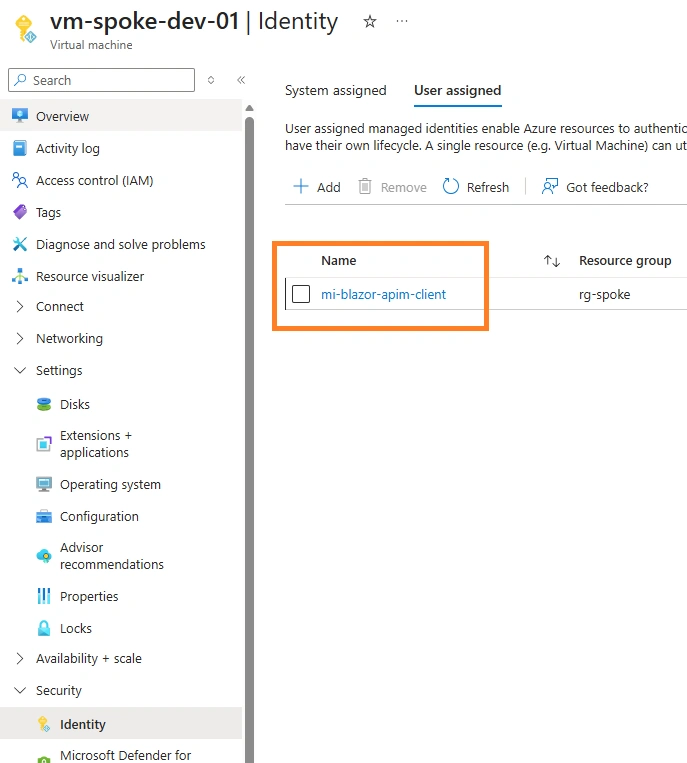
The hosting environment for the Blazor application is configured with a User-Assigned Managed Identity.
3. User-Assigned Managed Identity
An Azure resource that provides an identity for the application to use when authenticating to Azure services.
4. Microsoft Entra ID (Azure Active Directory)
The identity provider that issues tokens and manages application registrations and permissions.
5. Azure API Management
The API gateway that validates JWT tokens and enforces access policies before routing requests to the backend.
6. Backend Web API
The protected API that serves weather forecast data is registered in Entra ID with defined app roles.
The authentication flow follows these steps:
Step 1: The Blazor application starts on the Azure VM
Step 2: When the application needs to call the backend API, it requests a token from Entra ID using the Managed Identity
Step 3: Entra ID validates the Managed Identity and issues a JWT token with the appropriate claims and roles
Step 4: The application sends the API request to APIM with the JWT token in the Authorization header
Step 5: APIM validates the JWT token, checking the issuer, audience, and required claims
Step 6: If validation succeeds, APIM forwards the request to the backend API
Step 7: The backend API processes the request and returns the response
Step-by-Step Implementation
Step 1: Create the Backend API App Registration
Please refer to my last article on Securing Azure API Management with DefaultAzureCredential and Zero Trust Architecture, where I gave step-by-step instructions on registering the MS Entra ID application for the Backend API
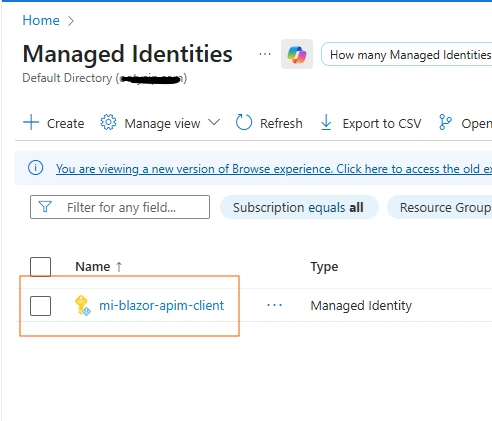
Step 2: Create the User-Assigned Managed Identity
1. Navigate to the Azure Portal
2. Search for Managed Identities and click Create
3. Enter the following details:
Subscription: Your subscription
Resource group: Your resource group
Region: Same region as your VM
Name: give some name (example: mi-blazor-apim-client)

Join the conversation! Your thoughts help the community grow.