
Many Web Applications do not properly protect the sensitive data such as password, credit card number, Email Id and mobile number etc. The attackers may steal or modify such weakly-protected data in many ways.
Scenarios to Avoid Exposure of Sensitive Data
There are mainly two techniques required to avoid exposure of sensitive data,
- Hashing.
- Encryption
Hashing
Hashing is the process of generating a unique string in an encrypted format for the given input.The best hashing algorithms are designed so that it’s impossible for the hacker to convert the hashed string into the original string.
Popular Algorithms
- MD5 (Message Digest 5 algorithm)
- SHA (Secure Hash algorithm)
MD5
MD5 is the most widely known hash function. It produces a 16 byte hash value, usually expressed as a 32 digit hexadecimal number.
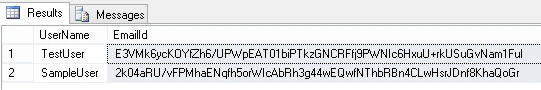
The screenshot, given below, explains the procedure of hashing, using MD5.
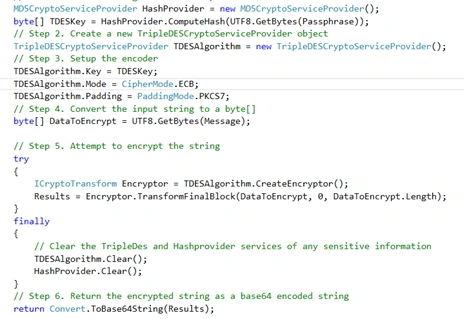
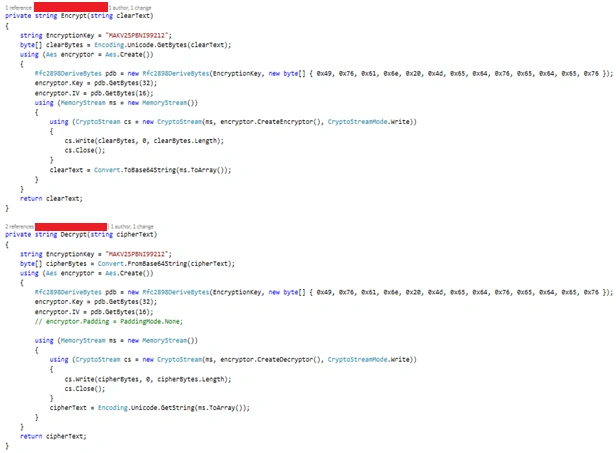
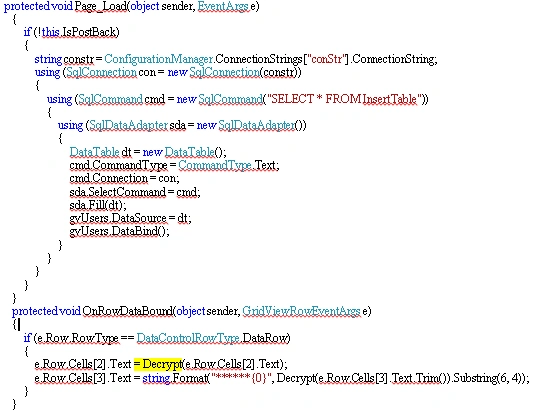
The code, given below, decrypts the hashed text:
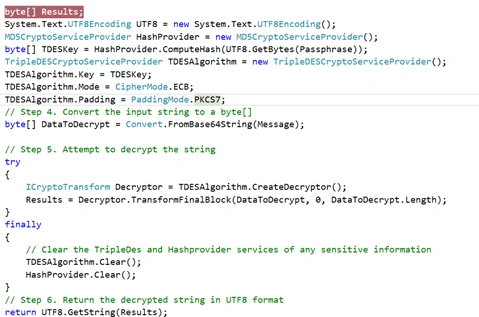
From the above screenshots, we observe
MD5CryptoServiceProvider: is used to compute the Hash and create a valid TripleDES private key.
TripleDESCryptoServiceProvider
It accepts the initialization vector and the private key.
TripleDES, as its name itself show, increases the encryption strength by applying the DES encryption algorithm to the data three times, before rendering to a result. As shown in the image, given below, the string or number is encrypting and decrypting three times:
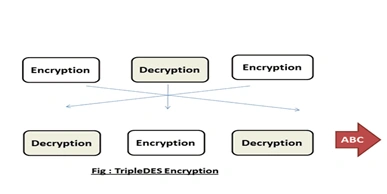
By creating an object of TripleDescryptoserviceprovider, we have few properties. We can say mode, padding etc...
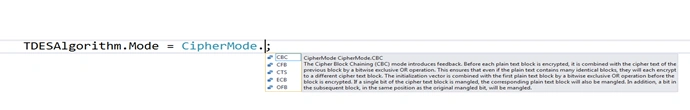
We have a few Cipher Modes (Encrypted modes).They are,
- CBC (Cypher Block chaining)
- ECB (Electronic Codebook)
- CFB (Cipher feedback)
- CTS (Cypher text stealing)
- OFB (Output Feedback)
CipherMode.ECB
The Electronic Codebook (ECB) mode is the simplest mode among the available encryption modes.The message is divided into the blocks and each block is encrypted separately.
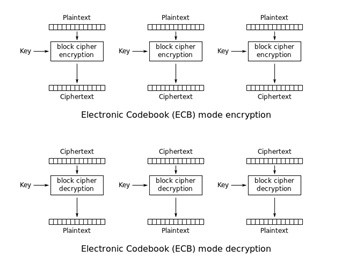
Advantages of using ECB: ECB supports Encryption parallelizable and Decryption parallelizable.
Disadvantages of using ECB
Identical plaintext blocks are encrypted into the identical cipher text blocks. Thus, it doesn't get out of sight data patterns. To some extent, it doesn't provide the serious message confidentiality.
CipherMode.CBC
In CBC mode, each block of the plaintext depends on the previous cipher text block, before being encrypted. As shown below in the screenshot, each cipher text block relies on all plaintext blocks, processed until that point of time. To make each message unique, in the first block, an initialization vector must be used.
Initialization Vector(IV)
It is an arbitrary number, that can be used along with a secret key for the data encryption.
The use of IV prevents a repetition in the data encryption and it makes it more difficult for the hacker to break a cipher.
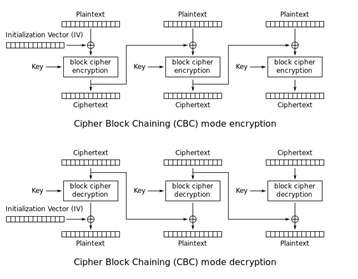
Disadvantages of using CBC
CBC does not support parallelizable encryption .
CipherMode.OFB
The Output Feedback (OFB) mode makes a block cipher into a synchronous stream cipher. It generates the keystream blocks, which will be XORed with the plaintext blocks to produce the cipher text.
Stream cipher
It is a mechanism of encrypting the text to produce a cipher text, in which a cryptographic key and algorithm are applied to each and every binary digit in a data stream, one bit at a time.
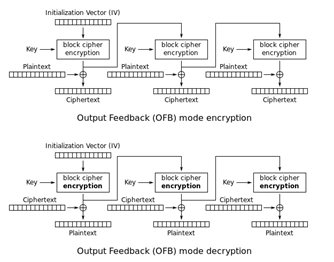
Disadvantages of using OFB
Each output block cipher operation depends on all the previous blocks and that is why, it cannot be performed in parallel.
OFB does not support Encryption Parallelism and Decryption parallelism.
CipherMode.CFB
The Cipher Feedback (CFB) mode is a close relative of CBC and makes a block cipher into a self-synchronizing stream cipher. This operation is very similar to CBC and CFB decryption is almost identical to CBC encryption, performed in reverse.
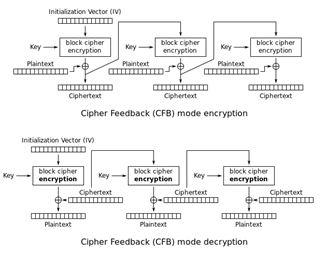
Advantages of using CFB
CFB shares two advantages over CBC mode:
- The block cipher is only used in the encrypting direction.
- The message does not need to be padded to a multiple of the cipher block size.
CipherMode.CTS
This mode handles any length of the plain text and produces cipher text, whose length equals the plain text length. This mode behaves in the same way as CBC mode behaves.
Padding
The screenshot, given below, explains the different padding modes, available in TDESAlgorithm.
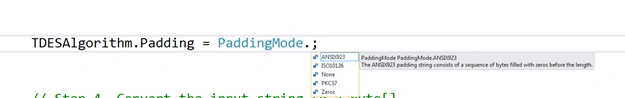
PaddingMode.ANSIX923
In ANSIX923, zeros are filled for the bytes with padded and the last byte defines the padding boundaries or the number of padded bytes.
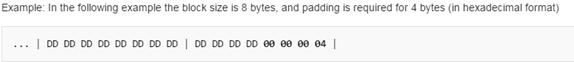
PaddingMode.ISO10126
Specifies that the padding should be done at the end of the last block with the random bytes and the last byte should specify the padding boundary.
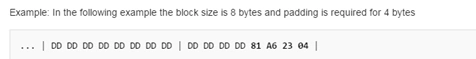
PaddingMode.PKCS7
Padding is in whole bytes. The value of each added byte is the number of bytes, that are added.This padding method (as well as the previous two) is well-defined, if and only if, N is less than 256.
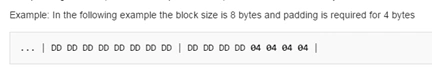
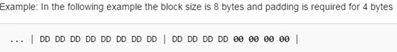
PaddingMode.Zeroes
All the bytes that are required to be padded are padded with zero. The zero padding scheme has not been standardized for the encryption, although it is specified for the hashes and MACs
ICryptoTransform
The ICryptoTransform defines the basic operations of the cryptographic transformations.
TransformFinalBlock
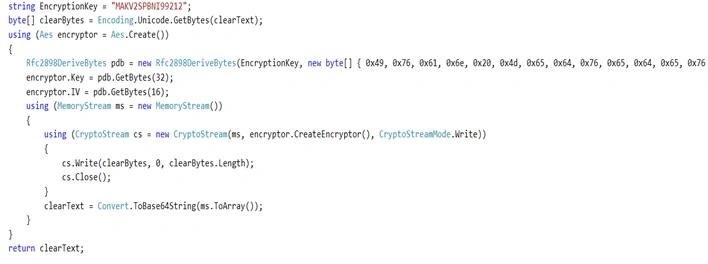
This method transforms the input byte array into an encrypted byte array by applying the private key and the initialization vector.This is finally converted into a Base64String and returns the encrypted string to the calling method.
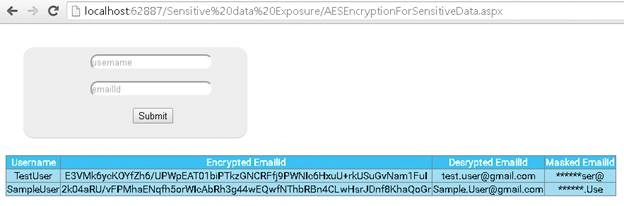
Here, we finally got both Hashed and Decrypted format, as shown below:
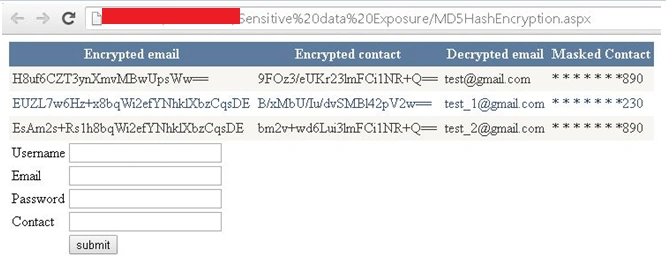
While decrypting the contact number, we are exposing only the last three letters for the contact number under "Masked Contact" field.
Performance and Security Comparison of MD5 and SHA1

Vignesh ManiPosted Jul 8, 2016, 8:26 AM
Nice
Piyush MahurkarPosted Jul 8, 2016, 6:51 AM
Nice one most imp
kalu singh raoPosted Jul 7, 2016, 2:17 PM
Nice...